openstatus: six Docker images, three Compose files, and no release tags
🫖 Status page with uptime monitoring & API monitoring as code 🫖
At a glance
- What is it?
- openstatus is an AGPL-3.0 status page and uptime monitoring platform where monitors, status pages, and notification channels are declared in YAML or Terraform. Reading the repository and the Compose files shows what a self-hosted deployment costs you in services, memory ceilings, and pinning decisions.
- Who is it for?
- openstatus fits a team that wants its status page and its uptime checks declared in the same Terraform or YAML it already reviews, and that accepts operating six containers plus libsql and Tinybird itself. It does not fit a team that wants one container or a tagged release to pin.
- Can I use it commercially?
- Yes, with strict conditions. AGPL-3.0 is a network copyleft licence: if people use a modified version over a network, for example as a hosted service, you must offer them its source code under the same licence.
- Is it still maintained?
- Yes. The repository last received commits 2 days ago.
- What is it written in?
- Mainly TypeScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 13, 2026, and from our analysis. They are not legal advice.
Star history
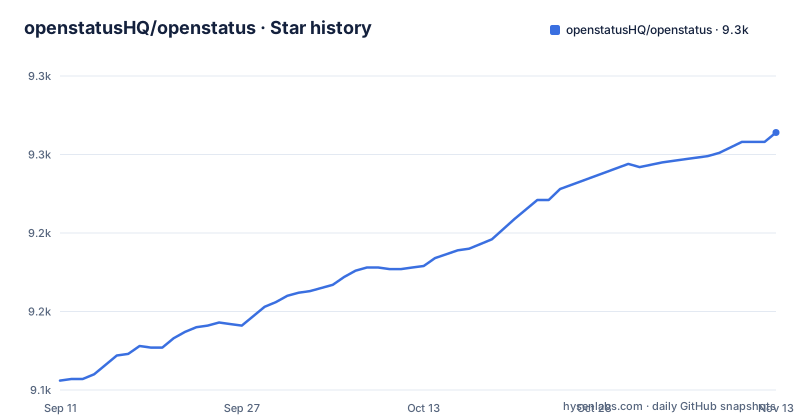
- openstatusHQ/openstatus9,264 ★ · +158
| Repository | 2026-09-11 | 2026-11-13 |
|---|---|---|
| openstatusHQ/openstatus | 9.1k | 9.3k |
158 Stars in the last 63 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
docker compose up -d serves the dashboard on 3002 and status pages on 3003
The documented first run copies an example environment file and starts everything with Compose:
# 1. Copy environment file
cp .env.docker.example .env.docker

# 2. Start all services
docker compose up -d

# 3. Access the application
open http://localhost:3002  # Dashboard
open http://localhost:3003  # Status Pages
The dashboard answers on port 3002 and the public status pages on port 3003. This is the route the README calls fastest for both development and self-hosting, with DOCKER.md holding the long version. A lighter stack sits beside the full one in the repository, .env.docker-lightweight.example paired with docker-compose-lightweight.yaml, and a third file, docker-compose.github-packages.yaml, exists for pulling images from GitHub Packages instead of building them. Three Compose files means three different shapes of the same system.
Six ghcr images, a libsql capped at 512M, and an amd64 pin
The self-hosting guide lists what you are actually deploying:
ghcr.io/openstatushq/openstatus-server:latest
ghcr.io/openstatushq/openstatus-dashboard:latest
ghcr.io/openstatushq/openstatus-workflows:latest
ghcr.io/openstatushq/openstatus-private-location:latest
ghcr.io/openstatushq/openstatus-status-page:latest
ghcr.io/openstatushq/openstatus-checker:latest
Server, dashboard, workflows, private location, status page, checker: six images, every one tagged latest, and none of them the whole product. The private location image is the 8.5MB one, and it is what runs checks from inside your own network. A deployment target therefore needs several services wired together rather than a single image to point at, and whoever maintains that target keeps all six in step. The routes on offer are equally spread out: COOLIFY_DEPLOYMENT.md, COOLIFY_SETUP.md, and COOLIFY_ENVIRONMENT_GUIDE.md, a .koyebignore, a .stacked.toml, a coolify-deployment.yaml, and a charts/ directory. Railway works differently, with a template that puts the dashboard, status pages, API, workflows, probes, libSQL, and Tinybird Local into one project and whose source lives in a separate repository, ephraimduncan/openstatus-railway.
The Compose file adds the ceilings. The libsql service publishes ports 8080 and 5001, sets SQLD_MAX_CONCURRENT_CONNECTIONS=512 and SQLD_MAX_CONCURRENT_REQUESTS=1024, carries a memswap_limit of 512M with a 256M reservation, and health checks every 10s with a 5s timeout, 5 retries, and a 10s start period using a Perl socket opened against 127.0.0.1:8080. The tinybird-local service listens on 7181 with COMPATIBILITY_MODE=1 and is pinned with platform: linux/amd64. So the memory number is a ceiling rather than a preference, and the amd64 pin means the analytics container runs under emulation on Apple Silicon and on arm64 hosts.
pnpm, Deno, and Bun all have a foot in the same workspace
The root package.json names [email protected] as the packageManager and turbo 2.11.2 as the task runner, across workspaces at apps/*, packages/**/*, and packages/config/*. The stated manual setup prerequisites are Node.js, pnpm, and the Turso CLI. Bun appears alongside them, with a bunfig.toml at the root, and the env script is written as bun env.ts.
What that costs a contributor is attention rather than disk space. The documented way to run the status page app or the marketing site is to install dependencies with pnpm and then start one filtered task:
pnpm install
pnpm -w dev:status-page
The dashboard has its own filter, dev:dashboard, and the marketing site is dev:web, each one also pulling in packages/db. The env script runs under Bun instead, so knowing which one owns a given command takes a look at the package.json first. devbox.json is in the root for anyone who would rather have the toolchain pinned by somebody else.
One key spans the API, the CLI, Terraform and the MCP server
The dashboard is not a private surface. Four entry points share a single API key: a typed JSON over HTTP API built on ConnectRPC with a Node SDK beside it, a CLI that is interactive for a person and takes --json when an agent drives it, a Terraform provider written as HCL for monitors, notifications, and status pages, and an MCP server for Claude, ChatGPT, Cursor, or any MCP client. Resources are declared in YAML or Terraform and applied from the CLI or CI, which is the infra as code premise rather than a slogan bolted on afterwards.
Key scopes are the part to read twice: read-only or read-write, with every mutation written to the audit log. Hand a read-write key to an MCP client and an assistant can change monitors and status pages, not only read them, and the audit log is the record of what it changed after the fact. Status pages themselves take custom domains, password protection, maintenance windows, and subscriber notifications by email and RSS.
Incidents travel open, mitigated, resolved with a commander attached
Incident handling is where this stops being a monitoring ping. From the dashboard you declare an incident, set its severity to critical, major, or minor, assign a commander, and move it from open to mitigated to resolved, with every change landing on the incident timeline. The same operations exist in Slack: mention the openstatus agent to declare, update, resolve, or add notes, and bind an incident to a channel so coordination stays in one place. A status report can be linked to an incident, which is how a subscriber learns what the team is working on. Because the incident tools are also on the MCP server, Claude, ChatGPT, or Cursor can drive the same transitions, which changes who is allowed to move an incident and not only how.
The README's incident section lists severity levels, a commander, and a timeline; it does not cover roles, permissions, or an approval step for incident state changes, so check the documentation before assuming who may declare or resolve.
The Go checker sits outside the TypeScript services
The stack is split by language and by job: Next.js for the dashboard, Hono for the API server, Go for the checker, Turso as the database with Drizzle as the ORM, Tinybird for analytics, Tailwind CSS for styling, and shadcn/ui for components. The checker being Go means the code that decides whether your endpoint answered is not TypeScript, and it ships as its own image, openstatus-checker.
Status pages and monitoring are deliberately one tool here, and the README says so without hedging: no need to wire up a separate monitoring service.
Alerts leave through Slack, Discord, PagerDuty and email, with no escalation documented
A monitor that is down or slow notifies through Slack, Discord, PagerDuty, email, and other channels, and incident subscribers are reached by email, RSS, and webhooks. Those channels are declared in the same YAML or Terraform as the monitors themselves, so channel configuration is versioned alongside monitoring configuration and arrives through the same apply step rather than through a settings screen nobody reviews.
Checks run from 28 global regions across 3 cloud providers. Escalation policies, alert deduplication, grouping and on-call schedules are not part of the README's feature list, so check the documentation before you rely on a page reaching a human at 3am.
No release tags means latest is the only channel you get
The repository has no GitHub releases, which is the first fact to settle before self-hosting: there is no version list, no tag to read a changelog against, and no stable channel. The default branch main took a push on 2026-11-01, so work lands there continuously, and the images in the self-hosting guide are all tagged latest. A deployment that pulls ghcr.io/openstatushq/openstatus-server:latest will therefore change underneath you, and the only stable choices are pinning a commit or building the images yourself.
The same repository is written for people who work in it. CONTRIBUTING.md exists, AGENTS.md and CLAUDE.md sit at the root next to a .claude/ directory, and the verify script chains format:check, check:docs, and check, where check:docs runs node scripts/check-doc-refs.mts to catch documentation links that stopped resolving. Tests run through turbo as well. That is a working contributor setup, and it is not a release process.
Editorial conclusion
openstatus fits a team that wants its status page and its uptime checks declared in the same Terraform or YAML it already reviews, and that accepts operating six containers plus libsql and Tinybird itself. It does not fit a team that wants one container or a tagged release to pin. Before you point anything at it, check what your license obligations are under AGPL-3.0, how many images your target actually runs, and which commit your dashboard is serving.
Frequently asked questions
What is openstatus?
It is an open source uptime monitoring and status page platform built for infra as code, released under AGPL-3.0. Monitors, status pages, and notification channels are declared in YAML or Terraform, applied from the CLI or CI, and operable from Claude, ChatGPT, or Cursor over MCP.
What is the best self-hosted status page tool?
openstatus is self-hostable under AGPL-3.0, with pre-built Docker images listed for Coolify, a one-click Railway template that covers the dashboard, status pages, API, workflows, probes, libSQL, and Tinybird Local, and a manual path needing Node.js, pnpm, and the Turso CLI. The README does not rank itself against any other tool.
How does openstatus compare to uptime kuma?
The README does not mention Uptime Kuma at all. What it states about itself is that status pages and uptime monitoring live in one tool with no separate monitoring service to wire up, that it checks from 28 global regions across 3 cloud providers, and that private locations run in a single 8.5MB Docker image.
Is openstatus an open source website monitoring tool?
Yes. It monitors servers, websites, and APIs from 28 regions across multiple cloud providers, notifies through Slack, Discord, PagerDuty, email, and more, and carries status pages with custom domains, password protection, and maintenance windows in the same project.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/openstatushq-openstatus)Star history chart for your README
[](https://hysenlabs.com/projects/openstatushq-openstatus)Was this useful?