kmon spends its front page on kernel theory and its runtime image on dev packages
Linux Kernel Manager and Activity Monitor 🐧💻
At a glance
- What is it?
- kmon is a Rust text user interface for managing kernel modules and watching kernel messages. Three quarters of its README is an explanation of what a kernel and a loadable module are, its Dockerfile installs development headers into the runtime stage with package signature checking relaxed, and the crate package excludes the example module the README teaches from.
- Who is it for?
- kmon is worth installing if you manage kernel modules by hand and want dmesg plus module control in one window, since that gathering is the stated purpose and it is small, with nine dependencies all pinned exactly. Two things to check if you plan to use the container rather than a package.
- Can I use it commercially?
- Yes, with conditions. GPL-3.0 is a copyleft licence: if you distribute software that includes it, you must release that software's source code under the same licence. Running it internally without distributing it does not trigger that obligation.
- Is it still maintained?
- Yes. The repository last received commits 62 days ago.
- What is it written in?
- Mainly Rust, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 21, 2026, and from our analysis. They are not legal advice.
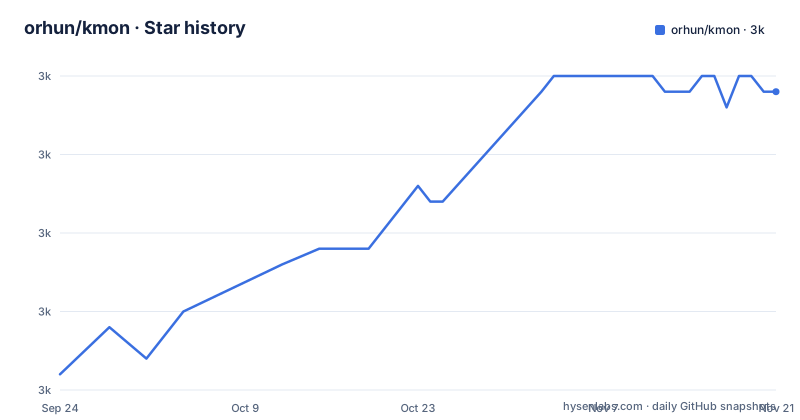
Star history
- orhun/kmon2,969 ★ · +18
| Repository | 2026-09-24 | 2026-11-21 |
|---|---|---|
| orhun/kmon | 3k | 3k |
18 Stars in the last 58 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Three quarters of the front page is a kernel tutorial
Read this readme top to bottom and the tool arrives late. The first paragraphs explain what a kernel is, what a system call is, why user space and protected kernel space are separated, and what the point of that separation is. Then comes a survey of kernel designs, contrasting monolithic kernels that run everything in one address space for speed against microkernels that split spaces for modularity, with hybrid, nanokernel and exkernel mentioned in passing. Then Linux specifically, its history, its footprint and complexity relative to other designs, and how loadable modules extend it at runtime without a reboot. Only after all of that does kmon get described, in a single paragraph, as a text interface for loading, unloading, blacklisting and inspecting modules. That is a deliberate on-ramp rather than a mistake, and it is the clearest example in this batch of a project choosing to teach before it sells.
The example module is built and loaded with four commands
The tutorial arrives at a worked example, and the example is a small C module that prints a message when it is loaded and again when it is unloaded. Its lifecycle is four commands:
make                         # build
sudo make install            # install
sudo modprobe lkm_example    # load
sudo modprobe -r lkm_example # unload
Three of the four need root, which is the point the tutorial is making: module operations are privileged, so the tools that wrap them are. The readme also names the cheaper alternative, saying that a different pair of commands is used for modules independently of the module loader and without requiring an installation into the versioned modules directory, which it names with a command substitution on the running kernel's release string. The message buffer retrieval command is then named, and the expected output is given with two kernel timestamps, one for the load and one for the unload.
The Dockerfile installs dev packages into the runtime stage
The container is a two stage build and the second stage is where the problems are. Both stages install the same three graphics development packages: shape, xfixes and keyboard common, all with the dev suffix. Those are headers and link-time libraries, and the runtime stage does not need them to run a binary that was already linked. Both stages also pass a flag that allows unauthenticated packages to apt, which relaxes the signature checking apt would otherwise apply to that install transaction. So the runtime image is a development image: it carries build-time headers nobody will compile against and installs packages without the verification you would normally get. Neither is a vulnerability in itself, and neither affects the crate you install from a package manager; both matter if you run the image somewhere it matters.
Both stages are Debian Buster and the builder is an old Rust
The runtime stage is Debian Buster slim, and the builder stage is a Rust image whose own base is Buster slim. Buster is Debian 10, released in 2019 and no longer receiving support. So a repository whose last push is dated 2026-09-21 and whose newest release is from December 2024 ships a container on a distribution generation that has been superseded twice over. The builder pins its Rust version exactly, which is good practice for reproducibility, and the same file uses a lowercase as for both stage aliases where the convention is uppercase. Nothing here prevents the build from working; it is the age of the underlying distribution that is worth knowing, because a base image that long out of support will not receive the fixes its packages need.
Nine dependencies all pinned exactly with one engine turned off
The dependency list is short and every entry is an exact version rather than a range, which means an update is a deliberate act. The interface is built on a terminal UI library with its default features switched off and only the termion backend enabled, so the alternative backends it supports by default are compiled out. The backend itself is then pinned directly. Around that: a byte size formatter for the memory column, a character width library for box drawing with wide characters, a colour system conversion library, an enum iterator library, an argument parser, a clipboard extension that depends on an external command, and a lightweight regular expression engine rather than the full one. That last choice is a footprint decision, and paired with the disabled default features it says the author optimised for a small binary rather than for feature reach.
Panics abort and the release build is a single codegen unit
Two build profiles are configured in detail and both matter for how the binary behaves. Both the development and the release profile set panic behaviour to abort, so a panic terminates the process rather than unwinding. For a terminal interface that reads kernel messages that is a defensible choice, since there is nothing to unwind to and a clean exit is easier to reason about than a half unwound stack. The release profile then optimises at level three with link time optimisation enabled and the codegen unit count set to one, which is the slowest and most thorough combination available. The development profile is the opposite, unoptimised with debug information on. The bench profile optimises at level three without the link time optimisation.
The man page and shell completions are build artefacts
There are three build dependencies and none of them are part of the program. One generates the manual page from the argument parser's definitions. One generates shell completions from the same definitions. The third is the argument parser itself, repeated so the build can use it. Since there is a build script at the repository root, the manual page and the completion files are produced when you compile rather than being checked in. That is the right arrangement, because it means they cannot drift from the flags the program actually accepts, and it also means a distributor packaging the binary gets documentation and completions for free from the same source of truth. The argument parser appears on both sides, once as a runtime dependency and once as a build dependency, at the same pinned version.
The published crate excludes the example the README teaches from
The package manifest has an explicit include list, and it is short: the source directory, the two cargo files, the licence, the readme, and the changelog. Everything else in the repository is left out of the crate, including the example directory that holds the sample module's source and its makefile, and including the release notes file and the site configuration. So a reader who installs the tool from a package manager and then follows the tutorial has to clone the repository to get the module the tutorial is about. That is a small, deliberate trade, and it keeps the crate small, but it is the kind of detail that makes the difference between a tutorial you can follow and one you have to go find. The same include list is why the crate carries the changelog but not the release process documentation.
Editorial conclusion
kmon is worth installing if you manage kernel modules by hand and want dmesg plus module control in one window, since that gathering is the stated purpose and it is small, with nine dependencies all pinned exactly. Two things to check if you plan to use the container rather than a package. The runtime stage installs development headers it does not need and relaxes package signature checking during install, so treat the image as a development convenience rather than something to run in production. And if you want the sample kernel module the README walks through, clone the repository rather than relying on the crate, because the package manifest excludes the example directory.
Frequently asked questions
What is kmon used for?
It is a text-based user interface for managing Linux kernel modules and monitoring kernel activity. Managing means loading, unloading, blacklisting, and showing information about a module; monitoring means tracking module changes and kernel messages in real time. The stated aim is to gather the module and message buffer tools into a single terminal window.
How do I install kmon?
Six channels are documented: Cargo, the Arch Linux package, Nixpkgs, Alpine Linux, Docker, and a manual build. The crate is published on crates.io, and the project is also packaged in Arch Linux's extra repository. Building from source needs a Rust toolchain, and the container route is a two stage Dockerfile.
Does kmon need root to manage modules?
Loading and unloading kernel modules does, which the readme demonstrates with a worked example: build, install, load, unload, where three of the four commands are run with elevated privileges. The readme also names an alternative pair of commands for modules that works independently of the module loader and without installing into the versioned modules directory.
What are kmon's dependencies?
Nine, each pinned to an exact version: a terminal UI library with its default features disabled and only one backend enabled, that backend directly, a byte size formatter, a character width library, a colour conversion library, an enum iterator, an argument parser, a clipboard extension, and a lightweight regular expression engine rather than the full one. Three more build dependencies generate the manual page and shell completions.
Is the kmon Docker image suitable for production?
Treat it as a development convenience. Both of its stages install three graphics development packages that the runtime does not need to execute an already linked binary, both pass a flag that relaxes package signature checking during the install, and both are based on a Debian generation that has been superseded twice. The released packages, rather than the image, are the safer route.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/orhun-kmon)Star history chart for your README
[](https://hysenlabs.com/projects/orhun-kmon)Was this useful?