LitePan: the Go rewrite, and the latest tag still points at the Python version
LitePan: aggregated mounting for multiple cloud drives, supporting WebDAV, STRM, media organization, local mounting and chained tasks.
At a glance
- What is it?
- A Go rewrite of a multi-storage aggregator that mounts several cloud drives behind one interface, serves them over WebDAV and FUSE, and writes .strm files for Emby and Jellyfin. It is licensed for non-commercial use only, ships with a default admin password, and its compose file asks for a privileged container in the host process namespace.
- Who is it for?
- LitePan fits someone who has several storage services, wants them behind one WebDAV or FUSE mount, and wants media libraries generated rather than curated by hand, and who is using it for personal purposes. It does not fit a commercial deployment, and the licence is explicit about that.
- Can I use it commercially?
- Check first. The repository uses a licence we do not classify automatically, so read its LICENSE file before any commercial use.
- Is it still maintained?
- Yes. The repository last received commits 44 days ago.
- What is it written in?
- Mainly Go, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
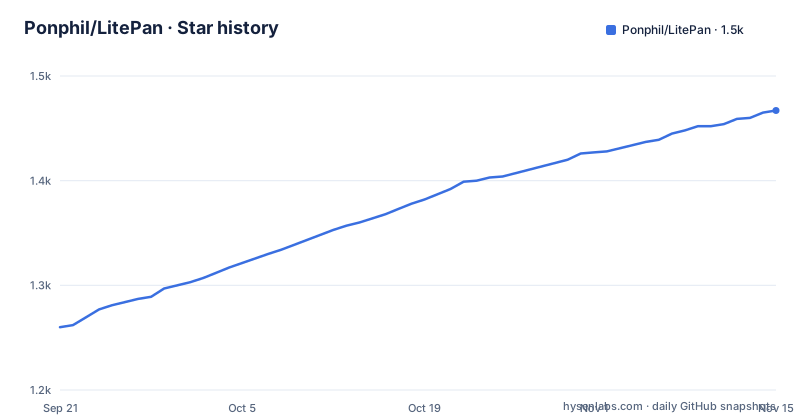
- Ponphil/LitePan1,467 ★ · +207
| Repository | 2026-09-21 | 2026-11-15 |
|---|---|---|
| Ponphil/LitePan | 1.3k | 1.5k |
207 Stars in the last 55 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The latest tag still points at the previous Python build
Two admonitions sit at the top of the README, and the second one is the kind that saves an afternoon.
The first says the current repository is the Go version of LitePan, still in development, that the first release may have many problems, and that it should be tested carefully. The Python version has been archived to a separate repository.
The second is a warning about container tags. Deploying the latest tag for this repository is explicitly discouraged, because the latest tag is still the old Python image. If you need the old program and its compose scripts, the README sends you to the archived repository. What you should use instead is the beta tag or a specific version tag such as the one named in the version badge.
So the image names in this project have two generations behind them, and the one most people type first points at the wrong thing.
There are no GitHub releases to make the version discoverable, so the badge is the version of record: v0.5.7-Beta, with the word Beta attached to the number. The last commit on the default branch is dated 2026-10-02, so the tree is moving faster than the tagged images.
For anyone migrating from the Python version, that means the compose file in this repository and the compose file in the archive are not interchangeable, and the image names differ between them.
A non-commercial licence, and metadata that does not say so
The licence section is short and its message is unambiguous. The project uses version 1.0.0 of the PolyForm Noncommercial licence, which covers personal study and non-commercial use, and commercial use is prohibited.
That is not an open source licence. It is source-available with a use restriction, and the difference matters for anything other than personal use: a company, a paid service, or a project with a budget cannot adopt it under those terms without a separate arrangement.
The repository's own licence metadata carries no recognised identifier, so the licence field on the repository page does not tell you any of this. What tells you is the README section and the licence file at the root, and the badge in the header renders the licence name so a reader scanning the top of the page sees it.
Two related lines complete the picture. Third-party dependencies are listed in a separate notices file, which is the right arrangement given how many storage and networking libraries this project pulls in. And the README asks users to comply with each storage service's terms and with local law, which is the correct disclaimer for a tool that automates access to third-party accounts.
For a project whose feature list includes instant cross-account uploads, that last line is doing real work: automating a provider's upload endpoint is exactly where a provider's terms tend to be specific.
Default admin password admin, privileged container, host process namespace
The quick start publishes a compose file, and three lines in it deserve attention before anyone copies it.
services:
  litepan:
    image: ponphil/litepan:beta
    container_name: litepan
    restart: unless-stopped
    ports:
      - "5211:5211"
      - "42069:42069/tcp"
      - "42069:42069/udp"
    devices:
      - /dev/fuse:/dev/fuse
    pid: "host"
    privileged: true
The service listens on port 5211, and the README states the default administrator password is admin. There is no first-run prompt described, so the first person to reach that interface on the network has the credentials.
Second, the container requests privileged mode, joins the host process namespace, and has the FUSE device mapped in. All three are explained by the FUSE mounting feature, and they are also the combination that gives a container the widest possible access to the machine. The image works around the user restriction by enabling the allow-other option in the FUSE configuration file at build time.
Third, the file publishes a second port for both TCP and UDP, described as the listener for the built-in magnet support, covering the peer-to-peer protocols including the distributed hash table. The comment next to it warns that if the port is changed in the backend, the mapping has to be changed to match.
That warning is worth pausing on, because a peer-to-peer listener is not inert. Enabling it means the container participates in that network, and doing so by default rather than by an explicit switch is a decision the operator inherits from the compose file.
The frontend is compiled into the Go binary
The container build has three stages, and the middle one explains the deployment shape.
The first stage builds the web interface with Node, running a type check and a production build. The second stage is the Go build, and it copies the built frontend out of the first stage into a directory inside the Go source tree. The binary is then compiled with path trimming and stripped symbols, which means the interface ends up embedded in the executable rather than served from a separate file tree.
The result is a single file to run, with the interface inside it, which is the right shape for a container image and for a single-binary release. The interface is also type-checked in the build, so a broken web build fails the image rather than shipping.
The runtime stage is Debian slim with certificate and time zone data plus the FUSE package, and it declares four environment variables for the data directory, the output directory for generated files, the listen address and the log level.
Two build settings are worth noticing because they say who this is built for. The npm registry is set to a regional mirror, the Go proxy is set to a regional mirror with a direct fallback, and the toolchain download is explicitly disabled with a comment explaining that this avoids failures when the default module proxy is unreachable. All three are consistent with a project developed on a network where the default hosts are unreliable.
FUSE is a build tag, and the default container platform is amd64
The Makefile shows that FUSE support is optional at compile time. There is a build target that passes a FUSE tag and a target named for building without it, so the same source produces either a binary that can mount or one that cannot.
That choice has a consequence for the feature list, since local mounting is one of the advertised capabilities. A binary built without the tag still serves WebDAV; it just cannot do the filesystem mounting. The compose file requests the device regardless.
The rest of the tooling is disciplined. Linting runs through a configuration file at the root with the linter version pinned and the executable resolved either from the path or from the Go workspace directory. Tests run with the race detector. Every Go command is invoked with workspace mode switched off, which means a stray workspace file on the machine cannot change what the build sees.
There is also a target that builds the image, brings the compose project up or down, and one that exports the built image to a compressed archive for transfer to another machine, which is the usual path onto a NAS that cannot pull from a registry.
The one setting that will bite an owner of consumer NAS hardware is the default container platform, which is amd64. Most such devices are arm64, so a build or export needs the platform overridden, and the repository ships a second compose file for one NAS operating system to go with it.
The dependency list is a map of what the program actually does
There is no architecture document in the root, so the module file is the place to read for what this program is made of.
The module declares a recent Go language version and a small set of direct dependencies. A peer-to-peer torrent library and a distributed hash table implementation are there, which explains the magnet support, the second published port and the offline download feature. A FUSE library explains the local mounting. A WebDAV server library explains the WebDAV surface. A QR code library is present, which in this context usually means a device-authorisation login flow for a storage provider rather than a user-facing feature.
A router library handles the HTTP layer, a filesystem notification library watches paths, a UUID library exists because storage providers key on account identifiers, and the SQLite driver is the pure-Go implementation rather than a binding, which is why the container build can disable cgo entirely and produce a static binary.
The direct list is thirteen entries. The indirect list underneath is long and dominated by the peer-to-peer stack, which is what it usually looks like when a torrent client is a direct dependency.
One inconsistency: a comment in the build file says the Go version there is aligned with the language version declared in the module file and quotes a slightly older number than the module file actually declares. The intent is documented, the specific number has drifted.
Public pull requests are not accepted
The contribution model is the opposite of what a repository with a contributing guide usually has.
The feedback section says to get in touch through the author's video channel page, states that public pull requests are not accepted for now, and asks anyone who wants to help maintain the project to send a private message instead. External contributions are acknowledged in a separate file at the root.
So there is no issue tracker workflow, no review queue and no branch protection to speak of, and a first-time contributor has to start a private conversation. For a project in its first release of a language rewrite, that is a defensible choice: reviewing outside pull requests from people who have not learned the codebase yet costs more than it returns.
It does mean the project has a single point of contact for everything except code already inside the repository, which is worth knowing before you plan to depend on it.
The rest of the repository follows the shape the module file implies: a command directory for the entry point, a drivers directory for the per-provider integrations, internal and public package directories, a web directory for the frontend, and a documentation directory. Alongside those sit the lint configuration, the notices file for third-party code, a second compose file for a NAS operating system, and a Makefile that builds, tests and exports.
Editorial conclusion
LitePan fits someone who has several storage services, wants them behind one WebDAV or FUSE mount, and wants media libraries generated rather than curated by hand, and who is using it for personal purposes. It does not fit a commercial deployment, and the licence is explicit about that. Verify four things before you deploy it. Read the licence before anything else, because it is a non-commercial licence rather than an open source one, the repository's licence metadata carries no recognised identifier, and the README asks you to respect each storage provider's terms separately. Use the beta tag or a specific version tag, not the latest tag, which the README says still points at the previous Python image. Change the default administrator password, which is documented as admin. And read the compose file before running it, since it requests privileged mode, the host process namespace and the FUSE device, and it publishes a peer-to-peer network listener on a second port. Public pull requests are not accepted, so plan to report problems through the author's video channel rather than a repository issue. There are no GitHub releases, the version is carried in a badge as v0.5.7-Beta, and the last commit is dated 2026-10-02.
Frequently asked questions
What is LitePan?
A Go rewrite of a multi-storage aggregator that mounts several cloud drive services behind one interface, serves them over WebDAV and FUSE, generates .strm links with metadata for Emby or Jellyfin, organises files using TMDB recognition with a preview before archiving, and chains the organise, generate, scrape and refresh steps together. The Python original now lives in a separate archived repository.
Which Docker image tag should I use for the Go version of LitePan?
The beta tag or a specific version tag such as v0.5.7-Beta. The README carries an explicit warning not to deploy the latest tag for this repository, because latest still points at the old Python image, and sends you to the archived repository if you need that version.
What are LitePan's default credentials and container privileges?
The web interface runs on port 5211 and the default administrator password is documented as admin. The compose file runs the container in privileged mode, in the host process namespace and with the FUSE device mapped, and it publishes a second port for both TCP and UDP for the built-in magnet peer-to-peer listener.
Can I use LitePan commercially?
No. The project is licensed under PolyForm Noncommercial 1.0.0, covering personal study and non-commercial use with commercial use prohibited. The repository's licence metadata carries no recognised identifier, third-party dependencies are listed in a separate notices file, and the README asks users to follow each storage provider's terms and local law.
Can I contribute to LitePan through a pull request?
Not a public one. The README says public pull requests are not accepted for now and asks anyone interested in helping maintain the project to send a private message through the author's video channel page. External contributions that already exist are credited in a separate acknowledgements file.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/ponphil-litepan)Star history chart for your README
[](https://hysenlabs.com/projects/ponphil-litepan)Was this useful?