PrestaShop's develop branch is documented as 9.1 while 9.2.0 is already tagged
PrestaShop is the universal open-source software platform to build your e-commerce solution.
At a glance
- What is it?
- PrestaShop is a self-hosted PHP e-commerce platform whose repository is a development environment rather than a distribution. The practical friction lives in the details: a README that lags its own tags, a container that refuses to reinstall until you delete a config file, development defaults that publish MySQL on a well known password, and a Makefile comment explaining why Ctrl+C does not stop the watcher.
- Who is it for?
- PrestaShop suits a team that wants to own its storefront and will run its own server, PHP and database included. Before starting, resolve the branch question yourself: the default branch is develop, and the README's statement that it targets 9.1 does not match the 9.2.0 tag.
- Can I use it commercially?
- Check first. The repository uses a licence we do not classify automatically, so read its LICENSE file before any commercial use.
- Is it still maintained?
- Yes. The repository last received commits 2 days ago.
- What is it written in?
- Mainly PHP, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
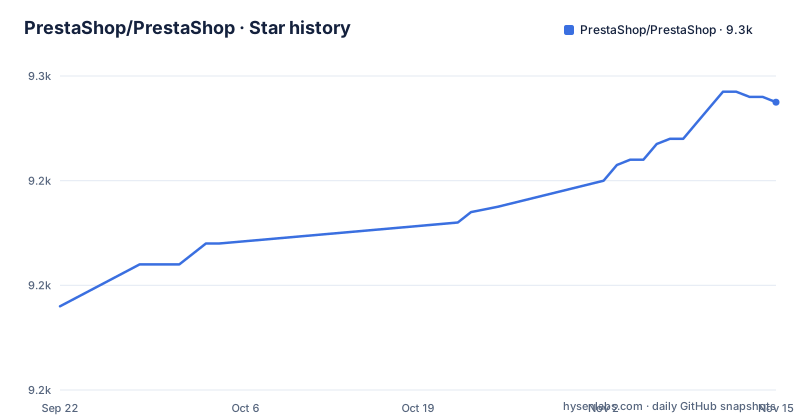
- PrestaShop/PrestaShop9,255 ★ · +39
| Repository | 2026-09-22 | 2026-11-15 |
|---|---|---|
| PrestaShop/PrestaShop | 9.2k | 9.3k |
39 Stars in the last 54 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The README says 9.1 while the 9.2.0 tag already exists
Two statements in the README do not line up with the release history. One says the latest stable public version is currently 9.0 and points to the releases page to download it, and another says the `develop` branch holds work in progress for the next version and is exclusively for 9.1.
The tags say otherwise. PrestaShop 9.2.0 was published on 2026-09-30, an earlier 9.2.0-rc.1 candidate on 2026-09-21, and 9.1.5 on 2026-08-18. So the README is describing a 9.1 line that already has a patch release, while a 9.2 line is out, and it still points new production users at 9.0.
The consequence is concrete for anyone starting work. Clone the repository, read the README, and you have two plausible instructions that contradict each other: the branch you land on is not the branch the README says it is, and the version the README tells you to deploy is behind two others. Nobody can resolve this from the file alone. Check which tags exist against the branch you actually have before writing a single module, because building an extension against the default branch and then deploying 9.0 means the code is written against a version your production install does not have. The same paragraph also carries the one thing that is unambiguous: this repository is for development and preview, and production installs come from the releases page, not from a clone.
app/config/parameters.php decides whether the container reinstalls
The Docker environment will not overwrite an existing installation, and the check is a specific file. Before auto-installing, the container tests whether `app/config/parameters.php` exists on startup. If it does, the install is skipped, which is what protects an existing shop in the workspace. If you expect the container to install or reinstall, you must delete that file first.
The second half of the note is the part that catches people on a shared machine or a mounted volume: the container runs as `www-data`, and that user needs write access to the whole workspace. The compose file passes `USER_ID` and `GROUP_ID` as build arguments, both defaulting to 1000.
Together those two details make reinstalls a manual, deliberate act rather than a state the environment recovers into. If you are iterating on an install, expect to remove the file each time and to check ownership first, otherwise you will lose time to a permission error that looks like a broken image.
The compose file publishes MySQL with a default root password
The database service is exposed to the host and configured with development defaults:
    ports:
      - "${DB_HOST_PORT:-3306}:3306"
    environment:
      MYSQL_ROOT_PASSWORD: ${DB_PASSWD:-prestashop}
      MYSQL_DATABASE: ${DB_NAME:-prestashop}
That reads as `prestashop` for both unless you export `DB_PASSWD` first. The MySQL port is published on the host, so on a machine with a permissive firewall the database is reachable with credentials that are published in a public repository.
The other defaults in the same file are just as revealing, and all of them are development choices. `PS_DEV_MODE` defaults to 1, `PS_ENABLE_SSL` defaults to 0 while ports 8001 and 8002 are still both mapped, `PS_ERASE_DB` defaults to 0, and `PS_USE_DOCKER_MAILDEV` defaults to 1, which is why the quick start lists an email testing service on port 1080. Nothing here is a secret, but the pattern matters: this file is tuned to make a developer's first run work, not to survive contact with a network.
The credentials worth changing before anything else are the admin login and this database password. The compose file accepts overrides for both, and the quick start shows the admin pair explicitly:
export [email protected]
export ADMIN_PASSWD=Your-Secure-Password
docker compose up
The default admin is `[email protected]` with password `Pr3st4Sh0P`. A shop left on that, with its database on port 3306, is reachable by anyone who has read this repository.
Ctrl+C never reaches the watcher running inside the container
The Makefile contains a comment about a behaviour that will otherwise waste an afternoon. When the Makefile detects that compose is running, it re-routes PHP, Composer and Symfony console calls into the container as the `www-data` user, and it sets up the watch targets through `docker exec`. The comment explains the problem: `docker exec` has no signal proxying, so Ctrl+C only reaches the asset watcher through the pty line discipline inside the container.
The workaround is in the same comment. A TTY is allocated whenever one is available to attach, detected by testing whether standard input is a terminal. Without a TTY, which is the case in CI and in IDE task runners, the target falls back to input only. And there the interrupt kills the local client while leaving the watcher running inside the container.
The consequence is orphaned processes. Run a watch target from a terminal and it stops when you expect. Run the same target from a CI job, a task runner, or any piped context, and the watcher survives its parent. If assets are not rebuilding as expected, check for a leftover watcher in the container before touching the build configuration.
The same detection drives everything else in the file, which is worth knowing: whether a command runs on your host or inside the container is decided by whether compose reports a running project, so the behaviour of `make test` and `make assets` changes depending on the environment you invoke them from.
Three static analysis baselines carry the legacy layout
The repository ships four separate PHPStan configuration files, and the names describe the state of the migration rather than a preference for baselines. There is a baseline, a disallowed calls list, and a separate baseline named for a temporary legacy layout. Rector is configured alongside them, as is a PHP CS Fixer distribution file, which points at automated refactoring of existing code rather than a green field codebase.
A baseline file works by recording known violations and suppressing them, so the analysis run passes while the recorded problems remain in the tree. The consequence is that a passing static analysis run tells you nothing about whether the codebase is clean. It tells you no new problem was added since the baseline was recorded. When the disallowed calls list is doing the same job for calls nobody wants to make, the two together describe a codebase being held at a fixed level rather than improved, which is the honest reading of a repository carrying a temporary legacy layout baseline and a refactoring tool at once.
The directory listing explains what the legacy layout is. Several generations of structure sit at the root: `classes/`, `controllers/`, `src/`, `app/`, `config/`, `override/`, `modules/`, `themes/`, `cache/`, `download/`, `localization/`, `mails/`, `pdf/`, `img/` and `js/`. Several of those names predate PSR-4 conventions, and the presence of a disallowed calls list alongside the baselines suggests the project is constraining older patterns as it moves toward the newer layout. If you are writing new code, expect the linters to have opinions about where things live, and read the baseline files before assuming a failure is your mistake.
Instruction files for four coding agents sit at the root
The repository root contains a `.ai/`, a `.claude/`, a `.cursor/` and a `.windsurf/` directory, plus `AGENTS.md`, `CLAUDE.md` and `GEMINI.md`. That is configuration for four different agent tools and three separate instruction files, committed alongside the code.
The project treats this as a supported path rather than an accident. The contributing section tells contributors that if they use AI tools to write code, their agent should read `.ai/CONTEXT.md` first, and it points at a documentation page on AI assisted development in the DevDocs. There is a `package-lock.json` and a `composer.json`, so the front end and the PHP side are both installed from the repository rather than from a global toolchain.
Two consequences follow, and they point in opposite directions. The positive one is that a contributor using an agent has a defined context file to point it at, which is more than most projects offer. The maintenance cost is that the same project knowledge now has several potential homes, and nothing in the layout makes one of them authoritative. If you are an agent or a contributor, read `.ai/CONTEXT.md` as instructed, and check whether the tool specific files agree with it before trusting either. For a project at this size, duplicated instructions across seven locations is the sort of surface that drifts quietly.
Licence metadata reads NOASSERTION beside an OSL3 header stamp
The repository metadata does not resolve to a licence identifier. It reports NOASSERTION, while the root contains a `LICENSE.md` file and a configuration named `.header-stamp-config.yml` paired with a file called `.header-stamp-osl3-license.txt`. The tooling therefore sees an unasserted licence, and the files on disk carry a notice referring to OSL3.
The header stamp mechanism is the important part. A stamp config plus a notice file means every file in the tree gets its licence header written or checked automatically, which is a stronger guarantee than a single licence file alone for code that gets copied into modules and forks. But an unasserted SPDX identifier defeats the automatic half of the ecosystem. Dependency scanners, package registries and compliance tooling that read repository metadata will report no licence rather than the one the headers carry.
The consequence for a reader is that you cannot answer the licence question from the metadata and should not try. Read `LICENSE.md` and the header stamp configuration directly, and if you are redistributing code, check what the stamp actually inserts into a file rather than inferring it. Note also that the repository carries `modules/` and `themes/` directories alongside the core, so check the terms of any module or theme you add yourself.
Editorial conclusion
PrestaShop suits a team that wants to own its storefront and will run its own server, PHP and database included. Before starting, resolve the branch question yourself: the default branch is develop, and the README's statement that it targets 9.1 does not match the 9.2.0 tag. Treat the compose file as a development artefact rather than a deployment template, change the admin credentials and the MySQL root password before it reaches any shared host, and read the update guide, which states plainly that switching versions is not trivial.
Frequently asked questions
What language does PrestaShop use?
PrestaShop is written in PHP and needs a web server running PHP 8.1+ with any flavor of MySQL 5.6+, including MySQL, MariaDB or Percona Server, with Apache or Nginx recommended. The Docker development environment builds the same stack with a PHP 8.1 Apache image and a MySQL 8.4 database, and the front end assets are built with Node, pinned to 20.19.5 in the compose build arguments.
how to install prestashop
For a production shop, download the latest stable version from the releases page and follow the user install guide; the repository itself is for development and preview only, and a manual install also needs a database created with an administration tool such as phpMyAdmin. For development, start the Docker environment with `make docker-start`, which serves the front office on port 8001, the back office at localhost:8001/admin-dev and an email catcher on port 1080.
how to access prestashop admin
In the Docker environment the back office is at http://localhost:8001/admin-dev, signed in with [email protected] and the password Pr3st4Sh0P unless you export ADMIN_MAIL and ADMIN_PASSWD before starting. The admin folder in a development checkout is admin-dev rather than the production admin path, and the compose file exposes that as PS_FOLDER_ADMIN, alongside PS_FOLDER_INSTALL which defaults to install-dev.
Is PrestaShop free?
The platform is open source and self-hosted, so there is no licence fee for the software itself, but you supply the infrastructure: your own web server with PHP 8.1+ and a MySQL 5.6+ compatible database.
how to use prestashop
The project points first time users at a Getting Started guide for installation, a User Guide for running the shop, a Merchant's Guide for new sellers and an FAQ page. Operationally, the development environment runs the storefront at localhost:8001, the back office at localhost:8001/admin-dev and mail testing on port 1080, and the updating guide is worth reading first because the project states that switching to a new version is not trivial.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/prestashop-prestashop)Star history chart for your README
[](https://hysenlabs.com/projects/prestashop-prestashop)Was this useful?