The speed comparison dates from January 2024
Private front-end for Reddit
At a glance
- What is it?
- Redlib is a Rust front-end for Reddit that proxies every request, including media, through its own server and ships no JavaScript. Its own performance numbers are two and a half years older than its last commit, and its container image downloads a release tarball instead of building anything.
- Who is it for?
- Redlib fits someone who wants to read Reddit without a Reddit account, without ads, and without their browser talking to Reddit at all, and the container defaults are among the more carefully locked down in self-hosted software. Three things to check before you point your bookmarks at it.
- Can I use it commercially?
- Yes, with strict conditions. AGPL-3.0 is a network copyleft licence: if people use a modified version over a network, for example as a hosted service, you must offer them its source code under the same licence.
- Is it still maintained?
- Yes. The repository last received commits 24 days ago.
- What is it written in?
- Mainly Rust, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
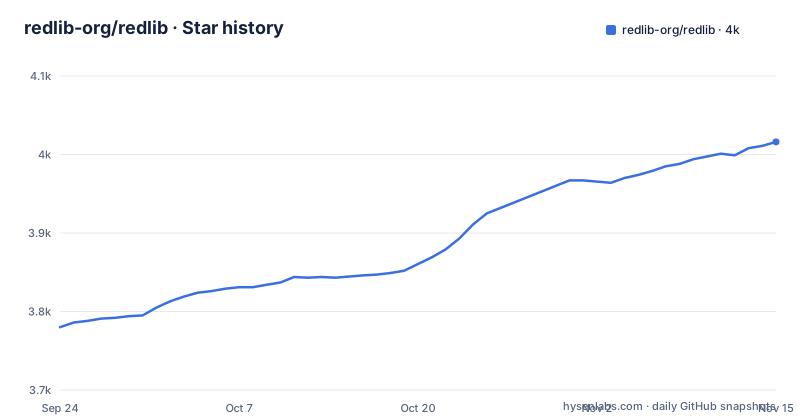
- redlib-org/redlib4,016 ★ · +236
| Repository | 2026-09-24 | 2026-11-15 |
|---|---|---|
| redlib-org/redlib | 3.8k | 4k |
236 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The performance table says last tested on January 12, 2024
The comparison section puts Redlib next to Reddit using Google PageSpeed Insights, with a Redlib report link and a Reddit report link, and it is three rows long: Speed Index 0.6s against 1.9s, Performance Score 100% against 64%, and Time to Interactive 2.8s against 12.4s. Above the table is the date, Last tested on January 12, 2024. That is the honest part of the section, since a dated measurement can be judged. What follows is that the newest release is v0.36.0 from 2025-03-20 and the most recent push to master is dated 2026-04-24, so the table describes a build more than two years older than the current branch. The figures also come from one instance, redlib.matthew.science, which is one of the maintainers' own, rather than from a sample of instances.
The Docker image downloads a release instead of building
The container image in this repository does not compile Redlib. It starts from alpine:3.19, installs curl, and then fetches a tarball from the project's releases page and unpacks it into the binary directory:
RUN curl -L "https://github.com/redlib-org/redlib/releases/latest/download/redlib-${TARGET}.tar.gz" | \
    tar xz -C /usr/local/bin/
The word latest in that URL is the consequence. An image built today contains the newest release at build time, and an image rebuilt next month contains a different one, with nothing in the Dockerfile changing. It also means the build depends on the release hosting staying reachable and on the download succeeding at build time rather than at runtime. After the download the file creates a user with a home directory of /nonexistent, no create-home flag and a disabled password, switches to it, exposes 8080, and sets a health check that fetches the settings page once a minute.
The compose file hardens everything and comments out seccomp
The deployment file is short and almost every line is a restriction. The service runs as user nobody, with read_only enabled, with every capability dropped, with no-new-privileges in the security options, and attached to its own named network rather than the default one. Only port 8080 is published, with a comment saying to specify 127.0.0.1:8080:8080 instead if you are using a reverse proxy. Configuration comes from an .env file through env_file. What is commented out is the interesting part: the line `# - seccomp=seccomp-redlib.json` sits directly under the no-new-privileges line, and the repository does ship that profile at its root. So the strictest of the available controls is present, documented by a file that is in the tree, and left for the operator to switch on.
Two health checks with different intervals
There are two health checks in this repository and they disagree. The image defines one with a one minute interval and a three second timeout, using wget in spider mode against the settings page on port 8080. The compose file defines another with a five minute interval and the same three second timeout, against the same URL. Because compose replaces whatever the image declared, a deployment that runs compose gets the five minute version, and a bare run of the built image gets the one minute version. The URL is worth noting as well: it probes the settings page, which is the one endpoint that renders without calling Reddit, so the check stays meaningful when the upstream is unreachable.
Twenty instance-wide defaults, including NSFW and subscriptions
The environment example separates four instance settings from a much longer list of default user settings, and the second list is where the judgement calls are. An operator can turn on SFW-only mode, set a banner, disable search engine indexing, and point the removed-post feature at a different host. Then there are the defaults every visitor inherits: theme, front page, layout, wide mode, post sort, comment sort, blurring spoiler content, showing NSFW content, blurring NSFW content, using HLS video format, hiding the HLS notification, autoplay, awards, the sidebar, a preset subscription list and a preset filter list, where both of those are written in a sub1+sub2+sub3 format. Twelve themes are offered. The theme default is system and the layout default is card, so an operator who changes nothing gets the card layout in the visitor's own colour scheme.
Removed posts come from a third-party host by default
One setting names an external service in the shipped default: REDLIB_PUSHSHIFT_FRONTEND is set to undelete.pullpush.io, with a comment saying to set the Pushshift frontend for removed links. Pushshift was the archive that Reddit acquired, and the replacement named here is a third-party host, so an instance that leaves the default is asking that host for content on behalf of every visitor who opens a removed link. Nothing else in the environment file points outward. That makes this single line the one to change before exposing an instance publicly, and it is easy to miss because it sits in the instance block above twenty lines of theme and sort defaults that look more configurable and matter less.
A release candidate sits beside hyper 0.14
The manifest is worth reading for the odd entries. The HTTP server is hyper at 0.14.31, the pre-1.x line of a project whose later versions moved on, while the async runtime is tokio at 1.44.2 with its full feature set. One dependency is pinned to a release candidate, wreq at 6.0.0-rc.28, which means a build can change under you when that crate publishes its final release. Two entries relate to the client spoofing the README describes: a crate named fake_user_agent, and the OAuth and token refresh logic. Three more, base2048, build_html and htmlescape, appear together with arc-swap, which is an unusual cluster for a Reddit front-end. The template engine is Askama with derived templates, the assets are compiled in with rust-embed, and dotenvy loads the environment file.
The name change was a legal constraint
The project is a fork of Libreddit, and the README explains both the name and the differences. The name Redlib was adopted to avoid legal issues, as Reddit only allows the use of their name if structured as XYZ For Reddit. Three technical improvements are listed. OAuth token spoofing is used to circumvent rate limits imposed by Reddit by mimicking the most common iOS and Android clients, and the file is specific about the choice: both were explored, but only the Android client was selected, due to content restrictions when using an anonymous iOS client. The authentication token is refreshed every 24 hours to emulate the official Android app, and efforts are made to send as many of the official app's headers as possible to reduce the likelihood of a crackdown. Each of those three is a deliberate impersonation of an official client, which is the part to weigh before running it.
Editorial conclusion
Redlib fits someone who wants to read Reddit without a Reddit account, without ads, and without their browser talking to Reddit at all, and the container defaults are among the more carefully locked down in self-hosted software. Three things to check before you point your bookmarks at it. How old your copy is, since the newest release is v0.36.0 from March 2025 while master has moved on since. Which defaults the instance owner set, because twenty of them are instance-wide and include NSFW display and preset subscriptions. And whether the unofficial-client behaviour is acceptable to you, since the README describes spoofing Reddit's Android client to get around rate limits.
Frequently asked questions
Is Redlib safe to use?
The README's privacy section is the answer. All requests are proxied through the server, including media, and a strong Content Security Policy prevents the browser from making requests to Reddit, with no JavaScript, no ads and no tracking. The server logging bullet begins by saying that in production, whether running the binary, hosting with docker or using the official instances, Redlib logs nothi
How do you install Redlib?
The README's deployment section covers several paths: Docker, Docker Compose and the Docker CLI, Podman with Quadlets, the binary run as a systemd service, building from source, Replit, Heroku and Glitch, and launchd on macOS. The compose file pulls quay.io/redlib/redlib, runs it as user nobody with a read-only filesystem and all capabilities dropped, and reads configuration from an .env file.
What is Redlib?
An alternative private front-end to Reddit, written in Rust, with origins in the Libreddit project. It is built on Hyper for HTTP, Askama for templating and Rustls for TLS, implements most of Reddit's signed-out functionality, and was inspired by Invidious, Nitter and Bibliogram for other services.
Why was Libreddit renamed to Redlib?
The README says the name Redlib was adopted to avoid legal issues, since Reddit only allows the use of their name when structured as XYZ For Reddit. It also lists three technical improvements over the fork: OAuth token spoofing of the common Android client to get around Reddit's rate limits, token refreshing every 24 hours, and mimicking the official app's headers.
Is Redlib free to use?
The project is licensed AGPL-3.0-only and self-hosted, and the README states no price for it. A list of public instances is kept in a separate redlib-instances repository in Markdown and JSON, with uptime reported on an Uptime Robot status page.
Official sources
Where developers are discussing it
Posts on Hacker News, dev.to and Lobsters that link to this repository, found by our scan of those communities. 2 in the last 30 days; newest first.
- Redlib discussion: Reddit has decided to force everyone to log inHacker News · Nov 2, 2026 · 5 points · 0 comments
- Tell HN: Reddit JSON endpoints might have been turned offHacker News · Oct 20, 2026 · 8 points · 5 comments
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/redlib-org-redlib)Star history chart for your README
[](https://hysenlabs.com/projects/redlib-org-redlib)Was this useful?