fable-os: an x86_64 kernel with no shell, where the model gets 64 syscalls and a FAT32 disk
An agentic operating system where the kernel is controlled directly by Claude
At a glance
- What is it?
- fable-os is a from-scratch x86_64 operating system whose only interface is a sentence: there is no shell, no ls and not one strcmp on the input path, and the kernel answers by printing the trace lines of the calls it dispatched, in C, from the real return values. It does its own DNS and TLS in ring 0 with lwIP and mbedTLS compiled into kernel.bin, carries an API key over QEMU fw_cfg at run time so the key is never a build input, and can be asked to write a driver for a sound chip it has never heard of.
- Who is it for?
- fable-os is worth reading as a demonstration of what an operating system looks like when a language model is the only user, and worth running if you have a Mac with Homebrew or the Linux equivalents, since `make toolchain` then `make run` boots far enough to complete a real TLS handshake to api.anthropic.com and come back with an honest 401 before you have entered a key.
- Can I use it commercially?
- Not without permission. GitHub finds no licence file in the repository, and without a licence all rights are reserved by default: you may read the code but not reuse it. Check the README, or ask the authors, before using it.
- Is it still maintained?
- Yes. The repository last received commits 108 days ago.
- What is it written in?
- Mainly C, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
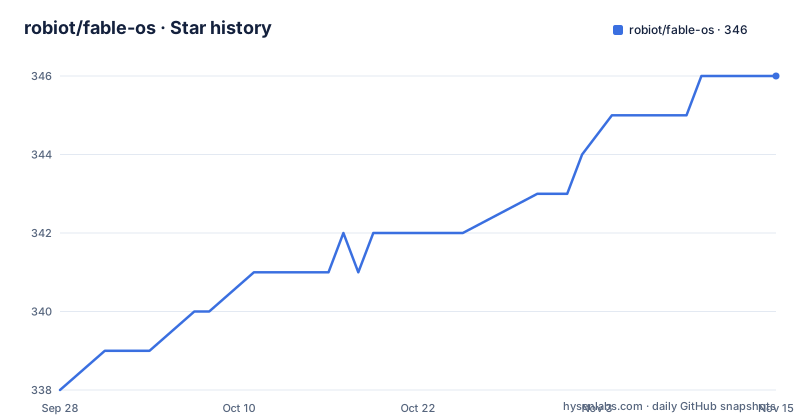
- robiot/fable-os346 ★ · +8
| Repository | 2026-09-28 | 2026-11-15 |
|---|---|---|
| robiot/fable-os | 338 | 346 |
8 Stars in the last 48 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
No shell, no ls, and not one strcmp on the input path
The central claim is stated as a prohibition rather than a feature list. There is no shell, there are no commands, there is no ls and there is no cat, and on the input path there is not one strcmp. You type what you want done and the kernel acts on the machine. What the model gets instead is 64 real syscalls into the kernel itself, covering VFS, devices, PCI, memory, screen, faults, clock, audio, network, capabilities and the compiler. What you get back is the reason to trust any of it: the kernel prints what it dispatched in C, from the real return value, so you can tell what happened from what you were told. The transcript makes the shape obvious. The model says it will open a calculator, and a bracketed line appears, gui_open app=calculator at=40,48 size=216x266 widgets=18 -> 1. It then clicks keys, and each click is a bracketed line with a widget id, a label and a coordinate, ending in a return value of 1. Only after four click lines does it say the display reads 15. The design rule behind that formatting is that prose is the model and brackets are the kernel. On a machine with no ls, that distinction is the only audit trail that exists, so the project enforces it structurally rather than promising it, and five separate defects had to be fixed to keep the rule true.
The key is not a build input, and KEY= is a hard error
The most instructive part of this repository is the comment block in the Makefile about the API key, because it documents a leak that was fixed rather than ignored. The key used to be a build input, passed as a compiler define. That put the live secret inside the compiled object, the linked kernel, the raw binary, the ISO image, and a build-flags file that recorded the flag set verbatim, which meant the key text appeared in plain sight in the last of those. All five artifacts were excluded by a gitignore, and the comment is blunt about why that is the wrong place for a safety property: one forced git add, one CI cache, or one shared build directory and the key is published. So the hazard was removed rather than guarded. There is no KEY variable and no define anywhere in the build, and grepping every build output for the key prefix finds nothing because the compiler is never told. Passing KEY on the command line is refused loudly rather than ignored, on the grounds that silently dropping a key someone believes they passed produces a kernel that gets a 401 and an operator who does not know why. There is also a make subtlety worth copying: the check tests where KEY came from rather than its value, because make imports the environment as make variables, so a naive non-empty test also fires when the variable merely happens to be exported in the caller's shell.
fw_cfg carries the key into guest RAM and nothing else holds it
Where the key goes now is described in .env.example, which is gitignored and is the only file in the tree that holds it. The Makefile reads that file inside the recipe's own shell, writes the value to a mode-0600 temporary file in the system temporary directory outside the repository, passes it to QEMU through the firmware configuration channel, and deletes the temp file however the run ends:
-fw_cfg name=opt/fableos/apikey,file=<that temp file>The guest reads the blob at boot through the fw_cfg driver into RAM, strips the trailing newline the file has, and reports only how many bytes arrived. The line you should see is `fwcfg: api key: N bytes loaded from fw_cfg`, which is a deliberately unsatisfying confirmation: a count, never the value. There is a second path for people who would rather leave nothing on disk, an exported ANTHROPIC_API_KEY environment variable, which is consulted when .env has no key. With no key at all the kernel still boots identically, still says it has none, and the API answers 401, and that is described as the default developer experience and what the tests assume. So the unauthenticated boot is not a degraded mode you discover by accident; it is the designed baseline, which is also why a fresh clone needs nothing but a toolchain before the machine says hello.
The first boot proves the HTTPS path with an honest 401
Getting to that first boot takes two commands on a Mac with Homebrew, or the Linux equivalents:
make toolchain     # once: nasm, x86_64-elf-gcc, qemu
make run
The toolchain target installs nasm, the x86_64 bare-metal GCC and QEMU, which tells you the whole build is an assembler and a cross compiler rather than anything exotic. The run target boots in QEMU with a graphics window and serial on standard output. Two variations are documented in the Makefile header: make run with ZOOM=3 gives a 3x window instead of the default 2x, and make run-nox boots headless on serial only, which is the one to use when you are reading trace lines rather than looking at them. There is a third path for real hardware shapes, make iso, which produces a GRUB bootable image for a CD or a USB stick, alongside the multiboot path that passes the kernel with -kernel. What you see on that first boot, with no key configured, is a completed TLS handshake to api.anthropic.com followed by an honest 401, and the project treats that as proof the HTTPS path works rather than as an error state. DNS and TLS are both done in ring 0 by lwIP and mbedTLS compiled into kernel.bin, with no host proxy of any kind, so the network stack is part of the system rather than a borrowed library.
The driver VM is a bounded ISA of hardware primitives
The demo that explains the architecture is asking for a driver for hardware the system has never seen. The kernel ships no audio driver and no knowledge of any sound chip, so attaching a card leaves it as an unclaimed PCI device:
make run QEMU_EXTRA="-audiodev coreaudio,id=a0 -device AC97,audiodev=a0"Ask it to find the card, write a driver and play a tone, and the described sequence is specific enough to be a checklist: read PCI configuration space, write a bring-up program in the kernel's own driver-VM instruction set, reset the codec, unmute the mixer, build a buffer descriptor list, start the DMA engine, and install itself as the system audio sink. That instruction set is the key piece of design. The driver VM is a bounded ISA whose opcodes are hardware primitives, with DMA and bus mastering available, so the model writes code in something much smaller and much more constrained than C. A bounded ISA is what makes it safe to let a model emit privileged instructions, because every opcode is one it was given. The recordings of these runs are kept in vm/transcripts/, including the WAV analysis and one run where the model diagnosed a bug in this kernel's own printf from inside the guest. That last one is the detail worth remembering: the debugging loop runs against the machine that is running the model.
Capabilities survive a reboot, and the agenda runs before the prompt
The persistence story runs through a FAT32 disk the kernel itself formatted, with ATA PIO, a block layer, and FAT32 sitting behind the VFS's vnode_ops_t. Ask for a permanent capability and the model writes a program, saves it as a named capability on that disk and verifies it. Then power the machine off and on, and the second boot assembles nothing while reporting that one capability was loaded from /disk/cap. The interesting transcript is the one that checks the arithmetic afterwards, where the call itself is a bracketed kernel line with a version and a recursion depth, cap.call is_perfect_square v1 depth=0 -> 1, and only then does the model answer, yes, with the numbers. Alongside capabilities sits an agenda, a scheduled list loaded from /disk/agenda.json, and the demo of it is deliberately unsettling: with no API key at all and nobody typing, a boot item runs before the prompt is even printed, and the machine reports one boot item ran before anyone typed anything. If you are evaluating whether this is a toy or a research system, that transcript is the most informative artifact in the repository, and it is a plain text file in a directory.
The C compiler and the window manager both run on the machine
Two subsystems make the demos possible without a host toolchain. The first is the C compiler, which is described as lexer, preprocessor, parser, type checker and x86-64 code generation, all on the machine, so a driver or a capability can be compiled inside the guest rather than uploaded. The second is the display and window stack: a 1024x768 framebuffer with a real font, UTF-8, a window manager and a PS/2 mouse, with concurrency handled by cooperative fibers over guarded stacks so the screen keeps servicing input while a turn is in flight. Apps are not drawn, they are authored, as a document describing widgets and handlers that the runtime launches into a real window you can click. Two build flags let you see parts of that without spending a turn of API budget: make run with EXTRA_CFLAGS set to the app self-test define opens the reference calculator directly, and the concurrency define opens a clock window instead, where asking anything leaves the seconds ticking during the turn, with one 1725 ms API call servicing the screen 283 times. That number is the cheapest available evidence that the scheduler is not blocked on the network, and it is stated as a specific observation rather than a benchmark.
Host-native tests keep the inner loop out of QEMU
Testing is split along the line of what actually needs a virtual machine. `make test-host` runs 39 suites natively, compiled against the host compiler, in milliseconds, because pure-logic kernel modules do not require a boot to be exercised. `make test-host-asan` runs the same suites under AddressSanitizer and UndefinedBehaviorSanitizer. `make test-qemu` covers 6 boot cases plus a formatter lint, and hardware behaviour is asserted from real serial logs by a declarative case runner, which is how the trace-line discipline gets enforced by tooling rather than by review. The repository layout explains where the effort went: boot and arch for multiboot, long mode, the IDT and fault handling; core for kernel objects, the tool registry, capabilities, fibers and the agenda; mm and fs for the heap, VFS, ramfs and FAT32; drivers for serial, PCI, e1000, PS/2, RTC, ACPI, ATA and fw_cfg; net for JSON, the transport seam, the turn loop, TLS, SSE and fetch; vm and compiler for the driver VM and the C compiler; gui and apps for the window manager, widgets and app runtime; and tools for the model's syscalls, one file per family. The scale is about 72k lines of C and assembly plus 53k lines of tests, with lwip and mbedtls vendored at 330k lines that are not counted as achievement. The last push to main landed on 2026-07-30 and there are no GitHub releases.
Editorial conclusion
fable-os is worth reading as a demonstration of what an operating system looks like when a language model is the only user, and worth running if you have a Mac with Homebrew or the Linux equivalents, since `make toolchain` then `make run` boots far enough to complete a real TLS handshake to api.anthropic.com and come back with an honest 401 before you have entered a key. It is not a daily driver, not a shell to replace one, and not something to put in front of users, because there is no shell at all by design and the README says none was written. Three things to verify yourself rather than assume. First, the key story, which is the strongest engineering claim in the repository: there is no -D and no generated header, `make KEY=...` is a hard error rather than a silent no-op, and the value travels over fw_cfg into guest RAM, with the kernel reporting a byte count and never the key, but note the Makefile's own point that it tests `$(origin KEY)` rather than `$(KEY)` precisely because make imports the environment as make variables. Second, the trace lines, which are the only audit trail on a machine with no ls; vm/transcripts/ holds real recordings, including one run where the model found a bug in the kernel's own printf from inside the guest. Third, the code volume, about 72k lines of C and assembly plus 53k lines of tests against 330k vendored lines of lwIP and mbedTLS, which tells you the network stack is not the achievement. The licence is not stated in the repository metadata, there are no GitHub releases, and the last push to main landed on 2026-07-30.
Frequently asked questions
How do I build and boot fable-os?
On a Mac with Homebrew or the Linux equivalents, run `make toolchain` once to install nasm, x86_64-elf-gcc and qemu, then `make run` to boot in QEMU with a graphics window and serial on stdio. `make run ZOOM=3` gives a 3x window instead of the default 2x, `make run-nox` boots headless on serial only, and `make iso` produces a GRUB bootable image for a CD or USB stick. No API key is needed for the first boot.
How does fable-os handle the Anthropic API key?
The key is never a build input. There is no -D define and no generated header, `make KEY=...` is refused loudly, and the value travels from host to guest at run time over QEMU's fw_cfg channel into RAM only. The kernel prints the byte count and never the key. You can put it in a gitignored .env, or export ANTHROPIC_API_KEY and leave nothing on disk; with no key at all the kernel boots the same way and the API answers 401.
What can the fable-os model actually do besides talk?
It gets 64 syscalls covering VFS, devices, PCI, memory, screen, faults, clock, audio, network, capabilities and the compiler. Concretely it can open a calculator window and click its own keys with the mouse, write a driver for an unclaimed PCI sound card using the bounded driver-VM instruction set, compile C on the machine, and save a program as a capability on a FAT32 disk that survives a reboot and can be scheduled to run before the prompt is printed.
How do I tell what fable-os really did from what it claims?
The kernel prints bracketed trace lines in C from the real return value of each dispatch, and the convention is that prose is the model while brackets are the kernel, a distinction the project says it enforces structurally after five defects had to be fixed. The repository keeps real recordings under vm/transcripts/, including a WAV analysis and a run where the model diagnosed a bug in the kernel's own printf from inside the guest.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/robiot-fable-os)Star history chart for your README
[](https://hysenlabs.com/projects/robiot-fable-os)Was this useful?