RSS to Telegram Bot: the project description is a call for maintainers
A Telegram RSS bot that cares about your reading experience (calling for new maintainers: https://github.com/Rongronggg9/RSS-to-Telegram-Bot/issues/747)
At a glance
- What is it?
- A multi-user Telegram bot that forwards RSS feed posts with media, emoji and formatting intact, distributed as a Docker image, two PyPI packages and source. The newest release is from eighteen months ago, the repository's own summary asks for maintainers, and the default branch is not the branch the released package tracks.
- Who is it for?
- RSS to Telegram Bot is worth using if you want feed posts delivered to Telegram with the formatting and media you would otherwise have to re-do by hand, and if you can host it yourself rather than relying on the public instance. Three things decide whether it fits.
- Can I use it commercially?
- Yes, with strict conditions. AGPL-3.0 is a network copyleft licence: if people use a modified version over a network, for example as a hosted service, you must offer them its source code under the same licence.
- Is it still maintained?
- Yes. The repository last received commits 1 day ago.
- What is it written in?
- Mainly Python, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 21, 2026, and from our analysis. They are not legal advice.
Star history
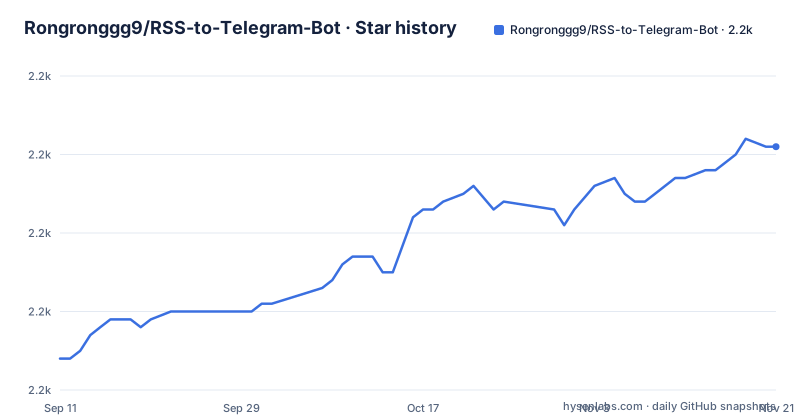
- Rongronggg9/RSS-to-Telegram-Bot2,181 ★ · +27
| Repository | 2026-09-11 | 2026-11-21 |
|---|---|---|
| Rongronggg9/RSS-to-Telegram-Bot | 2.2k | 2.2k |
27 Stars in the last 71 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The project summary is a request for a maintainer, and the last release is old
The most useful sentence about this project is in its metadata rather than its documentation. The summary line describes a Telegram bot that cares about your reading experience and then, in parentheses, links to an issue calling for new maintainers. That is the project's own statement of its position, and the release history is consistent with it. The three most recent tags are 2.10.0, whose note mentions a container health check and chat-specific hashtags, then 2.9.0 from the year before, whose note mentions a Telegraph-related revert and skipping certificate verification, then 2.8.0. The last recorded push to the development branch is far more recent than any of those tags. So the pattern is a maintained working tree with a stalled release line: commits continue, and no new version has been cut to match them.
The default branch is not the branch the released package tracks
The repository's default branch is the development branch, and the deployment section explains what each distribution channel follows. The package on the stable Python index tracks the master branch. The package on the test index tracks the development branch and is described as always up to date. The container badge in the header links two build queries, one scoped to master and one scoped to development. That means the artefact most people install from the stable index is built from a branch that is not the one the project develops on, while the artefact that reflects current work is on the test index where almost nobody looks. It is a reasonable arrangement for a project with limited time, and it is a trap for anyone who assumes the default branch is what pip gives them.
The licence section contains an operational instruction, not just a licence
The licensing block does more than name a licence. It states the project is AGPLv3+, and it adds that closed-source distribution and bot-hosting are strictly prohibited. Then it gives instructions rather than principles: if you distribute or host the bot with code modifications, make sure the source code is available to anyone who can use the bot, and the suggested mechanism is to edit the repository URL inside the internationalisation module. That string is the URL the running bot shows its users, which makes compliance partly a matter of configuration rather than purely of intent. The instruction is unusually concrete and the surrounding licence text is the standard copyleft notice, so a reader gets a clear rule and a one-line way to comply with it.
Two projects share this name and share no code
The closing line of the documentation is a piece of history worth stating plainly. The repository was forked from another project of the same name in 2020, and since sometime in 2021 the two have shared no common codebase and are described as completely different projects. That sentence exists because the names are identical and the search results are not, which is a genuine trap for anyone arriving from a search rather than from the repository. It also means the issue tracker, the documentation and the release history of the other project say nothing about this one. For a project that is publicly asking for maintainers, being indistinguishable from its own abandoned fork in search results is a real cost.
setup.py renames the source directory and turns migration folders into packages
The packaging file does three unusual things, each with a comment explaining why. The version is not a literal: it is read out of a version module in the source tree with a regular expression, so the number lives in one place. The package list is not used as found: a compiled substitution rewrites the leading source directory name to the distribution name, because the code lives in a directory called src and ships as a package called rsstt, with a package directory mapping to match. And the migration folders under the database directory are globbed, converted into dotted names and appended to the package list, with the comment explaining that migrations are not Python packages but still have to be included. The packaging metadata table itself is nearly empty, holding only the build system, so the real metadata is in the setup script.
The requirements file carries its own archaeology, including a commented-out git install
The dependency list records why several pins exist, in comments that would be deleted in most projects. One line pins the feed parser and carries, as a comment, the git URL of a fork on a development branch, which reads as a maintainer tracking an upstream fix they cannot use yet. Another caps a SQLite driver below a version with the reason written out, naming the exact release of the ORM it is incompatible with. A third caps a CLI library below a version only for interpreters older than 3.11, with the comment explaining that the newer release misses a dependency on 3.10. Two more use environment markers: an event loop library that skips Windows, Cygwin and one unusual platform, and an accelerator library limited to specific processor architectures. Every dependency is pinned exactly, and the only floating one is the SQLite cap.
The container build treats a comment convention as a feature flag
The image build has a two-stage dependency phase and a mechanism for experimental packages that is worth reading closely. A build argument holds a regular expression whose job is to find requirement lines whose comment contains a package name followed by an at-sign and a URL, which is exactly the shape of a git-installed dependency. A sed pass over the requirements file extracts those matches and builds wheels for only those, so a commented-out git URL is not documentation, it is a build input. A second build argument switches whether those experimental packages get installed into the image at all, and when it does, the affected packages are detected by the same pattern, uninstalled and reinstalled from the wheels. So a contributor adding a fork-based dependency gets it excluded from the image by default and included by one flag.
Three files disagree about the copyright year
Small things, but they are checkable. The licence notice in the documentation carries a copyright range ending two years earlier than the one in the container build, and the build script's own header carries a single later year and no range at all. So the three files that open with the same licence header name three different spans. None of this has a functional consequence, and all three are the kind of detail that tells you how rarely the headers are edited together. The rest of the build is careful by comparison: a dedicated base stage creates a virtual environment at a fixed path, puts it first on the path, upgrades packaging tools without caching, installs the requirements, and then deletes the source tree the install left behind.
Editorial conclusion
RSS to Telegram Bot is worth using if you want feed posts delivered to Telegram with the formatting and media you would otherwise have to re-do by hand, and if you can host it yourself rather than relying on the public instance. Three things decide whether it fits. Understand the maintenance position before you depend on it, because the project's own summary is a request for maintainers, the newest tagged release predates the most recent commits by well over a year, and the public bot is offered with no warranty and a request to keep subscriptions modest. Read the licence section carefully if you plan to host it for anyone else, because it is AGPL and the page adds an explicit prohibition on closed-source distribution and bot-hosting, with an instruction to publish your source by editing a repository URL inside the internationalisation module. And pick your install source deliberately, since the package on the stable index tracks a branch that is not the default one while the always-current package lives on the test index.
Frequently asked questions
How do I run RSS to Telegram Bot?
The recommended route is Docker Compose, described as suitable for virtually all virtual private servers. A platform as a service is officially supported. You can also install from PyPI, which tracks the master branch, or from TestPyPI, which tracks the dev branch and is always up to date, or run directly from source if you are developing.
Can I host RSS to Telegram Bot and keep the source closed?
No. The project is licensed under AGPLv3+ and the licensing section states that closed-source distribution and bot-hosting are strictly prohibited. If you host it with modifications, the source must be available to anyone who can use the bot, and the page says to make it available by editing the repository URL inside the internationalisation module.
Which languages does RSS to Telegram Bot support?
English, Chinese, Cantonese, Italian and more. Translations are managed through a hosted translation service, a translation guide is published, and a Chinese readme is linked from the top of the page alongside the changelog, FAQ and documentation links.
Why does RSStT send some images as files instead of inline?
Because Telegram compresses long images and makes them unreadable, so long images are sent as file attachments instead. Media handling otherwise covers images, video and audio in both post content and enclosures, documents in enclosures, conversion of emoji shortcodes and emoji images into real emoji or their description, and automatic splitting of messages that are too long.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/rongronggg9-rss-to-telegram-bot)Star history chart for your README
[](https://hysenlabs.com/projects/rongronggg9-rss-to-telegram-bot)Was this useful?