One dependency claimed, five services defined: reading rudder-server's own files
Privacy and Security focused Segment-alternative, in Golang and React
At a glance
- What is it?
- The compose file, Dockerfile, Makefile and go.mod of rudderlabs/rudder-server, checked against the claims in its own README: default credentials, a token written into the shipped binary, a test target that absorbs failures, and nine dependency pins.
- Who is it for?
- Read rudder-server as infrastructure that assumes a trusted network and an operator who reads its files before running them. Settle the license question first, since the README names the Elastic License 2.0 while the repository metadata reports the licence as NOASSERTION.
- Can I use it commercially?
- Check first. The repository uses a licence we do not classify automatically, so read its LICENSE file before any commercial use.
- Is it still maintained?
- Yes. The repository last received commits 1 day ago.
- What is it written in?
- Mainly Go, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 14, 2026, and from our analysis. They are not legal advice.
Star history
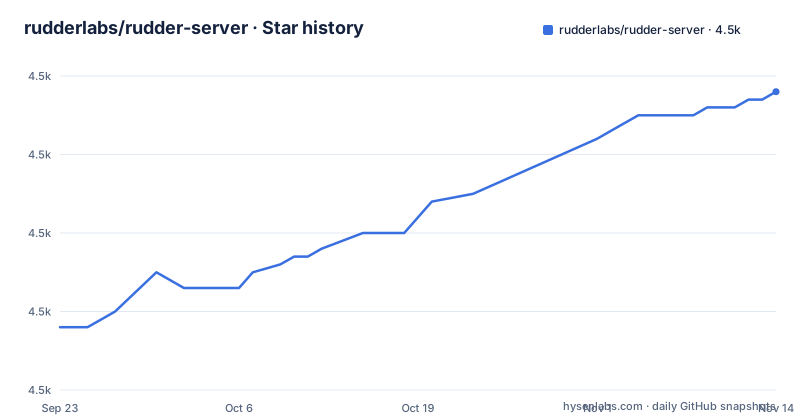
- rudderlabs/rudder-server4,518 ★ · +30
| Repository | 2026-09-23 | 2026-11-14 |
|---|---|---|
| rudderlabs/rudder-server | 4.5k | 4.5k |
30 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The architecture paragraph names one dependency and the compose file starts four services
The architecture section calls rudder-server an independent, stand-alone system whose only dependency is the database, and names PostgreSQL as that database. The compose file at the repository root tells a wider story. It defines five services: a `db` service on `postgres:15-alpine`, a `backend` built from the local Dockerfile, a `transformer` running `rudderstack/rudder-transformer:latest`, and two more parked behind profiles, `minio` under `storage` and `etcd` under `multi-tenant`. The module agrees with the wider list. Its require block names Google Cloud BigQuery, Pub/Sub and Storage, Azure blob storage, ClickHouse, the Apache Pulsar client, and AWS services including Kinesis, Firehose, Glue, Lambda, Personalize Events, EventBridge and S3.
That gap matters when you size a deployment. Only PostgreSQL describes the default single node path, and etcd sits behind a profile, so a reader who never turns on multi tenant mode never meets the second stateful service. The transformation step is different. The `backend` service declares `depends_on` for both `db` and `transformer`, which puts the transformer container on the default startup path even though the architecture paragraph does not count it as a dependency.
Default credentials sit in the compose file, and etcd listens on all interfaces
The two profile gated services arrive with credentials written into the file itself. The minio service sets `MINIO_ROOT_USER=root` and `MINIO_ROOT_PASSWORD=password`. The etcd service sets `ALLOW_NONE_AUTHENTICATION=yes` and binds `ETCD_LISTEN_CLIENT_URLS=http://0.0.0.0:2379`, while advertising itself to peers at `http://mode-provider:2379`, a host name that appears nowhere else in the file.
Both publish ports to the host, 9000 and 9001 for minio and 2379 for etcd, alongside 6432 for Postgres and 8080 for the backend, and neither declares a volume, so both stores start empty on every run. Here is that block as it stands:
  minio:
    image: pgsty/minio
    profiles:
      - storage
    ports:
      - "9000:9000"
      - "9001:9001"
    environment:
      - MINIO_ROOT_USER=root
      - MINIO_ROOT_PASSWORD=password
    command: server --console-address :9001 /data
  etcd:
    image: docker.io/bitnami/etcd:3
    profiles:
      - multi-tenant
    environment:
      - ALLOW_NONE_AUTHENTICATION=yes
      - ETCD_NAME=etcd
      - ETCD_LISTEN_CLIENT_URLS=http://0.0.0.0:2379
      - ETCD_ADVERTISE_CLIENT_URLS=http://mode-provider:2379
    ports:
      - "2379:2379"
The backend entrypoint is written as `sh -c '/wait-for db:5432 -- ./rudder-server'`, and it calls `/wait-for` while the Dockerfile copies in two separate wait helpers, `build/wait-for` at the image root and a `wait-for-go` binary from `build/wait-for-go/`. The file also opens with `version: "3.7"`, a key current Compose releases warn about rather than read.
The build writes an enterprise token into the shipped binary
The image is assembled in two stages: a builder on `golang:1.27.3-alpine3.24` pinned by digest, and an `alpine:3.24` runtime that adds `tzdata`, `ca-certificates`, `postgresql-client`, `curl` and `bash`. Version metadata is injected at link time through `-X` flags, and the last of them is not a build identifier:
RUN BUILD_DATE=$(date "+%F,%T") \
    LDFLAGS="-s -w -X main.version=${VERSION} -X main.commit=${COMMIT_HASH} -X main.buildDate=$BUILD_DATE -X main.builtBy=${REVISION} -X main.enterpriseToken=${ENTERPRISE_TOKEN} " \
    make build
`ENTERPRISE_TOKEN` arrives as a build argument, so its value is baked into the artifact rather than read at run time from the environment. `-X` writes a string into the binary's data section, which means whatever was passed stays readable inside anything you ship from that build. Whether that matters is a pipeline decision rather than a code decision, and a team that builds once and publishes images is making that call on behalf of every downstream consumer.
Two smaller details sit next to it. The builder declares `ARG PKG_NAME=github.com/rudderlabs/release-demo`, a default package path pointing at a different repository than the one being compiled. And the tree root carries an `enterprise/` directory alongside `controlplane/` and `regulation-worker/`.
Every test run in the Makefile ends with a swallowed failure
`make test` expands to `install-tools test-run test-teardown`, and the invocations inside `test-run` terminate the same way:
$(TEST_CMD) -count=1 $(TEST_OPTIONS) $(FILES) && touch $(TESTFILE) || trueThe trailing `|| true` absorbs a failure of the whole chain, so a red suite does not hand a non-zero exit back to make. `TESTFILE=_testok` is created as a marker rather than as a result, and the same shape appears in the package and exclude branches a few lines below.
The flags around it are strict in the other direction. `-p=1` runs one package at a time, `-shuffle=on` randomises order, `-failfast` stops at the first failure, `--timeout=15m` caps the run, `SLOW=0` is exported ahead of the command, and `-coverpkg=./...` attributes coverage across every package whether or not it is under test. The wrapper is `gotestsum --format pkgname-and-test-fails` unless debug mode is on, in which case plain `go test` takes over. Tool versions are pinned the same way: golangci-lint v2.14.0, gofumpt v0.9.1, mockgen v0.6.0, protoc-gen-go v1.33.0 and gitleaks v8.21.2, while actionlint and govulncheck track @latest. A pipeline that runs `make test` should read that `|| true` before it reads anything else.
Nine replace directives hold the dependency graph in place
The comment above the replace block says it exists to address snyk vulnerabilities in indirect dependencies, and it asks that an upgraded dependency use the same version in both places. Two of the nine entries deserve a closer read:
replace (
	github.com/cyphar/filepath-securejoin => github.com/cyphar/filepath-securejoin v0.2.5
	github.com/gin-gonic/gin => github.com/gin-gonic/gin v1.10.0
	github.com/go-jose/go-jose/v3 => github.com/go-jose/go-jose/v3 v3.0.3
	github.com/satori/go.uuid => github.com/satori/go.uuid v1.2.0
	github.com/xitongsys/parquet-go => github.com/rudderlabs/parquet-go v0.0.3
	golang.org/x/image => golang.org/x/image v0.24.0
	golang.org/x/net/html => golang.org/x/net/html v0.41.0
	gopkg.in/yaml.v3 => gopkg.in/yaml.v3 v3.0.1
	k8s.io/kubernetes => k8s.io/kubernetes v1.32.1
)
`parquet-go` is redirected to a fork under the same organisation, `github.com/rudderlabs/parquet-go v0.0.3`, so warehouse Parquet handling runs on code maintained in this ecosystem rather than on the upstream module. `satori/go.uuid` is held at v1.2.0, and `k8s.io/kubernetes` at v1.32.1, which brings a full Kubernetes release line in as a library dependency. The module declares `go 1.27.3`, and the Dockerfile pins `GO_VERSION=1.27.3` to match, with Go and Alpine both fixed by digest so a rebuild of the same tag gets the same toolchain.
The production note points at Helm charts and says images move faster than the source
Setup is offered as three documentation links rather than commands in this file: Docker, Kubernetes, and a developer machine setup. Beneath them sits a note in capitals advising the Kubernetes Helm charts for production, on the stated grounds that Docker images are updated with bug fixes much more frequently than the GitHub repository. One reading is reassurance about image freshness. The other is a plain statement that the source tree is not the fastest route to a patched build, which matters to anyone whose plan was to pin a commit and compile it.
The release list points the other way. v1.92.0-rc.1 was published on 2026-10-26, v1.92.0 at 08:11 on 2026-10-27, and v1.92.1 at 10:59 on 2026-10-28, so a candidate, a final and a patch all landed inside about two days. The repository also carries its own review configuration at the root in `AGENTS.md`, `.junie/`, `.deepsource.toml` and `.golangci.yml`, which tells you where the project's standards are written down but says nothing about how wide the gap between an image and its tag can get.
The 99.99 percent uptime figure has no measurement behind it in this tree
The feature list claims at least 99.99% uptime, credits a retry and error handling system with delivering data through network partitions and destination downtime, and says more than 90 tool and warehouse destinations are supported. It also names Mattermost, IFTTT, Torpedo, Grofers, 1mg, Nana and OnceHub as production users. None of that can be checked from the repository. There is no benchmark directory, no load test artefact and no runbook in the tree, and the only checks visible are workflow badges linked from the README header plus a `codecov.yml` file at the root.
The shape of the claim is the interesting part. An availability figure like that has to be enforced outside the binary, in deployment and monitoring, and the architecture paragraph's single PostgreSQL is the only hard dependency the README identifies, so every retry across a database blip carries more weight than one sentence gives it. The destination count is at least partly checkable: the module's BigQuery, ClickHouse, Kinesis, Firehose, Pub/Sub and Azure blob entries are the client libraries a large share of those destinations would need. The rest of it is a promise made in a bullet point.
The license line names the Elastic License 2.0 and no license value is recorded
Licensing is one sentence: the server is released under the Elastic License 2.0, with a link to the LICENSE file, and the tree root does hold a LICENSE file. The repository metadata reports the licence as NOASSERTION, meaning GitHub did not match the file to a standard identifier, so read the LICENSE file itself before adopting this as shared infrastructure.
The same tension runs through the opening copy, which calls rudder-server the leading open source customer data platform and refers to RudderStack Open Source in the pricing bullet, while the recommended route for production is a vendor maintained Helm chart, and the same README says its Docker images are patched more often than the repository. An open source framing, a named license with no OSI claim attached to it, and a hosted path you do not build yourself: that combination is worth holding in view together. A reader who skims only the badges at the top of the README will come away with the wrong idea about what they can do with the result.
Editorial conclusion
Read rudder-server as infrastructure that assumes a trusted network and an operator who reads its files before running them. Settle the license question first, since the README names the Elastic License 2.0 while the repository metadata reports the licence as NOASSERTION. Then replace the compose defaults for the object store and etcd, and decide whether a link time token inside images built with ENTERPRISE_TOKEN is acceptable in your build pipeline. Teams looking for a benchmark behind the 99.99% uptime figure will not find one here.
Frequently asked questions
How much does RudderStack cost?
The README points readers at a free tier of the hosted RudderStack Cloud product and lists no prices anywhere, and this repository carries no pricing table either, so the cost of the hosted tier has to come from the vendor rather than from the code.
What is the meaning of "rudder"?
Nothing in this repository defines the word. It appears only inside the project and vendor names, and there is no glossary or terminology section anywhere in the tree, so the question has to be answered from the vendor's own material.
Who owns RudderStack?
The module path is `github.com/rudderlabs/rudder-server`, the tree root holds `enterprise/`, `controlplane/` and `regulation-worker/` directories next to a LICENSE file, and the README links the vendor site, a Slack community and a Twitter account under the same name.
What is rudder analytics used for?
The repository never mentions rudder analytics. What it describes is a customer data platform backend written in Go with a React interface, whose only stated hard dependency is PostgreSQL, plus SDK, transformer and warehouse integrations.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/rudderlabs-rudder-server)Star history chart for your README
[](https://hysenlabs.com/projects/rudderlabs-rudder-server)Was this useful?