eSIM Tools automates a carrier login, and its manifest points at a file it does not ship
Giffgaff Simyo eSIM SIM eSIM (A modern set of eSIM management tools designed specifically for users who already have Giffgaff and Simyo numbers, offering support for converting physical SIM cards to eSIMs, device replacements, and QR code generation.).
At a glance
- What is it?
- Silentely/eSIM-Tools turns a physical SIM into an eSIM or moves an eSIM to a new phone for people who already hold a Giffgaff or Simyo number. It runs in the browser, it depends on an account login and a one-time code, and its package manifest names an entry point the repository does not contain.
- Who is it for?
- This suits an existing customer of one of the two supported carriers who wants to change hardware without a support call, and who is comfortable entering carrier credentials into a third-party page. Two things to weigh first.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 7 days ago.
- What is it written in?
- Mainly JavaScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 14, 2026, and from our analysis. They are not legal advice.
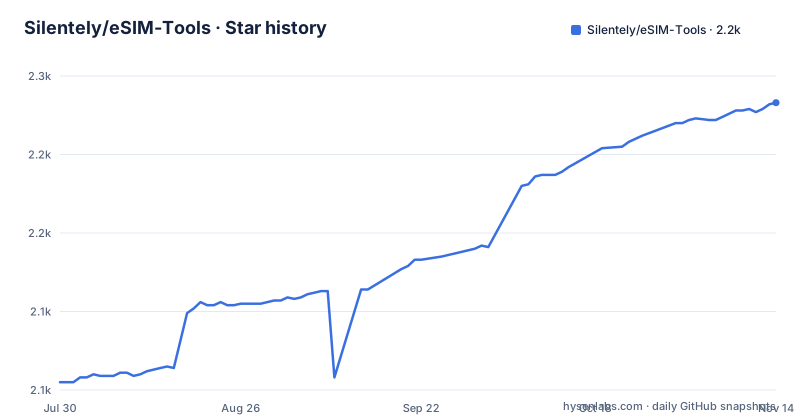
Star history
- Silentely/eSIM-Tools2,233 ★ · +178
| Repository | 2026-07-30 | 2026-11-14 |
|---|---|---|
| Silentely/eSIM-Tools | 2.1k | 2.2k |
178 Stars in the last 107 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Two carriers, and one hard precondition on both
The tool supports exactly two carriers, one in the United Kingdom and one in the Netherlands, and the scope note is unambiguous: it is for people who already hold a number with one of them. Everything it does depends on that. Converting a physical SIM to an eSIM, moving an eSIM to a replacement device and generating the activation code all act on an existing line. New applicants are explicitly out of scope, and the page says so twice, once in the scope note and again in the audience section where each carrier gets a checklist with the last item marked as not supported. For the Dutch carrier the page also constrains the number format, requiring ten digits beginning with the national prefix, so a reader outside those two markets can rule themselves out from the first line.
The flow is an account login plus a one-time code
For the British carrier the documented path has four steps: sign in using a secure method, confirm by email or message, enter a six-digit code from a text message, and receive an activation code that is generated automatically. The page recommends this method over the alternatives and says it is fully automatic apart from the code. For the Dutch carrier the shape is the same with a different second step, where you choose between replacing a device and retrieving an existing profile before confirming. One line deserves attention: for a customer who does not yet have a number, the page points British users at a third-party modified application or module to obtain a code, and Dutch users at the carrier's own application. That recommendation sits outside the tool's own scope and outside anything the two carriers document.
One carrier switched off the manual route in October 2025
The frequently-asked-answers section records that the manual activation method was disabled by the carrier on 8 October 2025 and that the message-code method is now the only route, which tells you how tightly this tool is coupled to one carrier's current behaviour. Two operational constraints are documented alongside it. Activation only works inside a service window given in the carrier's local time, and the page displays your local time next to that window so you can see whether attempting it is worthwhile. And if you close the page mid-flow, signing back in resumes from a recoverable point rather than starting over, with an explicit recommendation not to close the tab until activation completes. Both are the kind of detail that only appears once something has broken for someone.
A no-framework claim next to dependencies that point outward
The technical section describes the project as plain JavaScript with no framework dependency, a small bundle, offline capability and a first-screen load under about a second. The manifest tells a longer story. It declares an HTTP client, an HTML parser, a cross-origin middleware package, an environment loader, a key-value store from the hosting platform, and an error-reporting client in two forms, one for the browser and one for the server. Against that, the privacy section claims all processing happens locally, that credentials are not stored, that the code is open and auditable, and that it should be used on a secure network, and the repository carries a separate security document. Both sets of statements can be true, since an error-reporting client only reports if it is configured, but they are worth reading together rather than separately.
The manifest's entry point is not in the repository
The package manifest names an index file as the entry point, and the repository root does not contain that file. What it contains instead is an HTML file, a server file, a source directory and a scripts directory, and the manifest's own start and development commands run the server file. That mismatch is harmless for a page deployed as static files and wrong for anyone who installs the package expecting an importable module. The rest of the script list is also worth scanning, because it is a hand-written pipeline rather than a framework: two hook installers, three separate checks that run local node files, a commit-message linter, three build steps that run before other commands, a test runner in three modes, a static-site build, a deployment command that shells out to the hosting platform's CLI, an image optimiser, a compressor, a security check, a quality check, an asset link checker, and three more scripts whose names suggest preparing, analysing and testing a deployment.
Two install paths, and a container-free deployment on one platform
For most readers the tool is a hosted page and the installation section is folded away under a developer heading. For developers it is five commands:
git clone https://github.com/Silentely/eSIM-Tools.git
cd eSIM-Tools
npm install
cp env.example .env
npm run dev
Then open the local port it prints. The stated requirements are a current Node runtime and package manager, plus four named browser baselines. The alternative path is to fork the repository and connect it to a static hosting platform, with a build command and a publish directory both named in the page and environment variables taken from the same example file. There is no container configuration anywhere in the repository, which is consistent with the static build and the local-server development model but means there is no documented way to run the tool as a service you control.
Code under one licence, documentation under another that forbids commerce
The licensing section draws a line most projects do not. Code is released under a permissive licence except where stated otherwise, while the readme, the wiki and similar resources are under a share-alike licence with an explicit non-commercial condition, and the page explains what that means in unusually plain language: you may copy and redistribute with attribution and you may not use it commercially, with any profit-making activity counted as commercial. That is a split worth knowing before you fork it, because a fork that keeps the documentation is a fork that cannot be sold. The page also carries a disclaimer that the tool is for study and personal use, that users should respect the relevant terms of service, and that the developers accept no responsibility for problems arising from its use.
Editorial conclusion
This suits an existing customer of one of the two supported carriers who wants to change hardware without a support call, and who is comfortable entering carrier credentials into a third-party page. Two things to weigh first. The page claims all processing happens locally and that credentials are not stored, while the manifest declares an error-reporting client for both browser and server and a hosted key-value store among its dependencies, so read the security document before you paste a login into it. And the service depends on flows the carriers do not document, one of which was switched off by the carrier in October 2025, so treat it as fragile rather than as a stable interface.
Frequently asked questions
What is Silentely/eSIM-Tools?
It is a free browser-based tool for people who already hold a number with one of two supported carriers, one in the United Kingdom and one in the Netherlands. It converts a physical SIM card into an eSIM without replacing the card, moves an eSIM to a replacement device, and generates an activation code to scan, and it describes itself as taking one to two minutes with no support contact needed.
Who can use eSIM-Tools?
Only existing customers of the two supported carriers, and the page states this restriction twice: once in the scope note and again in the per-carrier audience checklists, where applying for a new number is marked as not supported. For the Dutch carrier it additionally requires a ten-digit national number, so readers outside those two markets can rule themselves out immediately.
What happens if I do not have a number yet?
The tool does not cover it. The page says so explicitly and then points British users at a third-party modified application or module for obtaining an activation code, and Dutch users at the carrier's own application. Neither route is part of the tool, and the modified-application suggestion is outside anything the carriers document.
Is my data safe with eSIM-Tools?
The page claims all processing happens locally, that user credentials are not stored, that the code is open and auditable, and that it should be used on a secure network, and the repository carries a separate security document. Against that, the manifest declares an error-reporting client for both browser and server and a hosted key-value store among its dependencies, so both sets of statements are worth reading together.
How do I run eSIM-Tools locally?
Clone the repository, install dependencies, copy the example environment file to a local one and fill it in, start the development server, and open the local port it prints. The stated requirements are a current Node runtime and package manager plus four named browser baselines. The alternative is to fork and connect to a static hosting platform with a named build command and publish directory; no container configuration exists in the repository.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/silentely-esim-tools)Star history chart for your README
[](https://hysenlabs.com/projects/silentely-esim-tools)Was this useful?