Alexandrie: five default secrets, two floating image tags, and a Makefile with a phantom target
📚 The open-source, offline-first Notion, Obsidian & Confluence alternative. Advanced Markdown, multi-tenant teams, OIDC/SSO, and local S3 backups. Deploy in one command.
At a glance
- What is it?
- A self-hosted Markdown knowledge base whose one command install copies an example environment file that supplies a working password for every service, while its Makefile declares a target it never defines and its object storage target predates the service the compose file actually runs.
- Who is it for?
- Alexandrie suits a team that wants a self-hosted Markdown wiki with per-node permissions, an offline-capable web app, and its own object storage rather than a vendor account, and the three-service stack comes up in three commands. Verify five things before you expose it.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 4 days ago.
- What is it written in?
- Mainly Vue, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
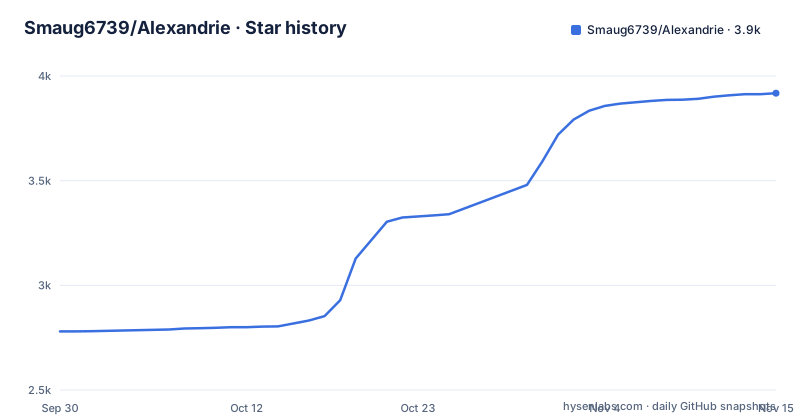
- Smaug6739/Alexandrie3,918 ★ · +1,138
| Repository | 2026-09-30 | 2026-11-15 |
|---|---|---|
| Smaug6739/Alexandrie | 2.8k | 3.9k |
1,138 Stars in the last 46 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Every credential in the compose file has a default that ships in the repository
The quick start is three commands, and the middle one is what decides how the stack is secured.
# 1. Download the .env.example and docker-compose.yml files
curl -O https://raw.githubusercontent.com/Smaug6739/Alexandrie/main/.env.example
curl -O https://raw.githubusercontent.com/Smaug6739/Alexandrie/main/docker-compose.yml

# 2. Configure environments
cp .env.example .env

# 3. Launch the stack
docker compose up -d
The compose file resolves each secret from the environment with a fallback, and every fallback is a working value: the database root password defaults to rootpassword, the application database password defaults to password, the object store access key defaults to alexandrie-key and its secret key to alexandrie-secret, and the backend's signing secret defaults to a placeholder string whose own text says to change it. So the documented path to a running instance is also the path to an instance using credentials that are published in the repository, and the only step between them is copying a file rather than editing it. The example environment file does carry an instruction not to commit the final environment file to source control, which is the one place in the project where those default values are acknowledged as something to be replaced rather than used.
Two of the three images float on a latest tag
The stack runs three images and pins one of them. The database is pinned to a major version tag, 8.0, which at least holds the major line still. The object store is referenced by a bare latest tag, and so is the backend, which is pulled from a registry path under the maintainer's own account rather than built locally. Two floating tags in a compose file means a restart months later can pick up a different backend build or a different storage engine than the one the documentation was written against, with nothing in the compose file recording which version that was. This sits directly against the feature bullet that calls the platform production ready, which also names single sign-on providers, automated backup and restore pipelines, and a storage architecture it describes in strong terms. None of that is inconsistent on its own, but the version story a deployment inherits is the loosest part of the package. That tag also moves often, since the release history holds three tags inside two weeks, a minor and two patches, with the most recent push landing a couple of weeks after the last of them.
The database and the object store are both published on the host
Two of the three services map a host port. The database maps a configurable external port, defaulting to 3307, onto its own 3306, and the object store maps a configurable port, defaulting to 9000, onto its own 9000. Neither mapping is restricted to the loopback interface, so on a host with a routable address both are reachable from outside unless a firewall stops them, and both are reachable with the default credentials described earlier. The object store additionally carries a flag for whether its own console is enabled, defaulting to false, and a log level variable defaulting to info. The two services also treat readiness differently, which is worth knowing if you write health-dependent automation. The database probe runs an actual query, a select of one, against the configured user and database, while the object store probe only checks that something is listening on its port with a netcat call and an exit code. The database probe takes care to escape its own variable references with a doubled dollar sign, which keeps the compose substitution step from replacing references meant for inside the container, and both services persist through named volumes, one for the database and two for the object store, one for its data and one for its logs, joined by a single network shared with the backend. Neither service sets a memory or CPU limit, so on a small host the two of them compete with whatever else is running.
The Makefile declares a target it never defines and leaves four targets undeclared
The build file opens with a phony declaration listing backend, frontend, minio, migrate, and all. Two things follow from that line. The target named all is declared and then never written, so invoking it does nothing and reports success. And four targets that do exist further down the file are absent from the declaration: a variant that starts the frontend on all interfaces, one that serves the documentation, one that updates dependencies, and a second object storage variant. A file with no matching recipe behaves as satisfied, which is why the phantom target fails quietly rather than loudly. The phony declaration also covers minio, so the object storage targets are treated as always out of date, which is correct for a server process and not what the declaration appears to be aiming at elsewhere in the list. The migration target shows the same gap in a different form, since it shells out to a migrate binary that is not declared anywhere in the repository, passing a sql extension, a directory pointing into the backend migrations folder, a sequential flag, and a name taken from a make variable, so generating a migration needs a tool the project does not vendor.
The object storage targets predate the service the compose file runs
The compose file starts an object store called rustfs, described in a comment as S3 compatible, with data and log volumes. The Makefile still carries two targets for a different object store entirely, invoking a minio binary directly with a root user and a root password written into the recipe, serving data from a directory in the repository, and putting the console on a separate port. The two targets differ in one meaningful way: the first binds its addresses to localhost, and the second binds them to every interface, on both the server port and the console port, while keeping the same hardcoded credential. So the development convenience path for object storage is the one that exposes it, and both paths are for a product that no longer ships that server in its compose file. Nothing in the root README mentions either target. The feature list, meanwhile, presents four interchangeable object stores as supported backends, which is what makes these two targets read as leftovers rather than as an alternative path.
Speech to text names no provider while the storage pitch is about ownership
The sovereignty argument is made in storage terms. The platform is described as relying on decoupled storage engines to preserve performance without external analytics dependencies, with native compatibility with object stores including RustFS, Garage, MinIO, or AWS, and the feature list promises total ownership over binaries, media streams, and backups. Against that, one writing feature is described as dictating notes directly into the editor using integrated voice-recognition APIs, with no provider named and no statement about whether audio is processed on the device or sent anywhere. That is the single feature in the list most likely to move user content off the machine, and it is the only one whose data path the text leaves entirely open. The rest of the writing features are local by construction: an extended editor, diagrams drawn in the document, a snippet manager, and checkboxes. It is worth being precise about what the ownership claim covers, since data can also leave by three routes the project does document, a reverse proxy in front of the content host, a direct copy out of the bucket, and a zip export of nodes or of the whole platform.
Configuration documentation points twice at a file outside the readme
The root README is short: a positioning paragraph, a feature list, and the quick start. Everything about configuring the stack lives in the example environment file, which is heavily structured with banner comments dividing it into numbered sections, starting with public access and global urls. That file names three public addresses for the browser to reach, for the frontend, the API, and a content delivery address, and a fourth value for the base path inside the content delivery host, carrying a comment that it should match the bucket name and only be changed if the bucket name changed or a reverse proxy path was configured. It also introduces a set of feature flags for turning parts of the interface off, including the landing page and the signup page. A third flag in that group is cut off partway through its name in the visible text, so the full set of switches the project exposes is not readable from the file. Twice the file tells the reader to consult a documentation file in the docs directory, once for explanations of each variable and once for a troubleshooting section.
Three Nuxt dev servers, a Go backend, and a process manager config beside the compose file
The repository carries two deployment models and does not reconcile them. The supported one is the compose stack, and the other is a process manager configuration file at the root, which is the shape a long running service takes under a process supervisor rather than in a container. The build file shows what each half is made of. The backend is a Go program started with go run on its main file, and the compose file sets its port to 8201 and its web framework mode to release, which is why the quick start tells you to open port 8200 for the frontend. The frontend and the documentation site are both Nuxt development servers launched through bunx, with a port of 3001 for the documentation. The dependency update target is the most destructive line in the file, deleting the installed packages, the build cache, and the lock file before running an update, and then tidying the Go modules. A development compose file sits beside the production one, so the two are edited together even though they are meant for different jobs.
Editorial conclusion
Alexandrie suits a team that wants a self-hosted Markdown wiki with per-node permissions, an offline-capable web app, and its own object storage rather than a vendor account, and the three-service stack comes up in three commands. Verify five things before you expose it. Every credential in the compose file has a default that is already in the repository, and the quick start copies the example environment file rather than replacing those values. Only the database image is pinned, so the object store and the backend both track a floating tag. The database and the object store are published on host ports. The Makefile declares a target it does not define and leaves four real targets out of its phony list, and one of its object storage targets binds every interface with a hardcoded secret. Last, the voice input feature names no provider, which matters for a product whose pitch is owning your data.
Frequently asked questions
How do I deploy Alexandrie?
The quick start is three commands: download the example environment file and the compose file with curl, copy the example environment file to .env, then run docker compose up -d. Opening the frontend port at localhost:8200 creates the primary owner account. More detail is in a contributing guide in the repository.
Does the Alexandrie compose file ship with default passwords?
Yes. The database root password defaults to rootpassword, the application database password to password, the object store access and secret keys to alexandrie-key and alexandrie-secret, and the backend signing secret to a placeholder that says to change it. The quick start copies the example environment file rather than replacing those values.
Which images does the default Alexandride stack run?
Three: a database pinned to the 8.0 tag, an S3-compatible object store referenced by a bare latest tag, and the backend pulled from a registry path under the maintainer's account, also on latest. Only the database is pinned to a version.
Which S3-compatible object stores does Alexandrie support?
The feature list names four, describing them as decentralized modern object stores: RustFS, Garage, MinIO, and AWS. The default compose stack runs RustFS, while the Makefile still carries two targets that launch a MinIO binary directly.
What access levels does Alexandrie offer?
Five, from None through Read, Write, Admin, and Owner, applied per node or per workspace. Alongside them the project describes temporary invitation codes, custom scopes, and team allocation tables, plus sharing across organizations through public links or group rules.
What is the Alexandrie backend written in and how is it run?
Go, started in development with go run on its main file, and the compose file sets its port to 8201 and its web framework mode to release. The frontend and documentation are Nuxt development servers launched through bunx, and the project is filed as Vue.
Official sources
Where this project is recommended
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/smaug6739-alexandrie)Star history chart for your README
[](https://hysenlabs.com/projects/smaug6739-alexandrie)Was this useful?