Snapshot v1: a Vue interface whose Docker image serves the dev server
V1 interface for Snapshot. Join us on Discord http://discord.snapshot.org
At a glance
- What is it?
- snapshot-v1 is the Vue front end for the Snapshot governance client, and its build files tell a more honest story than its README does: a testnet hub by default, submodules pulled during install, and a container that ends up running vite dev.
- Who is it for?
- Use this repository if you are building on the Snapshot client and need to see the interface against a real hub, because the dev URL and the testnet default make that a quick job. Do not use it as a reference for production deployment: there are no releases, the container serves the development server, and the README never names the environment variables in .env.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 4 days ago.
- What is it written in?
- Mainly Vue, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
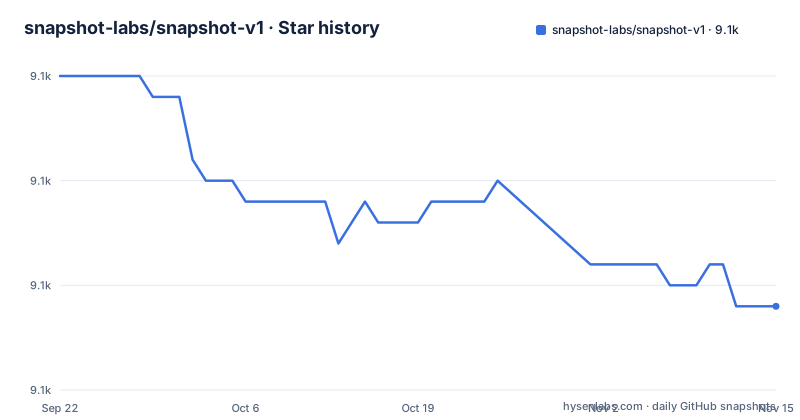
- snapshot-labs/snapshot-v19,074 ★ · -11
| Repository | 2026-09-22 | 2026-11-15 |
|---|---|---|
| snapshot-labs/snapshot-v1 | 9.1k | 9.1k |
-11 Stars in the last 54 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
A fresh checkout points at the testnet hub, not at mainnet
The development guide gives one URL for testing your code, http://localhost:8080/#/fabien.eth, which puts a profile name in the URL fragment and a dev server on port 8080. It also states that by default your instance connects to the hub at https://testnet.hub.snapshot.org, and that you can create a .env.local to overwrite values from .env. That ordering matters for anyone forking this. A checkout with no .env.local is not talking to the production hub, and the README never lists which keys .env holds, so the file you have to inspect is the file you have to copy. Consequence: a fork that forgets the override appears to work while every proposal, vote and space it shows belongs to a test environment.
The container builds for production and then runs vite dev
The Dockerfile starts from node:18-alpine, installs git, python3, gcc, g++, make and pip with apk, copies the tree, runs yarn install --frozen-lockfile, runs it a second time, then runs yarn run build. After all that it exposes 8080 and ends with a command of yarn run dev --host. The dev script in package.json is vite --port=8080, so the container serves the development server bound to every interface, not the artefact that was just compiled. Consequence: anyone who runs docker run --name snapshot -p 8080:8080 snapshot is running a hot-reloading dev server, and the duplicate install line costs a full dependency pass on every image build.
yarn install is what pulls the git submodules
package.json wires the install lifecycle to the repository state. preinstall runs yarn run init-submodules, which is git submodule update --init, and postinstall runs patch-package and then husky install. The tree contains a .gitmodules file, a .husky directory and a top level snapshot-spaces entry, so a correct checkout depends on all three existing as git things rather than as loose files. Consequence: an install from a tarball has no git to update, and an install without yarn on the path fails inside the preinstall script even if the package manager you chose is something else. Install also mutates your checkout by patching packages and installing hooks.
There are no releases and no tags to pin
The repository has no GitHub releases, and the only version anywhere is the version field in package.json, which reads 0.1.4. That number has no published artefact behind it. It is not tied to a deploy, a tag or a changelog, so it tells a consumer nothing about which state of the interface they are looking at. Consequence: if you need a fixed copy of this front end for your own product, you have to pin a commit hash and re-pin it yourself, and you get no release notes telling you what moved. The project is not archived and the last push is dated 2026-09-14, so the code moves while the version field does not.
The voting logic lives in snapshot.js, not in this repository
The description calls this the V1 interface for Snapshot and the primary language is Vue, and the governance behaviour itself is imported. package.json depends on @snapshot-labs/snapshot.js at ^0.17.2, @snapshot-labs/lock at ^0.2.11 and @snapshot-labs/pineapple at ^1.1.0, and extends the @snapshot-labs/vue eslint config plus @snapshot-labs/prettier-config. All three are caret ranges, so a fresh install can pull a newer SDK than the one this interface was written against. Consequence: an upgrade that changes how a vote is read or signed can arrive through a lockfile refresh with no commit here at all.
Two dependencies break the caret convention on purpose
Almost everything in dependencies uses a caret range. Two entries do not: @shutter-network/shutter-crypto is written as the exact string 1.0.1 with no range prefix, and @vue/apollo-composable is 4.0.0-beta.11, a beta. The rest of the client runs on @ethersproject packages at version 5, @apollo/client at ^3.8.7 and @sentry/vue at ^7.80.1. Consequence: the exact pin means a fix in the crypto helper has to be taken deliberately, by editing package.json and refreshing yarn.lock, and the beta means the GraphQL layer rests on a pre-release version. Neither choice is explained anywhere in the README.
Vitest is wired up, and the README stops at lint
The setup section of the README covers four commands and nothing else:
yarn
yarn dev
yarn build
yarn run lint
package.json nevertheless defines test:unit as vitest run and test:unit:coverage as vitest run --coverage, alongside lint:fix as yarn lint --fix. A contributor who follows the README never learns the test command exists. There is no end-to-end path in the repository either, which is the awkward part for a governance interface where the failures that matter come from hub reads, ENS name resolution and wallet signing rather than from component rendering. The tree also carries crowdin.yml, vercel.json and .gitpod.yml, none of which is explained in the README.
Editorial conclusion
Use this repository if you are building on the Snapshot client and need to see the interface against a real hub, because the dev URL and the testnet default make that a quick job. Do not use it as a reference for production deployment: there are no releases, the container serves the development server, and the README never names the environment variables in .env. If you fork it, write .env.local against your own hub before you judge any behaviour, and read the pinned shutter-crypto version and the beta apollo-composable before you trust a vote result.
Frequently asked questions
How do I run the Snapshot v1 client locally?
Install with yarn, then start the dev server with yarn dev, which runs vite on port 8080, and open http://localhost:8080/#/fabien.eth. The Docker route is docker build -t snapshot . followed by docker run --name snapshot -p 8080:8080 snapshot.
Which hub does Snapshot v1 talk to by default?
By default it connects to the hub at https://testnet.hub.snapshot.org. The README says you can create a .env.local and overwrite the values from .env to change that or any other value.
Is there a released version of snapshot-v1 I can pin to?
The repository has no GitHub releases. The only version is 0.1.4 in package.json, which is not tied to a tag or a published artefact, so pinning a commit is the only fixed option.
Does the Snapshot v1 Docker image run a production build?
No. The Dockerfile runs yarn run build and then ends with a command of yarn run dev --host, which is the vite development server from the dev script, bound to all interfaces on port 8080.
Why does installing snapshot-v1 touch my git checkout?
The preinstall script runs yarn run init-submodules, which is git submodule update --init, and postinstall runs patch-package and husky install. The repository has a .gitmodules file, a .husky directory and a snapshot-spaces entry.
Where is the governance logic used by snapshot-v1 kept?
It is imported rather than included. package.json depends on @snapshot-labs/snapshot.js at ^0.17.2, @snapshot-labs/lock at ^0.2.11 and @snapshot-labs/pineapple at ^1.1.0, so the behaviour behind a vote is maintained in separate repositories.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/snapshot-labs-snapshot-v1)Star history chart for your README
[](https://hysenlabs.com/projects/snapshot-labs-snapshot-v1)Was this useful?