solo: a Go module path pointing at a different GitHub owner
Solo Agent — an open-source, local-first workspace where humans and AI coding agents collaborate through channels, tasks, teams, and persistent memory.
At a glance
- What is it?
- solo-agent/solo is a Go and Next.js workspace that puts five coding agent CLIs behind channels, task boards and per-agent memory files, but its go.mod declares a module under a different organisation than the repository it lives in, its compose file runs nothing but PostgreSQL so the daemon can reach your local agent binary, and its root package.json is a Playwright harness whose test script always exits non-zero.
- Who is it for?
- solo has made a choice that most agent tooling avoids: it does not embed a model, it supervises the CLI you already have. That means your existing authentication keeps working, five backends are supported through three different wire protocols, and the thing running on your machine is a binary you recognise.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 68 days ago.
- What is it written in?
- Mainly Go, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 20, 2026, and from our analysis. They are not legal advice.
Star history
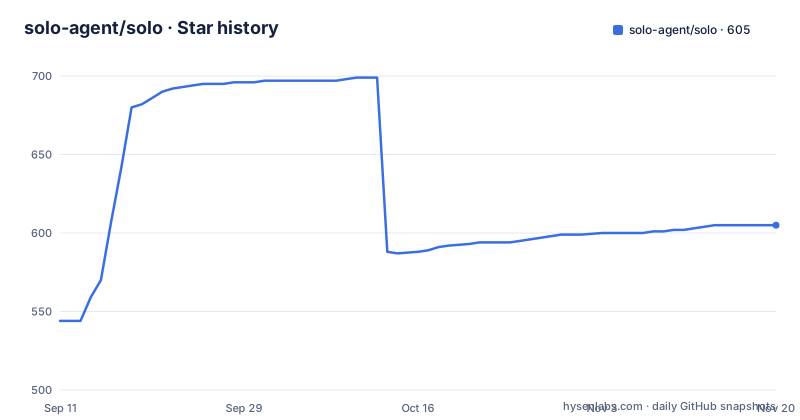
- solo-agent/solo605 ★ · +61
| Repository | 2026-09-11 | 2026-11-20 |
|---|---|---|
| solo-agent/solo | 544 | 605 |
61 Stars in the last 70 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The module path and the clone URL name different owners
The clone instruction is `git clone [email protected]:solo-agent/solo.git`, and the repository lives under the `solo-agent` organisation. The `go.mod` at the root declares `module github.com/solo-ai/solo`. Those are two different account names, so the import path inside every Go source file does not match where the code is fetched from. Nothing about the build requires them to agree, since Go resolves dependencies by module path and the repository is fetched by clone URL, so this is not a broken install waiting to happen. It is the kind of thing that costs an afternoon the first time a dependency tool tries to map one to the other, and it is the sort of rename that is cheap to fix now and expensive to change after downstream users have vendored the path. The root `package.json` has its own drift, carrying version `1.0.0` while the newest release tag is `v1.1.0` from 2026-08-14, five days after `v1.0.0`.
Five backends, three wire protocols, detected from PATH
The integration table is the part of this project that does the real work, and it is not uniform:
| Backend | CLI binary | Protocol | | --- | --- | --- | | Claude Code | `claude` | stream-json | | Codex CLI | `codex` | JSON-RPC | | OpenCode CLI | `opencode` | ACP | | Hermes CLI | `hermes` | ACP | | OpenClaw Agent | `openclaw` | ACP |
So there is one adapter speaking a JSON stream, one speaking JSON-RPC, and one shared protocol covering the remaining three. Backends are auto-detected from your `PATH` at daemon startup rather than configured by hand, which is why at least one supported agent CLI has to be on the path before the daemon starts. Each agent can then override `system_prompt`, `model_name`, `custom_env`, and `custom_args`, so two agents running the same binary can be different agents. The product framing in the documentation is a single line about the contract: if it can receive a heartbeat, it is hired.
Only PostgreSQL is containerised, because the daemon needs your CLI
The compose file is small and the reason is stated in a comment at the top. Only PostgreSQL runs in Docker, on `postgres:16-alpine` with the database, user, and password all set to `solo`, the password being `solo-dev`, the port published as `5432:5432`, and a `pgdata` volume. Server and Daemon run natively, and the reason is that they need access to the local `claude` binary for `LLM_PROVIDER=local` mode. That is a coherent constraint rather than an oversight: a container cannot reach a subprocess on your host without extra plumbing, and the whole point of this design is to spawn your installed CLI. The consequences are worth stating plainly. The database port is exposed to the host on a well-known number with a known development password, so this stack is for a laptop and not for a shared machine. And both services run as your user account, which is also why the daemon is the process with access to everything you have authenticated to.
The runtime image is the Go toolchain, not a slim base
The Dockerfile builds in `golang:1.25-alpine` and then runs in `golang:1.25-alpine` again, with a comment saying the second stage reuses the base because it is already cached. That is a build-speed decision and it has a size and surface consequence: the shipped image contains the Go compiler and the module cache, not just the four binaries copied into it. Four are built, with `CGO_ENABLED=0 GOOS=linux` and stripped debug info, from `./cmd/server/`, `./cmd/daemon/`, `./cmd/solo/`, and `./cmd/migrate/`, so the daemon and the migration runner are separate programs rather than subcommands. The runtime stage adds a non-root `solo` user, copies those binaries plus the `migrations` directory, exposes 8080 and 8081, and defaults to running the server. If you containerise the whole thing rather than running it natively, that is the image you get.
Two vendor SDKs pinned to exact patch versions
The direct requirements are short and mostly infrastructure: `go-chi/chi/v5` for routing, `go-chi/cors`, `golang-jwt/jwt/v5`, `google/uuid`, `gorilla/websocket`, `jackc/pgx/v5` for PostgreSQL, and `golang.org/x/crypto`. Two of them are not: `github.com/larksuite/oapi-sdk-go/v3` at `v3.9.9`, and two entries from the Tencent Cloud SDK at `v1.3.136` each, one for the common package and one for `ses`, which is the transactional email service. So the binary ships a Lark messaging client and a Tencent email client, both pinned to an exact patch release rather than a minor or major range, inside a project described as local-first. That footprint is consistent with a workspace that sends notifications to chat and email, and the exact pins are consistent with a team that would rather not discover a transitive change in a notification path. It is still a larger dependency surface than the rest of the list implies.
Persistent memory is one MEMORY.md per agent
The concept table defines memory narrowly: agent-specific `MEMORY.md` context loaded into future sessions. That is the whole mechanism, a markdown file per agent, and it is worth saying plainly because "persistent memory" in this space usually means a database, an embedding store, or a summarisation pipeline. Here it does not. The third layer of the architecture explains where it fits: the agent CLI is your installed coding agent reading stdin and stdout, while Solo supplies the prompt, the memory, and the collaboration tools. So the memory file is something the agent's own runtime loads, not something Solo injects as a database query. The other concepts follow the same plainness. Channels are shared rooms. Tasks are Kanban items with five states, `todo`, `in_progress`, `in_review`, `done`, and `closed`. Teams are channel-scoped graphs of roles and ownership. Artifacts are generated outputs that can be reviewed and published.
Thinking mode forks a conversation, and it has its own design document
The one feature with a dedicated architecture file at the repository root is thinking mode, described as branching a channel conversation into focused lines of reasoning, keeping each branch in its own context, and returning useful conclusions to the parent discussion without losing the bigger picture. The design document for it is `THINKING_MODE_ARCHITECTURE.md`, checked in beside `AGENTS.md` and `SECURITY.md`. The rest of the workflow is described as making message-shaped work trackable: every task keeps its discussion thread attached to its Kanban card, so assignment, subtasks, review, artifacts, and history move together. Team creation is also conversational, where you pick an official workflow or describe a goal to a template assistant, preview the roles and relationships, and then create agents scoped to a single channel. The stated design intent is worth quoting as a boundary: Solo is a workspace, not a company simulator.
The root package.json is a Playwright harness with a placeholder test
The root `package.json` is named `solo` at version `1.0.0`, typed as commonjs, with no keywords, no author, and a single `test` script that is the stock placeholder npm writes into a new package, echoing an error and exiting 1. Running `npm test` at the root therefore always fails, by the template's design rather than the project's. Its two dependencies are `playwright` and `@playwright/test`, both at `^1.60.0`, which makes the file's real job clear: this is the end-to-end test harness for the Next.js frontend, not the manifest for the application. The everyday commands live in the Makefile instead:
make          # Show all targets
make start    # Start services
make stop     # Stop services
make rebuild  # Rebuild binaries and restart
make db-reset # Reset the local database
The Go code is built from `cmd/` with its own module, so the two toolchains coexist without either package.json describing the other. Also committed at the root are `.env.example` and `.env.production`, alongside `deploy/`, `docker-compose.yml`, `.goreleaser.yml`, `docs/`, `evals/`, `skills/`, `internal/`, `pkg/`, `frontend/`, `migrations/`, and `scripts/`.
Editorial conclusion
solo has made a choice that most agent tooling avoids: it does not embed a model, it supervises the CLI you already have. That means your existing authentication keeps working, five backends are supported through three different wire protocols, and the thing running on your machine is a binary you recognise. It also means the workspace inherits every difference between those CLIs. Before committing, check three things. Whether the module path mismatch between `go.mod` and the repository URL affects your build tooling, since import paths and clone URLs do not have to agree but surprises are annoying. Whether you accept that only PostgreSQL is containerised and the daemon runs natively with access to your agent binary, which is the only way that integration can work. And whether you want an enterprise email SDK and a Lark SDK pinned to exact patch versions inside what is described as a local-first tool.
Frequently asked questions
What is Solo Agent?
An open-source, local-first workspace where humans and AI coding agents collaborate. It does not embed a model; it supervises the coding CLIs you already have, and gives them shared channels, threaded conversations, task boards, channel-scoped team graphs, and per-agent memory.
Which coding agents does Solo Agent support?
Five, auto-detected from your PATH when the daemon starts: Claude Code through the `claude` binary over stream-json, Codex CLI through `codex` over JSON-RPC, and OpenCode, Hermes, and OpenClaw through their own binaries over ACP. Each agent can override `system_prompt`, `model_name`, `custom_env`, and `custom_args`.
How do I run Solo Agent locally?
You need Go 1.25+, Node.js 20+, npm, Docker, and at least one supported agent CLI on PATH. Then clone the repository, `cd solo`, and run `make dev`, which creates `.env`, installs frontend dependencies, starts PostgreSQL, runs migrations, and launches the app at `http://localhost:3000`. `make`, `make start`, `make stop`, `make rebuild`, and `make db-reset` are the everyday commands.
Does Solo Agent run its coding agents inside containers?
No. The compose file brings up only PostgreSQL, on `postgres:16-alpine`, and the documentation states that the Server and Daemon run natively because they need access to the local `claude` binary for `LLM_PROVIDER=local` mode. The agent subprocess is spawned by your daemon as your own user.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/solo-agent-solo)Star history chart for your README
[](https://hysenlabs.com/projects/solo-agent-solo)Was this useful?