Sync-in runs as 8888, ships two entrypoints and reserves its own name
Sync-in · Sovereign platform for file storage, sharing, synchronization, and collaboration.
At a glance
- What is it?
- Sync-in is a self-hosted file storage, sharing and collaboration server written in TypeScript, published under AGPL-3.0-or-later with a registered trademark behind the name. The Docker image, the npm workspaces and the keyword list each describe a slightly different product, and the differences are where an adopter has to look first.
- Who is it for?
- Sync-in fits a team that wants its own file server with collaboration on top and files left readable on a filesystem, and that runs Docker on a Linux host rather than Windows, since the image assumes a Linux user table and the root npm package explicitly refuses to install on win32. Three checks come first.
- Can I use it commercially?
- Yes, with strict conditions. AGPL-3.0 is a network copyleft licence: if people use a modified version over a network, for example as a hosted service, you must offer them its source code under the same licence.
- Is it still maintained?
- Yes. The repository last received commits 4 days ago.
- What is it written in?
- Mainly TypeScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 21, 2026, and from our analysis. They are not legal advice.
Star history
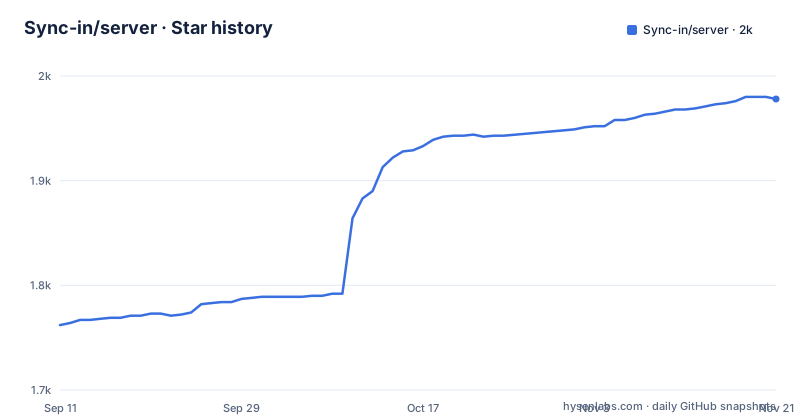
- Sync-in/server1,978 ★ · +216
| Repository | 2026-09-11 | 2026-11-21 |
|---|---|---|
| Sync-in/server | 1.8k | 2k |
216 Stars in the last 71 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The npm badge names @sync-in/server, the root manifest is private
The README links to an npm package called @sync-in/server, while the root package.json declares the name sync-in-server and marks the package private, which is what stops it being published. What is published comes out of the workspaces instead, and the root manifest lists exactly two of them, backend and frontend, with build running across both. Two further declarations shape where this can be installed. The os field reads !win32, so npm refuses this package on Windows, and engines requires Node 22 or later, while the container image is built on node:24-alpine. So the supported paths are the Docker image on a Linux host, or an npm install on macOS and Linux. The keyword list is unusually long for a server and includes crdt, collaborative-editing and realtime, which the feature list never explains, and then nextcloud, owncloud and dropbox, which place the project against named competitors in the package metadata itself.
The image exports a health URL that the healthcheck does not call
The container declares a readiness address and a separate probe, and they are two different mechanisms:
ENV SYNC_IN_HEALTHCHECK_URL=http://127.0.0.1:8080/healthz/ready
HEALTHCHECK --interval=30s --timeout=5s --start-period=60s --retries=3 \
    CMD ["node", "server/infrastructure/availability/scripts/check-health.js"]
So the address is exported as an environment variable for the application to bind, while the healthcheck itself launches a Node script from inside the server directory rather than requesting that address with curl or wget. Nothing in the image installs a client, which is consistent with the second choice, and it means the probe logic lives in the application rather than in the container runtime. The timings are worth noting for any orchestrator wrapping this: a 30 second interval, a 5 second timeout, a 60 second grace period before the first failure counts, and three retries before the container is called unhealthy. A database migration on first boot therefore has a full minute before it can mark a healthy instance as failing.
The process runs as 8888 and changes user twice
Privilege handling is explicit. The runtime stage installs su-exec, creates /app/data and /app/environment, and exports PUID and PGID with a default of 8888. Everything copied into the image is chowned to 8888:8888, and only the two shell scripts are given mode 755, which is what lets entrypoint.sh drop from root to those ids before the server process starts. That gives two processes rather than one: ENTRYPOINT is ./entrypoint.sh and CMD is ./sync-in-server.sh, so the entrypoint wrapper is what runs as root and the server wrapper is what runs as 8888. Both come from the scripts/ directory in the build context, docker-entrypoint.sh and docker-sync-in-server.sh. For an operator overriding PUID and PGID, the consequence is that those two scripts are the place the change is applied, and the host directories mounted at /app/data have to be writable by whatever ids end up there.
Migrations and config ship beside the build output, not inside it
The build stage compiles everything, then prunes: npm ci, npm run build, npm run reset, and finally a second install scoped to the backend workspace with dev dependencies omitted and audits and funding messages switched off. That last command is what keeps a full toolchain out of the runtime image, since node_modules is then copied wholesale from the build stage. What lands in /app is laid out by hand. dist/ becomes the working directory, package.json goes to server/, the node_modules tree is copied as is, backend/migrations is copied to a top-level migrations directory, and environment/environment.dist.yaml arrives as the configuration template beside it. Two consequences follow. The migration files are not part of the compiled output, so a schema upgrade path exists outside the bundle, and the packaged configuration is a dist file, which means an operator edits a copy rather than the source of truth.
Three office suites, four authentication methods and one keyword that is unexplained
Online editing is delegated rather than implemented, and to three separate products: Collabora Online, OnlyOffice and Euro-Office are all named as the editors behind the feature. Each is a document server an operator has to run, so the count of those containers is the real cost of the collaboration half of the product. Authentication is broader still, with local accounts, OIDC, LDAP, MFA, recovery codes and application passwords, which is the combination that makes it usable as an internal system of record rather than a personal drive. Against that, the keywords advertise crdt and collaborative-editing, and the README never explains what synchronises concurrent edits, since the visible design hands the document to an external suite. Search is described as full-text with deep indexing into common office and document formats, and the filesystem stays readable underneath, with shares, spaces, roles and folder anchoring added on top.
AGPL with a trademark on the name
The licence is the GNU Affero General Public License, at or later, with the text in a LICENSE file at the root and the same identifier in the manifest as AGPL-3.0-or-later. That matters for a file server more than for a library, because the Affero variant is the one written for network use: offering the modified service to users over a network is what brings the source obligation in. The second half of the licensing picture is separate and easier to miss. The README states that Sync-in is a registered trademark and points to a trademark policy on the project site, so the code is available under AGPL while the name is not. Nothing in the repository spells out how the two interact for an operator who wants to rebrand a fork, and the policy is a web page rather than a file in the tree, which is exactly the document to read before an internal deployment rather than after.
Windows code signing, and a package that will not install on Windows
Two sponsor arrangements appear in the README, and one of them is for a platform the server package excludes. Free code signing on Windows is provided by SignPath.io with a certificate from the SignPath Foundation, which is what lets the desktop and command line clients be distributed without a self-signed warning on Windows. The second is the Docker-sponsored open source programme. The clients themselves are a separate repository, Sync-in/desktop, covering Windows, macOS and Linux with multi-server synchronisation workflows. The split explains an oddity in the server manifest: os is set to exclude win32, so the server package is Linux and macOS only, while the client that is code signed for Windows ships from elsewhere. It also explains the WebDAV entry in the feature list, which is the route by which a Windows machine without a client still reaches the server.
Editorial conclusion
Sync-in fits a team that wants its own file server with collaboration on top and files left readable on a filesystem, and that runs Docker on a Linux host rather than Windows, since the image assumes a Linux user table and the root npm package explicitly refuses to install on win32. Three checks come first. The licence is AGPL-3.0-or-later, which is a different obligation from MIT or Apache, and the name Sync-in is a registered trademark with its own policy, so rebrand and network deployment questions should be settled before, not after. Second, document editing is delegated to three separate office suites, Collabora Online, OnlyOffice and Euro-Office, and how many of them you have to run is the largest operational decision here. Third, the published package name in the README badges is @sync-in/server while the root manifest is a private package called sync-in-server, so pinning the wrong name in a Dockerfile will fail. Version 2.5.2 was released on 2026-09-21 and the last commit on main is dated 2026-10-02.
Frequently asked questions
What is Sync-in and what does it replace?
Sync-in is a self-hosted platform for file storage, synchronization, sharing and team collaboration, run as your own workspace so the infrastructure and the data stay under your control. Its npm keywords place it alongside nextcloud, owncloud and dropbox, and it offers WebDAV alongside its own desktop and CLI clients for Windows, macOS and Linux.
What licence is Sync-in released under?
The GNU Affero General Public License, at or later, recorded in the manifest as AGPL-3.0-or-later with the text in a LICENSE file at the root. Sync-in is also a registered trademark with a separate trademark policy, so the code licence and the name are governed separately.
How does the Sync-in Docker image run its healthcheck?
The image exports SYNC_IN_HEALTHCHECK_URL pointing at the readiness endpoint on port 8080, and its HEALTHCHECK runs a Node script from the server directory with a 30 second interval, a 5 second timeout, a 60 second start period and three retries. The probe is the application script rather than a request made by a client in the image.
Which document editors can Sync-in use for online editing?
Online document editing is handled by external office suites: Collabora Online, OnlyOffice and Euro-Office are all named as supported. Authentication is handled separately, with local accounts, OIDC, LDAP, MFA, recovery codes and application passwords.
What are the system requirements for running Sync-in?
The npm package requires Node 22 or later and excludes Windows through its os field, while the container image is built on node:24-alpine. The image runs the process as 8888 with PUID and PGID overrides, exposes port 8080, and copies migrations and a distribution configuration file beside the compiled output.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/sync-in-server)Star history chart for your README
[](https://hysenlabs.com/projects/sync-in-server)Was this useful?