The OpenClaw Control Center ships read-only with mutation routes off, and its container binds every interface anyway
Turn OpenClaw from a black box into a local control center you can see, trust, and control.
At a glance
- What is it?
- TianyiDataScience/openclaw-control-center is a TypeScript dashboard that puts a local view of OpenClaw's health, usage, staff, tasks, documents and memory behind a browser interface, with a multi-agent hall that dispatches through the real agent runtime. Its defaults are deliberately conservative, but the Docker image sets the bind address to all interfaces and the manifest is version 1.0.0 with no published releases.
- Who is it for?
- This control center fits a team running OpenClaw on one machine that wants an operator view rather than log payloads, and it fits an operator who should not have to learn the backend's response shapes to answer whether work is moving. It does not fit a shared or exposed deployment without changes, because the container is built to listen on every interface and the read-only posture is a default rather than an enforced mode.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Activity is slowing. The repository last received commits 7 months ago.
- What is it written in?
- Mainly TypeScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
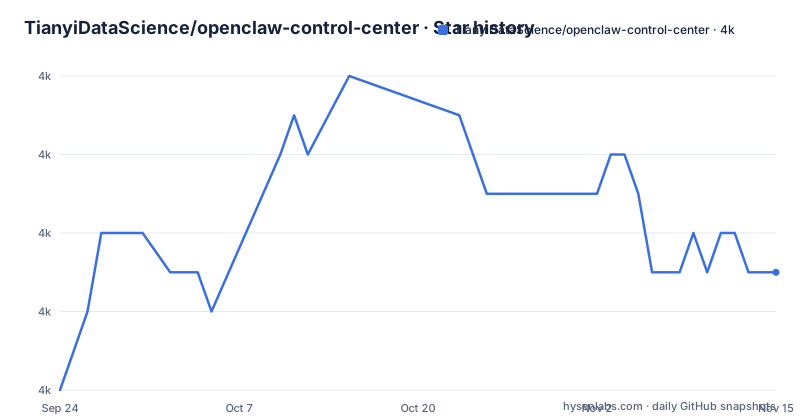
Star history
- TianyiDataScience/openclaw-control-center3,997 ★ · +3
| Repository | 2026-09-24 | 2026-11-15 |
|---|---|---|
| TianyiDataScience/openclaw-control-center | 4k | 4k |
3 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The default posture is read-only, and the environment file repeats it
The three defaults are stated as a group, and they are the design argument in three lines: read-only by default, local token authentication by default, and mutation routes disabled by default. The audience explains them. The project says it is built for non-technical operators who need observability and certainty rather than raw backend payloads, and a read-only dashboard is what you can hand to such a person. The environment template carries the same instruction as a comment next to its flags, telling you to keep read-only enabled until explicit live-mode validation is complete. That is an unusually direct instruction to keep a safety switch on, and it is the kind of comment that survives long after the reason for it has been forgotten. The first variable in the file is the gateway address, a websocket endpoint on the local machine, so what this thing talks to is a local runtime rather than a remote service.
One entry point, selected by an environment variable or a command name
There is a single source entry file, and the manifest reaches it many different ways. The development script runs it with a TypeScript loader and no flags at all, which per the notes performs exactly one monitor pass and does not start the interface, so it is a check rather than a server. Two neighbours add behaviour through an environment variable: one sets a continuous monitoring flag, the other turns on interface mode and is described as the more reliable cross-platform entry, especially on Windows shells. Then a set of maintenance operations is invoked by setting a command variable and running the same file, covering a backup export, an import validation, pruning acknowledgements and a task heartbeat. Tests, two smoke scripts and a set of validators run separate script files. So the entry point is shared, the mode is a variable, and a mistake there looks like a server that never listens.
Seven commands get you to a browser page
The getting started path is short enough to quote in full, which is unusual for a project of this size and tells you what the author considers the real setup cost:
npm install
cp .env.example .env
npm run build
npm test
npm run smoke:ui
npm run smoke:hall
npm run dev:ui
Two URLs follow, both on the same port with a different language parameter, one English and one Chinese, and the interface can be pointed at a remote host for access over a private network by setting the control interface URL variable. Two cautions belong with that list. The environment file is copied rather than created, which means the defaults you just accepted are the shipped ones, and the two smoke scripts are not decoration: one exercises the interface and one exercises the hall release flow, so a green pair is the closest thing to an end-to-end check this project documents.
Saving the execution order deliberately does not start execution
The hall workflow section is the most precise document in the readme, and it is worth following exactly because the steps are separated more than you would expect. You start with one task in the hall, and the first turn stays in a discussion state. Unless you explicitly mention one agent, the hall aims to collect at least two short replies, so a second person adds an angle rather than repeating the first. You arrange an execution order, choosing the first owner, the later owners and what each hands off, and here is the sentence that matters: saving that order does not start execution. A separate decision card shows a start command, and only that starts the queue. During execution each owner finishes only their own step and then visibly mentions the next. Review happens after the last queued owner finishes or when a human stops it. Then continue discussion reopens the same thread for another round.
The hall prefers live output and falls back to stored history
The release notes are unusually specific about how the hall reaches the runtime, and the details are all configurable. Hall discussion, assignment and handoff can dispatch through the real agent runtime, so what you see in the draft stream is real session execution rather than text the orchestrator generated. Streaming prefers a direct pass-through of the runtime's standard output when OpenClaw emits live output, and falls back to differences in the stored session history when the runtime only exposes persisted updates. The template names the switches: dispatch enabled, direct streaming enabled, a thinking level set to minimal, a timeout in seconds, a poll interval in milliseconds, a history limit, execution chains enabled, and a maximum number of turns per chain, set to three. One line deserves emphasis: leaving dispatch enabled gives the full experience, and disabling it exists to produce deterministic synthetic replies for testing.
Two lock files, and the scripts belong to the other package manager
The repository carries two lock files at the root, one for the npm client and one for a different client, while every script in the manifest uses the npm one, including the clean install inside the container build. That is not necessarily a mistake, since a project can accept patches from contributors using either client, but it does mean the reproducible build is defined by only one of them and a contributor using the other will produce a different tree. The manifest is small in other revealing ways. The project type is the CommonJS one, even though the source is TypeScript and is run through a loader rather than compiled on the fly, and the compiled output is produced by a single type-check-and-emit invocation. Validation is split into two named checks with a combined script, and there is a release audit script written as a shell script, which is the only shell entry point in an otherwise Node-based workflow.
The container listens on every interface, and copies a directory nothing builds
The image is built in two stages on the slim Node 22 Debian base. The build stage installs dependencies from the lock file, compiles, and exports avatars, which is the step that produces the staff-page images described in the screenshots. The runtime stage copies only the manifest, the compiled output, a directory called runtime, the environment example, both readmes, the hall guide and the documentation, then sets four environment values before exposing one port. Two of those are the problem. Interface mode is on, and the bind address is set to all interfaces, so the container listens on every network the host has rather than the loopback alone; the readme repeats that default outside containers too, so it is deliberate. The other problem is the copied runtime directory: no build step in the manifest names it, and no such directory appears in the repository's file listing, so either a step is missing from the scripts or the image build expects something the repository does not contain.
Bilingual documentation, and two install prompts
The repository carries three readme files: the default one, an English one and a Simplified Chinese one, with a language switch at the top of the default file. That is more than most small dashboards do, and it is consistent with the interface itself, which is reachable with a language query parameter and renders both. Then there are two installation prompt documents, one default and one English, sitting next to each other in the root, which suggests the intended onboarding path is that an assistant or operator pastes a prompt rather than following a manual. A compose file example, a process manager configuration for running the service under a supervisor, and a documentation directory complete the set. The hall guide file at the root is not documentation in that sense: it is read by the application at runtime on every turn, and it is injected into discussion, execution and handoff without being allowed to override routing.
Editorial conclusion
This control center fits a team running OpenClaw on one machine that wants an operator view rather than log payloads, and it fits an operator who should not have to learn the backend's response shapes to answer whether work is moving. It does not fit a shared or exposed deployment without changes, because the container is built to listen on every interface and the read-only posture is a default rather than an enforced mode. Two things to check before you put it anywhere reachable. What your first-run defaults actually are on your install, since the environment template tells you to keep read-only enabled until live-mode validation is complete, and the bridge variables that mirror room events to Discord or Telegram, which are commented out and easy to uncomment by accident. And which entry point you launch, because one script starts a single monitor pass and never serves the interface, which is a confusing first failure.
Frequently asked questions
What is OpenClaw control UI?
It is the browser interface of the OpenClaw Control Center, a local dashboard for OpenClaw with pages for overview, usage, staff, collaboration, tasks, documents and memory. It runs on port 4310 by default and is started with the script that turns on interface mode, which the readme recommends over the plain development script because that one only performs a single monitor pass.
How do I access my OpenClaw dashboard?
Follow the five-minute start: install dependencies, copy the environment example to your own file, build, run the tests and the two smoke scripts, then start the interface. Open the overview page at the local address on port 4310 with a language parameter of en or zh. To reach it from another machine, set the control interface URL variable to your host address, noting that the interface binds to all interfaces unless you override the bind address.
Is OpenClaw Control Center safe to run on a local machine?
Its first-run defaults are conservative: read-only by default, local token authentication by default, and mutation routes disabled by default, with the environment template telling you to keep read-only enabled until explicit live-mode validation is done. Two things to note before exposing it: the interface binds to all interfaces unless you set the bind address, and the environment file contains commented variables for mirroring room events to a Discord webhook or a Telegram bot.
How do I run the OpenClaw Control Center tests?
The test script runs a Node test runner through a TypeScript loader, and there are two separate smoke scripts: one for the interface, written as plain JavaScript, and one for the hall release flow, written in TypeScript. Validation of the task store and of budget computation are separate scripts, and a combined validation script runs both, which is the one to use before publishing.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/tianyidatascience-openclaw-control-center)Star history chart for your README
[](https://hysenlabs.com/projects/tianyidatascience-openclaw-control-center)Was this useful?