OpenClaw Dashboard: two default ports, one recovery token, and the host Docker socket
🔐 Secure, real-time monitoring dashboard for OpenClaw AI agents. Auth, TOTP MFA, cost tracking, live feed, memory browser and more.
At a glance
- What is it?
- A single server.js plus index.html reads an OpenClaw install and draws the session, cost and system panels from it. The two setup paths disagree on the port, the recovery token lives only in the startup output, and the Docker page wants the host socket.
- Who is it for?
- It fits a single operator on a box where the OpenClaw install is theirs: two files to run, no database, no npm packages, and panels for sessions, costs, cron jobs and memory files. It is a poor fit for a shared or internet reachable host, because the image enables plain HTTP at build time, the Docker page asks for the host socket, and the setup steps name no way to bind the server to a Tailscale address or to a certificate.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 10 days ago.
- What is it written in?
- Mainly HTML, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
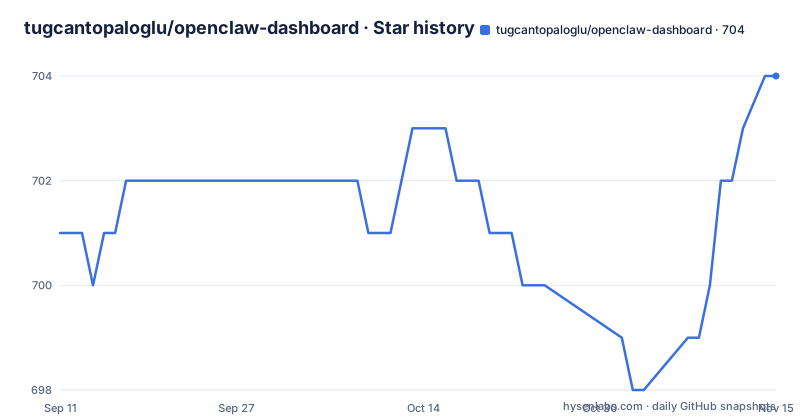
- tugcantopaloglu/openclaw-dashboard704 ★ · +3
| Repository | 2026-09-11 | 2026-11-15 |
|---|---|---|
| tugcantopaloglu/openclaw-dashboard | 701 | 704 |
3 Stars in the last 65 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The recovery token is printed once and never filed anywhere
Everything about the credential lifecycle happens in the first minute of a run. Starting the server prints two lines:
🚀 Dashboard running on http://localhost:7000
🔑 Recovery token: abc123def456...
The README says to save that token because you will need it if you forget your password. Nothing else in the setup steps covers it: no command reprints it, no page shows it once you are logged in, and no path is given for the file that holds it. `sudo ./install.sh` also generates one, and on that path the line lands in the systemd journal instead of a terminal, so the recovery credential exists only inside journal output and whatever was copied out of it. Password storage itself is described as PBKDF2 hashing, TOTP MFA is optional and Google Authenticator compatible, and Remember Me offers a session-only login or a 3-hour persistent one. Those three settings are the whole documented auth surface; rotation, revocation and expiry of the recovery token are not part of it.
Port 7000 on the host, 3001 in the image, HTTP already allowed
The access step after `node server.js` points at `http://localhost:7000`, and the environment variable table lists `DASHBOARD_PORT` with the default `7000`. The container path uses a different number. The Dockerfile sets three values at build time:
ENV NODE_ENV=production
ENV DASHBOARD_PORT=3001
ENV DASHBOARD_ALLOW_HTTP=true
It exposes 3001 and runs a healthcheck against `http://127.0.0.1:${DASHBOARD_PORT:-3001}/` every 30 seconds with a 5 second timeout. Both `docker run` examples map 3001:3001 and pass `-e DASHBOARD_ALLOW_HTTP=true` again, so the flag is redundant when the published image is used and inherited silently when the image is built from the Dockerfile. What that flag changes is never spelled out: the environment variable table ends at the `DASHBOARD_PORT` row, and no step describes server behaviour when the flag is absent, even though the feature list advertises HSTS, CSP, rate limiting, timing-safe comparisons and audit logging. The optional variables are more concrete:
export DASHBOARD_PORT=7000
export WORKSPACE_DIR=/path/to/your/workspace
export OPENCLAW_DIR=$HOME/.openclaw
export OPENCLAW_AGENT=main
So `DASHBOARD_ALLOW_HTTP` ships enabled in the image and defaults to nothing documented, which is the single fact to carry into any deployment.
Only the second run command gives the Docker page what it needs
Two `docker run` commands appear, and only the second one enables the Docker Management page, which the feature list describes as viewing containers, images and system usage, starting, stopping and restarting containers, and pruning unused resources. The gap is the socket. The first command mounts the OpenClaw directory read-only and the workspace read-write, and nothing more. The second adds two lines:
  -v /var/run/docker.sock:/var/run/docker.sock:ro \
  --group-add $(stat -c '%g' /var/run/docker.sock) \
They sit next to each other and both are needed: the image installs the Docker CLI with `apk add --no-cache docker-cli curl`, and the optional dependency table names `jq` for that same page. Read the pair as the question it is, because a Docker socket is the control plane of the host, and whether a read-only mount plus group membership is acceptable on a given machine is a decision the setup steps never address. The group lookup also uses the GNU form `stat -c '%g'`, while macOS ships a different `stat`, and the macOS support claim in the feature list is scoped to system stats, services and memory reporting rather than this command. Two mounts of the same host tree appear in both commands, `~/.openclaw` read-only at `/home/node/.openclaw` and `~/.openclaw/workspace` read-write at `/app/workspace`, which is how the workspace stays writable while its parent does not. The image itself is thin: the Dockerfile copies `server.js`, `index.html` and `scripts/` and nothing else, so `docs/`, `RELEASE_NOTES.md` and `install.sh` do not exist inside the container.
Usage and cost numbers arrive by two unrelated routes
The overview card can show Claude or Gemini, switched by the provider toggle, and the per-model selector names Opus, Sonnet, Pro and Flash as the choices. Underneath, two different mechanisms feed the page. Rate limit monitoring is described as tracking Claude and Gemini API usage against rolling windows, while the Claude Usage Scraper is described as fetching real usage data from the Claude Code CLI, with `tmux` listed as required for the scraper and `python3` for the usage parser. That sits awkwardly against the Minimal Dependencies entry, which claims pure Node.js with no database and no npm packages required: the parser behind one headline number is a Python program driven through tmux, not Node code. Gemini tracking arrived in v2.3.0 on February 19, 2026 and cost estimation in v2.4.0 on February 25, 2026, yet no price table, currency setting or rate source appears anywhere in the setup steps, so where the per-model dollar figures come from is unstated. Cost analysis breaks spending down by model, session and time period, and lifetime stats total tokens, messages and cost since the first session. A provider toggle plus a model selector sitting over two data sources is the part to keep in mind when a number on that card disagrees with a provider dashboard.
Two pages demand re-authentication, the file editor does not
Re-authentication is named on exactly two entries in the feature list: the System Security Dashboard, covering UFW rules, open ports, fail2ban, SSH logs and a security audit, and the Config Editor, which adds JSON validation, auto-backup and a gateway restart. The Files Manager, described as viewing and editing workspace files, skills and configs with security hardening, carries no such note. Neither does Service Control, whose quick actions restart OpenClaw, the dashboard or other services, nor Quick Actions, which offers one-click updates, cleanup and restarts. So the pages that read host security state and rewrite the agent configuration ask for credentials again, while the pages that write arbitrary workspace files and bounce services do not, as far as the feature list records. The Notification Center names three event types for its audit feed: login, config changes, and security events. Whether a file edit or a service restart lands in that feed is not stated. The Memory Viewer beside it is read-only and covers MEMORY.md, HEARTBEAT.md and daily notes, and Cron Management adds viewing, enable, disable and manual triggering of jobs. For a single trusted operator those distinctions are fine; for a shared host they are the wrong way round.
install.sh registers a unit called agent-dashboard
The systemd path is a single command:
sudo ./install.shIt creates `/etc/systemd/system/agent-dashboard.service`, writes an override to `/etc/systemd/system/agent-dashboard.service.d/override.conf`, enables and starts the unit, sets the workspace path and generates a recovery token. The unit is named `agent-dashboard`, while the repository, the built image and the container in every run example are all `openclaw-dashboard`, so the name used with systemctl is not the name used anywhere else. Logs follow the unit name rather than the project name:
journalctl -u agent-dashboard -fSystemd appears in the prerequisites as optional and for Linux only, and the install script never reaches the container because the Dockerfile copies just the server, the page and the scripts directory. That makes the two deployment paths alternatives instead of layers. The quick start path is the shortest form of the whole project:
# Clone the repository
git clone https://github.com/tugcantopaloglu/openclaw-dashboard.git
cd openclaw-dashboard

# Set your OpenClaw workspace path (optional, auto-detects if not set)
export WORKSPACE_DIR=/path/to/your/openclaw/workspace

# Start the dashboard
node server.js
Node.js v18 or higher and a running OpenClaw install are the stated prerequisites, and the first visit shows a registration screen where the username and password are created.
A MIT badge with no license file, and a homepage parked at v2.0.0
The header carries a badge linking to the MIT license text on opensource.org, yet the repository root holds `.dockerignore`, `.gitignore`, `Dockerfile`, `README.md`, `RELEASE_NOTES.md`, `docs/`, `index.html`, `install.sh`, `scripts/` and `server.js`, with no LICENSE file among them, and the license field recorded for the repository is empty. Which of the two governs is a question for the author rather than something a reader should assume. The project homepage link is behind in the same way: it points at the v2.0.0 release tag while v3.0.0, published on March 5, 2026, is the newest release, and v3.0.0 is the version that brought the theme toggle, the security dashboard, the config editor, Docker management and the notification center. The last commit on the default branch is dated March 17, 2026, twelve days after that release, and the repository carries 702 stars, 119 forks and 6 open issues. Six open issues against a dashboard that can edit workspace files and restart services is a small number to read before treating any panel as settled. Keyboard shortcuts listed as 1 to 7, Space, /, Esc and ?, a 30-day activity heatmap, 24-hour health history sparklines and an auto-refresh interval of 5 seconds describe a single screen refreshed ten times a minute, which is the load story behind every panel above.
Editorial conclusion
It fits a single operator on a box where the OpenClaw install is theirs: two files to run, no database, no npm packages, and panels for sessions, costs, cron jobs and memory files. It is a poor fit for a shared or internet reachable host, because the image enables plain HTTP at build time, the Docker page asks for the host socket, and the setup steps name no way to bind the server to a Tailscale address or to a certificate. Before trusting it with anything you care about, confirm where the recovery token from day one was stored, work out which port your own install binds, and read what the 6 open issues say about the file editor and the service restarts. The last commit on the default branch is dated March 17, 2026.
Frequently asked questions
how to install openclaw dashboard
Clone the repository and start the single server file, which needs Node.js v18 or higher and an OpenClaw install already running: git clone, cd openclaw-dashboard, then node server.js. On Linux, sudo ./install.sh registers a systemd unit named agent-dashboard and generates a recovery token instead.
what is openclaw dashboard url
http://localhost:7000 for a direct node server.js run, because DASHBOARD_PORT defaults to 7000. In the container it is port 3001: the Dockerfile sets DASHBOARD_PORT=3001, exposes 3001, and both docker run examples map 3001:3001.
how to access openclaw dashboard remotely
The setup steps only set a port. Nothing binds the server to a Tailscale address or to a certificate, and the Tailscale feature listed is for viewing status, IP and connected peers. The persistent path on Linux is the systemd unit that install.sh creates.
openclaw dashboard is not working
The setup steps include no troubleshooting section. Check which port the install actually binds first, 7000 for node server.js against 3001 in the container, then confirm the recovery token printed at first startup was saved somewhere, since password recovery depends on it.
openclaw dashboard alternative
No alternative is named in the setup steps. What the repository is: a single server.js plus index.html and a scripts directory, no database and no npm packages, needing an installed and running OpenClaw to have anything to monitor.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/tugcantopaloglu-openclaw-dashboard)Star history chart for your README
[](https://hysenlabs.com/projects/tugcantopaloglu-openclaw-dashboard)Was this useful?