Wanwu: five services, one .env template, and the password it reuses everywhere
China Unicom's Yuanjing Wanwu Agent Platform is an enterprise-grade, multi-tenant AI agent development platform. It helps users build applications such as intelligent agents, workflows, and rag, and also supports model management. The platform features a developer-friendly license, and we welcome all developers to build upon the platform.
At a glance
- What is it?
- Yuanjing Wanwu is UnicomAI's Apache-2.0 agent platform for enterprise delivery, written in Go with a web frontend. Its own configuration files say more than its feature list: one .env template feeds both the Makefile and the compose network, five services share a single example password, and the version a binary reports comes from that file rather than from a git tag.
- Who is it for?
- Wanwu is serious enterprise plumbing rather than a weekend demo, and the configuration files show exactly where an adopter inherits risk: one example password across five datastores, root database accounts, an http loopback default, and a build that expects a vendor tree and a local .env the repository does not ship.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 2 days ago.
- What is it written in?
- Mainly Go, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
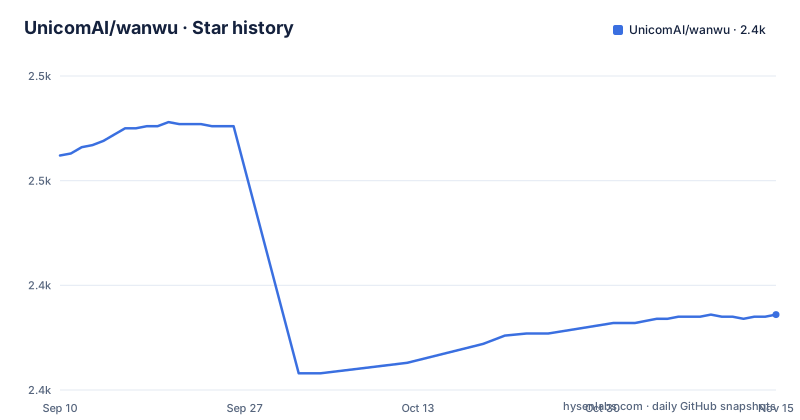
Star history
- UnicomAI/wanwu2,386 ★ · -76
| Repository | 2026-09-10 | 2026-11-15 |
|---|---|---|
| UnicomAI/wanwu | 2.5k | 2.4k |
-76 Stars in the last 66 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The Makefile includes a .env the tree never ships
The first two lines of the Makefile are includes, and the file the first one names is not in the tree:
include .env
include .env.image.${WANWU_ARCH}
What is committed is .env.example, .env.image.amd64 and .env.image.arm64, so a build needs a .env written locally before any recipe runs. Because the includes sit above the first rule, a missing file stops make before it reads a single target, and the failure comes from make itself rather than from anything the project checks. The arch include is the reason both .env.image files are in the tree: WANWU_ARCH is set to amd64 in the example, and changing it to arm64 changes which image variable file is read. Two other entry points sit beside the main one, Makefile.develop for development builds and .env.ontology.example for the ontology service, so a fresh clone presents three configuration shapes and no stated order between them.
Every build target passes -mod vendor against a tree with no vendor directory
Each service binary gets the same recipe, once per architecture:
build-bff-amd64:
	CGO_ENABLED=0 GOOS=linux GOARCH=amd64 go build -mod vendor -ldflags "$(LDFLAGS)" -o ./bin/amd64/ ./cmd/bff-service
The target list covers cmd/tidb-setup, cmd/bff-service, cmd/iam-service, cmd/model-service and cmd/mcp-service, each with an amd64 and an arm64 variant, and every one of them passes -mod vendor. The top-level tree lists no vendor directory, so those flags expect a vendored dependency tree that none of the visible targets produces. LDFLAGS stamps five values into each binary: buildTime from the shell date, buildVersion from WANWU_VERSION, gitCommitID and gitBranch from git, and builder from git config user.name, which is whatever the building machine has configured. That is the whole version story: .env.example pins WANWU_VERSION=v0.6.5, the newest tag is v0.6.5 from 2026-09-18, and the last recorded push is 2026-09-25, later than that tag. The tag list also skips a number, going from v0.6.2 on 2026-07-24 to v0.6.4 on 2026-09-04 with no v0.6.3.
One password literal serves five datastores and two superusers
In .env.example the Redis and MinIO passwords are written the same way, and so are the three database root passwords above them:
# redis
WANWU_REDIS_HOST=redis-wanwu
WANWU_REDIS_PORT=6379
WANWU_REDIS_ADDRESS=${WANWU_REDIS_HOST}:${WANWU_REDIS_PORT}
WANWU_REDIS_PASSWORD='Wanwu123456'

# minio
WANWU_MINIO_HOST=minio-wanwu
WANWU_MINIO_PORT=9000
WANWU_MINIO_ENDPOINT=${WANWU_MINIO_HOST}:${WANWU_MINIO_PORT}
WANWU_MINIO_USER=root
WANWU_MINIO_PASSWORD='Wanwu123456'
The literal is Wanwu123456 for MySQL, TiDB, OceanBase, Redis and MinIO, with root as the user in all three database profiles and for MinIO as well. Nothing marks these as placeholders. The Redis password is the one the compose file puts on the command line:
command: "redis-server --requirepass ${WANWU_REDIS_PASSWORD}"The Kafka block is the one place that differs: WANWU_KAFKA_USER=admin is set, and WANWU_KAFKA_PASSWORD follows it. Which authentication path the platform uses for its own users is a separate question, and the module list answers it indirectly, since golang-jwt/jwt/v5 and mojocn/base64Captcha are both required by go.mod next to the cmd/iam-service binary.
Every derived URL is plain http on localhost
Three variables decide how the platform addresses itself, and the example values are WANWU_EXTERNAL_IP=localhost, WANWU_EXTERNAL_PORT=8081 and WANWU_EXTERNAL_SCHEME=http:
# web base url
WANWU_WEB_BASE_URL=${WANWU_EXTERNAL_SCHEME}://${WANWU_EXTERNAL_ENDPOINT}

# api base url
WANWU_API_BASE_URL=${WANWU_EXTERNAL_SCHEME}://${WANWU_EXTERNAL_ENDPOINT}/service/api

# app open url
WANWU_APP_OPEN_BASE_URL=${WANWU_EXTERNAL_SCHEME}://${WANWU_EXTERNAL_ENDPOINT}/aibase/webChat
So the console, the service API prefix and the chat entry point are three paths on one host and one port, and the scheme variable is the only thing that decides whether any of them end up encrypted. Among the values shown, nothing introduces a certificate or a proxy in front of that port. The same file also carries identity for the compose layer, because container names and the network name are variables rather than literals: the database host is mysql-wanwu, the cache is redis-wanwu and the network is wanwu-net, so renaming a service means editing .env rather than the compose file.
Three database profiles and a dedicated TiDB setup binary
WANWU_DB_NAME carries a comment that lists the three supported engines, and the tree carries one compose file per choice:
# db: mysql | tidb | oceanbase
WANWU_DB_NAME=mysql

# mysql
WANWU_MYSQL_HOST=mysql-wanwu
WANWU_MYSQL_PORT=3306
WANWU_MYSQL_ADDRESS=${WANWU_MYSQL_HOST}:${WANWU_MYSQL_PORT}
WANWU_MYSQL_USER=root
WANWU_MYSQL_PASSWORD='Wanwu123456'
The default file is not self contained, because its first line composes another file in:
include:
  - docker-compose.ontology.yaml
Beside it sit docker-compose.tidb.yaml, docker-compose.oceanbase.yaml, docker-compose-develop.yaml and .env.ontology.example. The distributed engines get their own ports, 4000 for TiDB and 2881 for OceanBase, and OceanBase adds a tenant named wanwu, while the MySQL service starts with utf8mb4 and utf8mb4_bin so identifier case sensitivity is on. A dedicated cmd/tidb-setup binary, built for both amd64 and arm64 like the rest, is the piece that prepares the TiDB path before the main services talk to it.
Schema creation waits on a healthcheck with 99 retries
Database bootstrap is ordered by probe result rather than by container order. The MySQL service checks itself every 15 seconds with a 5 second timeout, 99 retries and a 10 second start period, and a second container waits for that probe:
  mysql-setup:
    depends_on:
      mysql:
        condition: service_healthy
    restart: on-failure
That container pipes init.sql out of configs/middleware/mysql/initdb.d into the server, so the schema comes from a mounted file on the first boot of an empty volume rather than from a migration command. The probe itself is:
    healthcheck:
      test: [ "CMD-SHELL", "mysqladmin ping -u root -p$$MYSQL_ROOT_PASSWORD | grep 'mysqld is alive'" ]
      interval: 15s
      timeout: 5s
      retries: 99
      start_period: 10s
The Redis probe is a single word, redis-cli ping, in a service whose command line sets --requirepass, so in that snippet the check carries no credential while the server demands one. Host port mappings for MySQL and Redis are commented out, which leaves both reachable only from inside wanwu-net and out of reach from the host without a change to the compose file.
The GUI Agent client is a share link, its sandbox is source
The GUI Agent is the one capability whose operator side is not built from this repository. Its section in the README points at a share on pan.baidu.com whose link carries an extraction code in the query string, and the third deployment method points at a separate site for the UniClaw client. What the tree does hold is the execution side: Dockerfile.wga-sandbox and Dockerfile.wga-sandbox-base are committed, which matches the description of isolated Docker containers per bot for UI level operation without an underlying API. So the sandbox is something you can build and audit, while the client that drives it changes outside the repository and outside the Apache-2.0 grant. The frontend shows the same split at the root, where Dockerfile.frontend.bak sits beside Dockerfile.backend, Dockerfile.callback, Dockerfile.callback-base and Dockerfile.rag, a .bak name that has no counterpart among the other build files.
Headline claims with no dataset or number behind them
Several of the README's strongest statements cannot be checked against anything in the repository. The GraphRAG bullet ends with a claim of an industry leading F1 score and names no dataset, baseline or figure. The workflow bullet claims an industry first zero code Skill invocation, and the infrastructure list claims 100 plus built in industry Skills and unified access to hundreds of proprietary and open source models. The visible English text also stops mid word inside the Core Function Modules section, on a line beginning Provides multi-infe, after two bullets of the Model Management list, so the module inventory a reader would use to test those claims is only partly there; README_CN.md and README_繁體.md sit beside it as separate files of unknown content. The badge block above the text contains two anchors with no image inside and a releases link with no badge, which is why the tag history is easier to read from the version tags than from the page.
Editorial conclusion
Wanwu is serious enterprise plumbing rather than a weekend demo, and the configuration files show exactly where an adopter inherits risk: one example password across five datastores, root database accounts, an http loopback default, and a build that expects a vendor tree and a local .env the repository does not ship. Teams who already run Go services, already keep MySQL, TiDB or OceanBase, and can own a five service compose stack will get a working agent platform out of it; anyone expecting a one command install, or evaluating the GUI Agent without arranging a separate download, should settle those questions first. Check the Apache-2.0 terms against your distribution model, replace every credential before the first boot, and treat the compose network plus the healthcheck settings as the real boundary rather than the model hub.
Frequently asked questions
What license does wanwu ship under?
Apache-2.0. A LICENSE file and a NOTICE file both sit at the top of the tree, and the project presents the license as allowing free extension, secondary development and commercial use.
What has to exist before a wanwu Makefile target will run?
A .env file written from .env.example, plus the .env.image file for the architecture you picked. The Makefile includes both above its first rule, so a missing .env stops make before any recipe is read.
Which databases can wanwu run on?
Three, chosen with WANWU_DB_NAME: mysql, tidb or oceanbase. The tree holds docker-compose.yaml for the default plus docker-compose.tidb.yaml and docker-compose.oceanbase.yaml, and cmd/tidb-setup is built for both amd64 and arm64.
How does a user get the wanwu GUI Agent client?
From a share link on pan.baidu.com that carries an extraction code in its query string, and a separate download page for UniClaw. The sandbox side is different: Dockerfile.wga-sandbox and Dockerfile.wga-sandbox-base are committed to the repository.
Which credentials ship in wanwu's example environment file?
One literal, Wanwu123456, used as the MySQL, TiDB, OceanBase, Redis and MinIO password, with root as the user in all three database profiles and for MinIO too. The Kafka block sets WANWU_KAFKA_USER=admin, and WANWU_KAFKA_PASSWORD follows it.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/unicomai-wanwu)Star history chart for your README
[](https://hysenlabs.com/projects/unicomai-wanwu)Was this useful?