Uniswap/interface: three shipped front ends, published at the end of each cycle
🦄 Open source interfaces for the Uniswap protocol
At a glance
- What is it?
- Uniswap Labs develops the web app, wallet mobile app and wallet extension in a private repository, then publishes production-ready code here at the end of a cycle. The root manifest and the file tree tell you what a contributor inherits and what stays undocumented.
- Who is it for?
- Take this repository when you plan to run or extend the shipped Uniswap front ends and can accept a Bun only toolchain pinned to Node 22.23.4. Read apps/web/README.md before trusting the root file, and check .nvmrc and .bun-version against your own runtime, because the root README names no environment variable and offers no rollback beyond the automatic release tags.
- Can I use it commercially?
- Yes, with conditions. GPL-3.0 is a copyleft licence: if you distribute software that includes it, you must release that software's source code under the same licence. Running it internally without distributing it does not trigger that obligation.
- Is it still maintained?
- Yes. The repository last received commits 3 days ago.
- What is it written in?
- Mainly TypeScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
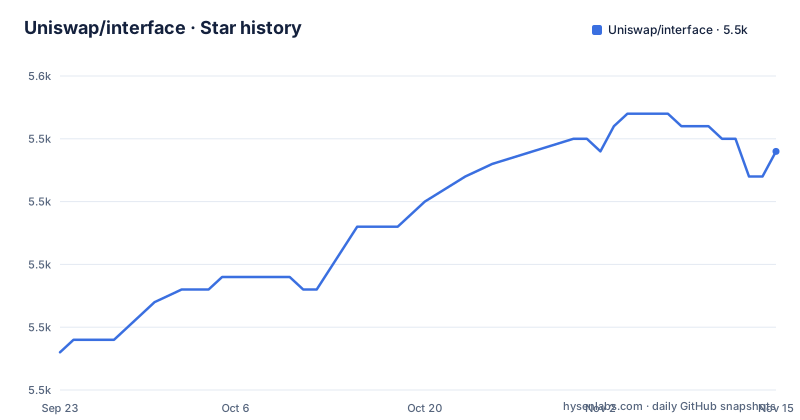
- Uniswap/interface5,544 ★ · +16
| Repository | 2026-09-23 | 2026-11-15 |
|---|---|---|
| Uniswap/interface | 5.5k | 5.5k |
16 Stars in the last 53 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The public repository receives code at the end of a cycle, not commit by commit
Uniswap Labs develops all of its front-end interfaces in a private repository. This one gets the latest production-ready code at the end of each development cycle, and releases are tagged automatically in the Releases tab. That single sentence changes how you read everything else in the tree. You are looking at a snapshot of production code, not a work log. A pull request opened against this copy lands in a repository whose day to day commits already happened somewhere you cannot see. The last push was on 2026-10-30, and the three most recent web tags are web/5.167.0 (2026-10-21), web/5.166.3 (2026-10-20) and web/5.166.2 (2026-10-20). The cadence is fast. The granularity is what surprises people. Nothing in the tree records the order the individual features landed in, so if you need to bisect a behaviour change, the tags are the only handle you get.
bun install and bun web start cover the web app and nothing else
The root README gives three lines, and there is no fourth one hiding elsewhere in the file. Clone, install with Bun, start the web target:
git clone [email protected]:Uniswap/interface.git
bun install
bun web start
That is the documented first run for the web app and nothing wider. The apps directory holds each standalone application, and the mobile and extension apps ship their own README files, so `bun web start` is not a workspace-wide command that boots all three surfaces. It targets the web app named in its name. The root file does not explain what the process does after it binds, which port it uses, or how to point it at a local contract deployment, so treat these three lines as the ceiling of what this page can teach you. Anyone building the wallet mobile app or loading the extension into a browser has to go to apps/mobile/README.md or apps/extension/README.md, and the root tree confirms those are separate applications rather than build targets of the web app. Two version pin files at the root, .nvmrc and .bun-version, decide whether the three lines work at all on your machine.
The engines block pins Node to =22.22.2 and hands npm a message instead of a version
Read package.json before installing anything. The root manifest is named universe, marked private, and typed as an ES module. Its engines block is the part worth stopping on, because three of its values are doing different jobs:
"engines": {
  "node": "=22.23.4",
  "bun": ">=1.4.4",
  "npm": "please-use-bun"
}
Node is pinned to one exact patch rather than a range, so 22.22.1 and 22.23.0 both fall outside what the manifest accepts. Bun gets a floor, which means a newer Bun is fine and an older one is not. npm gets a sentence in place of a version, which is a deliberate refusal rather than a missing field: running npm install here is not a slower route to the same result, it is the wrong tool, and the manifest says so in a place package managers read before they resolve anything. The two pin files reinforce the same intent from other directions. If your team standardises on npm through a wrapper or a corporate proxy, that wrapper has to hand control back to Bun at the root.
The root manifest carries dev tooling only, and manypkg is told to ignore the mismatch
Nothing in the root devDependencies list is a runtime library for the trading interface. It is the toolchain, and it is a long one: nx at 22.5.4, typescript at 7.0.2, vercel at 57.0.0, oxlint and oxfmt, lefthook, danger, knip, syncpack and @manypkg/cli. Application code lives under apps/, shared code under packages/, and shared infrastructure and configuration under config/, which is why the root package can stay free of product dependencies and still describe an entire exchange front end. The manypkg block then sets ignoredRules to INTERNAL_MISMATCH and ROOT_HAS_DEV_DEPENDENCIES, which is the repository instructing its version consistency checker to stop complaining about precisely this arrangement. Read that as a deliberate decision rather than an oversight. Version drift between the shared packages is tolerated on purpose, and the two ignored rule names are the paper trail explaining who decided it.
lefthook.yml, commitlint.config.js and dangerfile.ts decide whether your commit survives
Before the first commit, three files set the terms. lefthook.yml wires the git hooks and .husky/ sits beside it, so a rejected commit message stops you locally rather than in review. commitlint.config.js with @commitlint/config-conventional 17.4.4 decides the shape of the message text itself. dangerfile.ts runs its own checks on the pull request, and CODEOWNERS names who has to look at it. Linting here is not only formatting: oxlint.config.ts and .oxfmtrc.json split rules from formatting, the devDependency list carries eslint-plugin-security and eslint-plugin-no-unsanitized alongside oxlint-plugin-eslint, and knip.json is there to flag unused exports and dead files. On top of that sits nx.json and the .nx/ cache directory, so task graphs and remote caching are part of the normal path. A change that touches one screen can fail on a commit format, an unused import, a security lint rule or a missing owner, and the order those four checks run in is not written down anywhere in the root file.
No environment variable, no port and no rollback appear anywhere in the root README
The root README names no environment variable, no port and no deployment target. The devDependency list includes dotenv-cli 7.1.0, so environment file loading is expected somewhere in the toolchain, and the tree carries firebase.json, .firebaserc, firestore.rules and firestore.indexes.json, which places Firestore in the picture. What none of that resolves is which keys you need, where they come from, or whether a local run works without them. The i18n side has the same shape: i18n.config.ts and i18next-parser.config.js sit at the root with an .i18n/ directory, and i18next plus i18next-parser are devDependencies, but no locale list or extraction command is given at the root. Rollback is the other silence. Releases are tagged automatically, the public repository is a publish target, and nothing documents a revert procedure, so moving back to earlier behaviour means finding an earlier tag and rebuilding from it yourself. Treat the per-application READMEs and CONTRIBUTING.md as the real documentation. The root file is an index, a directory table and a contact list.
It is a shipped product front end, not a library you can add to a project
The GPL-3.0 license and the private flag together settle what this repository is for. The root package.json is marked private and carries a version of 0.0.0, so adding this to your own project as a dependency is not a path that exists. The alternative shape is to call the protocol from your own front end and keep a thin client, skipping this codebase and its three products entirely. The difference is scope, not quality. Working inside this tree gives you the real interface logic, the translation pipeline, the release plumbing and the deployment configuration, and it charges you an Nx workspace with a hard Node pin and a private development loop you do not control. The clearest measure of what a fork inherits is the configuration surface: firebase.json and the Firestore rules, vercel.json, i18n.config.ts, oxlint.config.ts, knip.json and the commit and danger rules. For a team shipping a full exchange product, that surface is the point. For a team that needs one swap widget, this is the wrong repository, and the 0.0.0 version says so before you read a single line of the README.
Editorial conclusion
Take this repository when you plan to run or extend the shipped Uniswap front ends and can accept a Bun only toolchain pinned to Node 22.23.4. Read apps/web/README.md before trusting the root file, and check .nvmrc and .bun-version against your own runtime, because the root README names no environment variable and offers no rollback beyond the automatic release tags.
Frequently asked questions
What is Uniswap/interface, and is it the Uniswap protocol itself?
It is the front end only: the web app, the wallet mobile app and the wallet extension, all in TypeScript. The protocol contracts and the V1 through V4 whitepapers live elsewhere, and the project describes itself as open source interfaces for the Uniswap protocol.
Can I install Uniswap/interface with npm?
No. The root package.json sets engines.npm to please-use-bun and requires Bun 1.4.4 or newer, and the documented install line is bun install after cloning the repository.
Which Node and Bun versions does Uniswap/interface require?
The root manifest pins Node to =22.23.4 and Bun to >=1.4.4. The .nvmrc and .bun-version files at the root carry the same intent for version managers that read them directly.
Does Uniswap/interface include a backend or a self hosted indexer?
The root README does not say. The tree carries firebase.json, .firebaserc, firestore.rules and firestore.indexes.json, but the README names no environment variable, no indexer and no contract deployment procedure.
How often does Uniswap/interface ship releases?
Tags are cut automatically, and the last push was on 2026-10-30. The three most recent web tags are web/5.167.0 (2026-10-21), web/5.166.3 and web/5.166.2 (both 2026-10-20).
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/uniswap-interface)Star history chart for your README
[](https://hysenlabs.com/projects/uniswap-interface)Was this useful?