docker_practice: 21 chapters, a CC BY-NC-SA licence, and a PDF that moves
Learn and understand Docker and container technologies, with real DevOps practice.
At a glance
- What is it?
- docker_practice is a Chinese-language book on Docker and container practice, published on GitBook with a downloadable PDF and built by its own tooling. The parts that affect whether you can use it are the non-commercial share-alike licence, a preview PDF that is overwritten on every mainline update, and a manifest version that has drifted behind the release tags.
- Who is it for?
- docker_practice suits a Chinese-reading developer or operator who wants a structured path through Docker with the practice cases included, and whose use is non-commercial. It is a poor fit for paid corporate training, because CC BY-NC-SA 4.0 requires non-commercial use with attribution and share-alike, and for anyone needing an English edition or a version-stable PDF, since the preview file is overwritten on every mainline push.
- Can I use it commercially?
- Not without permission. GitHub finds no licence file in the repository, and without a licence all rights are reserved by default: you may read the code but not reuse it. Check the README, or ask the authors, before using it.
- Is it still maintained?
- Yes. The repository last received commits 4 days ago.
- What is it written in?
- Mainly Go, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
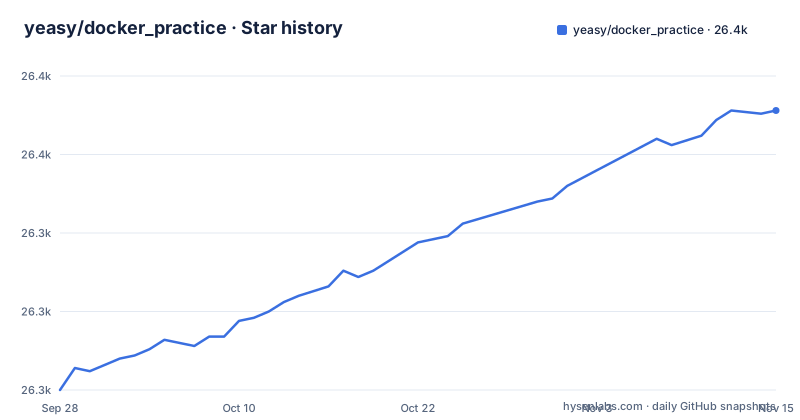
- yeasy/docker_practice26,364 ★ · +89
| Repository | 2026-09-28 | 2026-11-15 |
|---|---|---|
| yeasy/docker_practice | 26.3k | 26.4k |
89 Stars in the last 48 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The book builds itself with Docker, and the two images differ
A book about containers is assembled by containers, which is the most fitting thing in the repository. The compose file defines three services. The first, `mdpress-build`, uses the image `yeasy/docker_practice:latest`, mounts the working directory at `/srv/gitbook-src` and runs a build command. The second reuses that definition through a YAML merge key:
  mdpress-server:
    << : *mdpress-build
It adds a published port and a different command. The third, `mdpress-offline`, does not use the anchor at all. It pulls `dockerpracticesig/docker_practice:mdpress` from a different organisation, maps the container's port 80 to the host's 4000 rather than 4000 to 4000, and carries a comment that this image is built by a GitHub Action.
So there are two different images, from two different namespaces, with two different port conventions, and the offline one is produced by automation rather than by the same compose definition. A commented `docker run` line in the file shows a third naming variant. Nothing is wrong, but if you are reproducing the site locally, the difference between the build path and the offline path is a small thing to trip over.
Anchors and merge keys are worth recognising in general, since this file is a compact example of the pattern.
The preview PDF is overwritten and is not a release
There are two ways to get the book as a file, and they are not equally trustworthy. The supported route is the PDF on the GitHub Releases page, which corresponds to a tagged version. The second is a file under a release named for a preview PDF, and the README attaches a warning to it directly: it is overwritten as the main line updates and does not represent an official released version.
That distinction matters more here than it would for a piece of software. A software user who gets a slightly newer build is barely affected, and a good bug report names the tag anyway. A course, a reading group or a study plan built on a PDF is different, because readers will refer to chapter and section numbers and the document they are quoting may have moved under them.
The release list shows how the two coexist. There is a preview PDF tag dated 2026-03-29, alongside versioned tags v1.11.0 from 2026-07-04 and v1.10.0 from 2026-05-31. The preview being older than the latest version is a reminder that it is a moving target rather than a lag.
If you need a stable copy to distribute, take a tagged release and record the tag alongside the file.
CC BY-NC-SA 4.0 rules out putting it in a paid course
The licence is stated in the README and repeated in the manifest, which carries `CC-BY-NC-SA-4.0`. The README spells out the three obligations in plain terms: you may share and adapt freely, provided you give attribution, use it non-commercially, and share derivative works the same way.
The non-commercial term is the one with teeth. This is a training resource, and training is exactly the use case a company is most likely to have in mind, so the restriction binds before anything else. Adaptation is permitted, which means you can translate it or cut it up, but only if the result stays non-commercial and is licensed the same way. That is different from the permissive terms most technical books carry, and it is worth settling before anyone invests in adapting the material.
Two details sit alongside it. Repository metadata reports no recognised licence identifier even though the project states one, so automated tooling will not tell you the terms, and the manifest's author field is an empty string, so an automated attribution string will come out blank. If you are citing the work, take the author and terms from the README rather than from the package metadata.
This is a reading of the stated terms, not advice on how they apply to your situation.
The manifest says 1.9.2 and the tags say v1.11.0
The root `package.json` identifies the project as `docker_practice` at version `1.9.2`, marked private. The release tags tell a later story, with v1.10.0 and then v1.11.0. The two do not agree, and the reason is visible in the file itself: the package is private and its only dev dependency is a Mermaid renderer, so the version field is not tracking the book's edition.
Read it that way and there is no bug. Read it as an edition number and you will cite the wrong thing. Anyone pinning tooling against this repository, or writing a script that reports which version of the book it has, needs the git tag rather than the manifest.
The scripts in the same file show what the manifest is actually for, and they are all publication tasks. Building the site removes the output directory and runs a site-format build, serving runs the development server, and the PDF script is the interesting one because it chains four steps: clear a temporary directory, run a Python script to prepare the PDF sources, change into that directory, and build the PDF with an output path resolved from an environment variable so it lands back in the project root rather than in the temporary tree.
So the build is a Node and Python pipeline wearing a book-shaped package file.
The test script chains Node, two Python runs and a validation pass
Validation for a book repository is unusual enough to be worth reading:
"test": "node scripts/check_metadata.js && python3 -m unittest tools.test_prepare_pdf_sources && python3 -m unittest discover -s tests -p 'test_*.py' && python3 tools/test_examples.py",Four stages in sequence, and the first three must pass before the fourth runs. A Node script checks metadata, then a targeted Python unit test covers the PDF source preparation, then the general Python suite is discovered under `tests/`, and finally a script exercises the examples.
That tells you what the maintainers consider breakable. The PDF pipeline is a build artefact that can silently change shape, so it has its own test. The examples are run rather than merely listed, which is the difference between a snippet that was once correct and one that still is. Two more checks live at the repository root as Python scripts, one for emphasis formatting and one for project rules, so style and convention are enforced by tooling rather than left to review.
A note on the repository metadata: it lists Go as the primary language, while the tooling visible here is Node and Python, with a `.devcontainer/` directory and a `tools/` directory holding the Python. If you are looking for Go code to read, the book chapters are Markdown and the build scripts are the code.
One book, four reading paths, and one command in the quickstart
The structure is laid out in four bands of chapters, and the intended reader decides which parts matter. Chapters 1 to 6 cover the basics, which the README names as the core concepts of images, containers and repositories plus the core operations. Chapters 7 to 11 go further, with Dockerfile directives in detail, data and network management, Buildx and Compose. Chapters 12 to 17 turn to internals, covering implementation, container orchestration with Kubernetes and etcd, and adjacent ecosystem projects including Fedora CoreOS and Podman. Chapters 18 to 21 are practical, on container security, monitoring and log aggregation with Prometheus and ELK, and case studies in operating systems and CI/CD automation.
On top of that sit four role-based paths rather than a single linear one. An operations beginner reads 1 to 6. A developer reads 1 to 8 then 11. A DevOps engineer reads 1 to 11, then 13 and 14, then 18 to 21. An architect reads 1 to 6, then 12 to 17, then 18 and 19.
The five-minute quickstart is five pointers into that structure, and only one of the five steps contains a command:
docker run -it ubuntu bashEverything else in it is a chapter reference, including building an image and writing a Dockerfile. That is the honest shape of a 21-chapter book: it is a curriculum, and the quickstart is a reading plan.
Half the later material is about things that are not Docker
The band boundaries are worth noticing when you are deciding whether this book is the right one. Dockerfile, images, containers, registries, networking and Compose occupy the first eleven chapters. From chapter 12 the subject becomes the machinery around containers: how they are implemented, how they are orchestrated with Kubernetes and etcd, how they meet cloud computing, and how they relate to CoreOS and Podman. The last band adds security, observability and pipeline automation.
That is a reasonable progression for someone who has to run containers in production, and a poor fit for someone whose problem is Docker itself. If you want to understand the container and the image, chapters 1 to 6 cover it. If you want to deploy with Kubernetes, this book spends five chapters getting there and the rest on operating the result.
The wider set the same author maintains points the same way. Alongside this book there are titles on deployment engineering covering GitOps, infrastructure as code, supply chain, observability and SLOs, one on containerised deployment and isolation for agent infrastructure, one on the overlap between container security and AI system security, and one on containerised blockchain nodes. Read together they describe a practice in which the container is the substrate and the work is everything layered on it.
For a reader who only wants Docker, expect roughly half of the later chapters to be background.
Editorial conclusion
docker_practice suits a Chinese-reading developer or operator who wants a structured path through Docker with the practice cases included, and whose use is non-commercial. It is a poor fit for paid corporate training, because CC BY-NC-SA 4.0 requires non-commercial use with attribution and share-alike, and for anyone needing an English edition or a version-stable PDF, since the preview file is overwritten on every mainline push. Before adopting it, check three things: whether the chapter band you need matches your role's reading path, which release you are citing, because the manifest version says 1.9.2 while the tags are at v1.11.0, and whether the non-commercial term blocks your intended use.
Frequently asked questions
Is docker_practice free to use for company training?
The book is licensed CC BY-NC-SA 4.0, which the README summarises as free to share and adapt provided you give attribution, use it non-commercially, and share derivative works the same way. It is readable free online on GitBook, and the PDF edition is available from the GitHub Releases page. The non-commercial term is the one to check against your intended use.
How do I read docker_practice offline?
Download the PDF from the GitHub Releases page, which corresponds to a tagged version such as v1.11.0. A preview PDF is also published under a release named preview-pdf, but the README states that file is overwritten as the main line updates and does not represent an official released version. For local HTML, install mdPress with `brew tap yeasy/tap && brew install mdpress` and run `mdpress serve`.
How many chapters does docker_practice have and where should I start?
There are 21 chapters in four bands: 1 to 6 for basics, 7 to 11 for advanced application including Dockerfile, Buildx and Compose, 12 to 17 for internals, and 18 to 21 for practical work on security, Prometheus, ELK and CI/CD. The README gives role-based paths, from operations beginners reading 1 to 6, through to architects reading 1 to 6, then 12 to 17, then 18 and 19.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/yeasy-docker-practice)Star history chart for your README
[](https://hysenlabs.com/projects/yeasy-docker-practice)Was this useful?