google-cloud-python: a monorepo that ships a package per service
Google Cloud Client Libraries for Python
At a glance
- What is it?
- Google's Python clients for Cloud Platform live in one repository and publish as hundreds of independent PyPI packages. The README's real content is a stability taxonomy, and the generated table it embeds is more useful than it looks.
- Who is it for?
- The thing to take from this repository is that there is no single google-cloud-python package to install and no single stability guarantee to rely on. You choose a service, check the classifier its package carries on PyPI, and judge that service's API surface accordingly, while a beta-marked sub-module inside a stable package is a separate promise again.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly Python, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 21, 2026, and from our analysis. They are not legal advice.
Star history
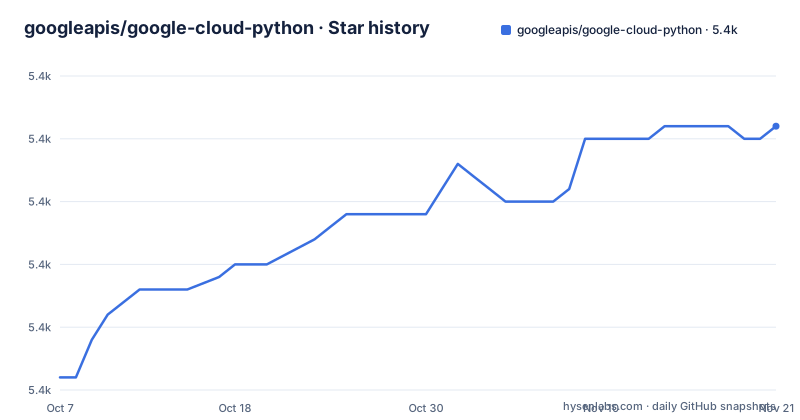
- googleapis/google-cloud-python5,421 ★ · +20
| Repository | 2026-10-07 | 2026-11-21 |
|---|---|---|
| googleapis/google-cloud-python | 5.4k | 5.4k |
20 Stars in the last 45 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The README's real subject is a stability taxonomy
A reader expecting a list of libraries gets one, and it is enormous and machine generated. But the section that actually explains the project is the one near the top, titled Stability levels, and it works through three states with more care than most library documentation does.
Stable, or general availability, means the client for a particular service has reached GA and that the code surface will not change in backwards-incompatible ways unless absolutely necessary, for instance because of a critical security issue, or with an extensive deprecation period. Issues and requests against stable libraries are addressed with the highest priority. The PyPI marker for this is the development status classifier for production and stable.
Preview covers two further states. Beta indicates the library is mostly stable, with issues addressed at a higher priority. Alpha indicates a work in progress that is more likely to receive backwards-incompatible updates.
What makes this genuinely useful rather than decorative is the mechanism. Each level maps to a specific PyPI development status classifier, so the promise is checkable without trusting the project's own adjectives. You can look at any package page and know what you are holding. Most ecosystems describe stability in prose and leave the reader to guess. This one hands you a field on an index page.
There is a second-order rule that catches people out, and it appears in a note attached to the stable tier. Sub-components of stable libraries that are explicitly marked as beta in the import path, with something like a v1beta2 suffix given as the example, should be considered to be preview. The package can be GA while the specific module you import is not.
The library table is generated and says so
The list of libraries in the README comes with a comment above it stating that the table is generated and pointing at a script called synth.py for details. It is rendered as an RST list-table with a header row of client, release level, version, API issues, file an API issue, and client library issues.
Two of those columns are worth more attention than they first appear to deserve. API issues, where filled in, points at the Google issue tracker, to a saved search or component query for that API, and the adjacent file-an-issue column links straight to a new issue form with the component already selected. That is a deliberate separation of concerns: a request for a new method is a request against the API, while a bug in the generated Python wrapper is a bug against the repository.
In practice that means when something does not work you have to decide which bucket it belongs in, and the generated table makes that decision easy. If the underlying method is missing from the API, it is an API issue. If the method exists and the wrapper mangles it, it belongs in the repository's issue tracker.
The table also confirms the sprawl. Reading through it, entries range from a Python wrapper of the C CRC32C library and a unified Python API in BigQuery, through AI Platform, App Engine Admin, Artifact Registry and Asset Inventory, to Auth OAuthlib and beyond. A python wrapper of the C library is included in a repository of Cloud clients, which tells you the boundary is packaging rather than theme. Each row links to either a package directory inside this repository or to a separate repository.
A monorepo publishing hundreds of independent distributions
The tree explains how hundreds of packages ship from one repository. `packages/` holds clients in directories named after the distribution, such as `packages/google-cloud-asset`, and a separate `preview-packages/` directory sits beside it.
Several of those directories link out to their own repositories rather than living here, and that pattern is worth noting. BigQuery's BigFrames and AI Platform are referenced at `github.com/google/bigframes` and `github.com/googleapis/python-aiplatform`, while Asset Inventory and Apigee Connect are referenced at paths inside this tree. Both arrangements appear in the same generated table, so the convention is not uniform and you should follow the link rather than assume.
The tooling directories tell you what a large release operation requires. There are three release-please configurations with matching manifests, named bulk, individual and preview. `renovate.json` keeps dependency updates moving, `.pre-commit-config.yaml` enforces local checks before anything is committed, `mypy.ini` covers static typing across the codebase, and `librarian.yaml` plus a `.librarian/` directoryare also present.
The `.gemini/`, `.kokoro/` and `AGENT_WORKFLOW.md` entries point to AI-assisted contribution tooling and to a specific CI system, and `.pinned-metadata.yaml` plus `.trampolinerc` suggest dependency and image pinning. All of it is a fair proxy for how much machinery stands behind a simple `pip install`.
Releases come in coordinated waves with identical commit messages
Releases are tagged per package. The three most recent are `google-auth` v2.62.1 on 2026-11-03, `google-cloud-compute` v1.56.0-preview.2 on 2026-10-29 and `google-cloud-bigquery` v3.47.0 on 2026-10-29.
The version numbers themselves tell you where each client sits. BigQuery is at 3.47.0, while the Compute release carries a preview tag. Combined with the stability tiers, that gives you a reasonably quick read on which packages are safe to let float to a new version automatically and which need a constraints file in your project.
The repository itself is not archived and was pushed to on 2026-11-02, with 5,417 stars and 1,821 forks. The open issue count of 646 is high in absolute terms and unremarkable for a repository of this size and this many separate issue trackers.
What to install, and where the boundaries with other libraries are
The README is pointed about scope. It describes itself as Python idiomatic clients for Google Cloud Platform services, and the second half of the stability section contains the redirect that matters most for anyone starting: if you need support for other Google APIs, the README points to the Google APIs Python Client library, a separate project for everything that is not Cloud.
That boundary is the one to internalise. If you are writing an application that talks to both Storage and, say, the Google Calendar API, you will be installing two different libraries with two different philosophies.
The reference documentation lives at docs.cloud.google.com/python/docs/reference rather than in the repository. `CONTRIBUTING.rst`, `CODE_OF_CONDUCT.md`, `SECURITY.md` and `SUPPORT.md` are all present at the root, which is more governance surface than most monorepos of this size bother with and it is worth reading `SUPPORT.md` before assuming an issue tracker is the right channel.
There is one more detail in the generated table that explains a dependency people often trip over. Both an API client core library under `google-api-core` and one under `google-cloud-core` appear as stable entries.
Editorial conclusion
The thing to take from this repository is that there is no single google-cloud-python package to install and no single stability guarantee to rely on. You choose a service, check the classifier its package carries on PyPI, and judge that service's API surface accordingly, while a beta-marked sub-module inside a stable package is a separate promise again. Everything else here is machinery in service of that: the generated table so you can look up a service without reading the tree, release automation so hundreds of packages can move together, and Renovate and pre-commit keeping the inputs current. Start from the stability section rather than the library table, because the taxonomy, not the package list, is what will save you from an upgrade surprise.
Frequently asked questions
How do I tell whether a google-cloud-python package is stable?
Each package carries a PyPI development status classifier that maps to one of the README's tiers: production and stable for GA, beta for a mostly stable preview, and alpha for a work in progress likely to get backwards-incompatible updates. You can check the classifier on the package's PyPI page without trusting the project's own description.
Can a stable package still contain unstable modules?
Yes. The README states that sub-components of stable libraries explicitly marked as beta in the import path, with a versioned suffix such as v1beta2 given as the example, should be considered preview. A package at general availability can therefore contain modules that are not.
Which package should I install for a non-Cloud Google API?
This repository is scoped to Cloud Platform services. For other Google APIs the README directs you to the separate Google APIs Python Client library.
Why do package changelogs show identical regenerate entries?
Because releases happen in coordinated waves. A version bump with no visible functional change usually reflects an upstream API definition change rather than a change to the Python wrapper itself.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/googleapis-google-cloud-python)Star history chart for your README
[](https://hysenlabs.com/projects/googleapis-google-cloud-python)Was this useful?