clawpanel: the container image is named openclaw, and macOS is told to pick a build by year
OpenClaw & Hermes Agent multi-engine AI management panel, with a built-in AI assistant (tool calling, image recognition, multimodal), one-click install, a Tauri v2 cross-platform desktop app, and 11 languages.
At a glance
- What is it?
- A Tauri v2 desktop panel that installs, diagnoses and supervises three AI agent engines, with a web-only mode that is what makes the ARM64 and embedded-board story work at all. The front page mixes two third-party commercial promotions with its download links, splits macOS builds on a year rather than on hardware, deploys its container on the host network by default, and its headless install command stops partway through a URL.
- Who is it for?
- clawpanel fits someone running agent engines on a single machine or a small board who wants a graphical way to install, diagnose and repair configuration rather than a command line, and the web mode is the genuinely portable half of the design. Four things to settle first.
- Can I use it commercially?
- Check first. The repository uses a licence we do not classify automatically, so read its LICENSE file before any commercial use.
- Is it still maintained?
- Yes. The repository last received commits 26 days ago.
- What is it written in?
- Mainly JavaScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
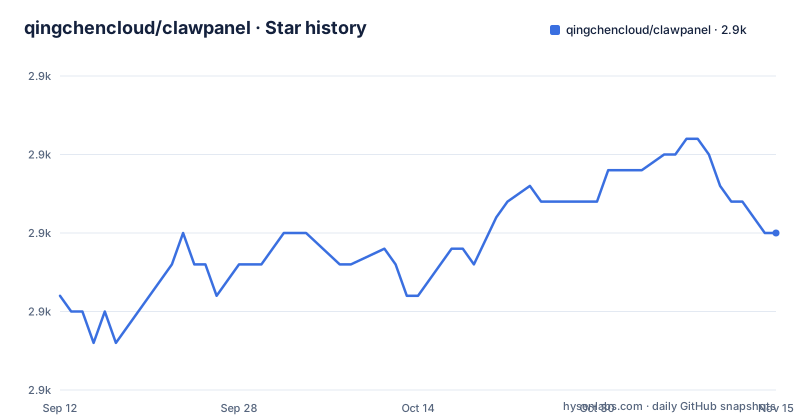
Star history
- qingchencloud/clawpanel2,935 ★ · +4
| Repository | 2026-09-12 | 2026-11-15 |
|---|---|---|
| qingchencloud/clawpanel | 2.9k | 2.9k |
4 Stars in the last 64 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The container image is named after one of the engines it manages
The download routes are four: an official download centre that detects your system, GitHub releases kept as a backup, and a mirror hosted on a domestic code-hosting site.
The desktop tables give seven package formats across three platforms. Two macOS disk images, one for each architecture. Two Windows installers, an executable installer recommended for ordinary use and an MSI for enterprise and silent deployment. Three Linux packages, a self-contained image needing a permission change, a Debian package and an RPM.
The container route is where the naming stops making sense:
docker run ghcr.io/qingchencloud/openclaw:latestThat image is ClawPanel. It is published under the name of OpenClaw, which is one of the three agent engines the panel manages, while the compose file in this same repository builds and runs a service named after the panel. Someone pulling that image by name will reasonably believe they are installing something else.
The architecture story is coherent once you see the split. Every Windows and Linux desktop package is x86-64 only, and ARM64 support lives entirely in the web mode and the container. Both macOS architectures do have native builds. So the boards are supported by not being a desktop application, which the page states clearly enough, if indirectly.
macOS gets a year-based guess and an unsigned-app warning
The macOS table splits on a year rather than on hardware. Apple Silicon covers machines from late 2020 onward, and Intel covers 2020 and earlier.
That proxy fails exactly where a proxy would. An Intel Mac bought in 2021 falls on the wrong side of nothing, because the table does not distinguish it from an Intel Mac from 2019, and a reader who guesses wrong downloads the wrong disk image. The page then tells them how to check, by opening About This Mac and reading the chip field, which concedes that the table is a guess.
Both disk images hold the same application, so the cost of a wrong guess is a wasted download rather than a broken install. It is a small problem with an easy manual answer.
The larger item on that platform is the signature, and the page is direct about it. The application is unsigned, so macOS blocks it on first open and reports it as damaged or as unverified. Two remedies are offered: a terminal command that strips the quarantine attribute from the installed application bundle, or the override in System Settings under Privacy and Security.
Both are ordinary for an unsigned build distributed outside a store. Both also disable the check that exists specifically to interrupt an unverified binary on first launch, which is exactly the situation here. Worth doing consciously rather than reflexively: you are removing a safeguard that was working.
The compose file puts the panel on the host network
The deployment default is host networking, and the file explains itself at length:
network_mode: hostThe stated reasons are that the container can then reach services running on the host, naming the agent gateway specifically; that it avoids the complexity of port mapping; and that it performs better because there is no extra network layer. The comment closes by noting that with host mode the ports configuration is invalid.
The port mapping is present in the file but commented out, labelled as applying only in the default network mode, with an instruction to uncomment it if you would rather have a bridge. So the choice is made deliberately and the alternative is one edit away.
The consequence is worth stating without softening. The panel's web interface, on the port the image sets, listens on the host's interfaces rather than being confined by a published mapping. That is exactly what makes the gateway reachable, and it is also what means anything able to reach the host on that port can reach the panel.
Compare it with the third engine's own design, which keeps its listener on the loopback address and reaches the full interface through short-lived tokens and a sandbox proxy, specifically so that no additional public port has to be opened. Two halves of one application make opposite choices about exposure, and only one of them explains the trade in terms of the other.
A native toolchain is installed for a build that compiles nothing
The builder stage of the container image installs git, python3, make and a C++ compiler before running the frontend build.
That build is one bundler invocation. The manifest declares four runtime dependencies, all prebuilt packages, none with a native component, and the desktop shell's own compiled side is not built here at all. So nothing in the build step requires a compiler.
The likely reason is defensive. An install step will compile any dependency that ships an install script, so installing a toolchain makes that step incapable of failing on a missing compiler. It is a reasonable precaution and a large one, since the production stage is a second copy of the same base image without any of it.
Two more lines in the same file deserve attention.
COPY --from=builder --chown=node:node /build/node_modules ./node_moduleThe destination is spelled in the singular, which is not the directory name Node resolves dependencies from. Either the runtime references that path explicitly, or the production image cannot resolve its dependencies at all.
And the package registry mirror is passed as a build argument by the compose file, while the Dockerfile hardcodes the same mirror address in its install line rather than reading the argument. Changing the argument has no effect, and the address is a regional third-party mirror rather than the default registry.
Ownership and home directory disagree in the production image
The production stage copies the build output as an unprivileged account that the base Node image already provides, and the comment beside it explains the reasoning: reusing the built-in user avoids a group id conflict on newer versions of the base distribution.
Two environment settings then point somewhere else. The home directory is set to the privileged user's home, and the timezone is fixed to a specific city rather than left to the deployment.
Those choices contradict each other. Files in the image are owned by the unprivileged account while the home directory points at the privileged one, so anything the application writes to its home, which for a panel that stores agent configuration is a substantial amount, is aimed at a path the process does not own. Depending on how the entrypoint is written that is either a permissions error at startup or a silent fallback.
The fixed timezone is a smaller matter but not a neutral one for this product. A panel that supervises background agents and can install a managed runtime is scheduling work, and a container that always reports the same zone will disagree with its host and with any user in another one.
The runtime stage also installs git and curl, which suggests the panel fetches something while running. That fits the rest of the page: a version policy file at the repository root, and a managed runtime described as installing and pinning a fixed accepted version of an engine.
Two version scripts run the identical command
The manifest's script list has ten entries, and two of them are the same operation under two names. One, for synchronising a version, and one, for setting it, both invoke the same file with no arguments.
So there is no difference between them, and neither accepts an option. Given that the repository root holds a version policy data file governing the managed engine, a reader would reasonably expect the setting script to be the one that writes into it. As written, the two names promise a distinction the scripts do not deliver.
The rest of the list is more revealing about what the product is. There is a bundler dev server, a bundler build, a preview, a passthrough to the desktop framework's own command, a script that regenerates the application icons from a logo image in the documentation directory, and a script that builds the locale files producing the eleven translations.
Then two that matter more than they look:
"serve": "node scripts/serve.js",
"web:bundle": "node scripts/prepare-web-bundle.mjs"
Those two are how the project escapes its own shell. The web mode is a plain Node server and a bundling step, with no desktop runtime and no graphical environment, which is the whole reason the ARM64 board and embedded-device support is possible. Everything the page claims about small computers rests on those two entries rather than on the desktop build.
Eleven translations, a duplicated badge, and a truncated install command
The front page offers eleven language versions, and the repository root carries eleven matching readme files. The count holds.
Chinese is the default and the only one marked as such in the switcher. The description, the package manifest, the compose file and the Dockerfile comments are all written in Chinese, so the English page is a translation rather than the source. That is a legitimate choice for where the project comes from, and it does mean the English text is the one most likely to lag.
Three small defects sit in the same file. Two badges at the top point at the same releases address. One community chat link appears twice inside a single row of links, once at the start of a group and again at the end of the next. And the third engine's primary link resolves not to the engine itself but to a community translation repository maintained by an individual account.
The significant one is at the bottom. The section for deploying the web version on a headless Linux server, which is the route the board and embedded story depends on, opens with a fetch-and-pipe command whose address stops partway through, at a raw content host and the organisation name, with no repository path and no script name.
So the one install command a headless user most needs is the one that cannot be copied. The container route beside it is complete, and the build scripts in the repository root are the other way in.
One more note for anyone reading the front page as a product page: alongside the official links sit two third-party commercial promotions, one a paid model relay advertising a deposit-to-credit conversion rate and an OpenAI-compatible endpoint to paste into the panel's settings, the other a free quota platform. The page is honest that no keys for the free platform are bundled and that you must register and paste one yourself, which is more disclosure than most vendor sections include.
Editorial conclusion
clawpanel fits someone running agent engines on a single machine or a small board who wants a graphical way to install, diagnose and repair configuration rather than a command line, and the web mode is the genuinely portable half of the design. Four things to settle first. Read what the container does on the host network before deploying it anywhere reachable, because that default exists so the panel can reach the agent gateway and it also removes the port boundary. Expect the macOS build to be unsigned and decide consciously whether to work around Gatekeeper. Ignore the sponsored provider section and register your own key, since the page itself says no keys are bundled. And prefer the source build or the Docker route over the web install line, which is incomplete.
Frequently asked questions
Which engines does ClawPanel manage?
Three: OpenClaw, Hermes Agent and DeepSeek Harness. The DeepSeek Harness section describes a managed runtime that installs a fixed accepted version without touching the global npm environment, a separate web workbench, model settings synchronised from the panel with read-back confirmation, and a listener kept on loopback reached through short-lived tokens.
How is ClawPanel installed on Linux?
Three desktop packages, all x86-64: a self-contained AppImage that needs a permission change, a DEB for Debian and Ubuntu installed with dpkg, and an RPM for Fedora and RHEL. There is also a web version for headless servers, and a container image, which is the route that covers ARM64 boards.
Why does macOS report ClawPanel as damaged on first launch?
Because the application is unsigned, so macOS blocks it. The page offers two remedies: removing the quarantine attribute from the installed application bundle in a terminal, or using the Privacy and Security override in System Settings to open it anyway.
What licence is ClawPanel released under?
The package manifest declares AGPL-3.0 and a LICENSE file is present at the repository root, while the repository metadata itself records no recognised licence value. The manifest and the licence file are the two places to check, and they disagree with the metadata.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/qingchencloud-clawpanel)Star history chart for your README
[](https://hysenlabs.com/projects/qingchencloud-clawpanel)Was this useful?