claude_codex_bridge documents its own race conditions, and clears your draft after 180 seconds
Visible multi-agent CLI workspace for mixing Codex, Claude, Gemini, Kimi, Qwen, Cursor, Copilot, Pi, OpenCode, and other AI coding agents
At a glance
- What is it?
- A terminal multiplexer and collaboration layer for driving several CLI coding agents at once, with a background daemon, a mobile controller, and a self-updater that refuses to modify an npm install. The unusual thing about this project is that its release notes are in the readme and they are candid about failure: a non-atomic input sequence, a draft-clearing timer, unsigned Windows binaries, and which providers have been tested versus not. Three packaging facts are worth knowing first: the manifest says AGPL-3.0-only while the recorded licence is empty, the npm tarball excludes Windows and ships no source, and installing puts four commands on your path.
- Who is it for?
- This suits someone already running two or more CLI coding agents who wants them in visible panes they can take over, and the honesty in the release notes is a genuine reason to trust the rest of it. Five things to establish first.
- Can I use it commercially?
- Check first. The repository uses a licence we do not classify automatically, so read its LICENSE file before any commercial use.
- Is it still maintained?
- Yes. The repository last received commits 4 days ago.
- What is it written in?
- Mainly Python, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
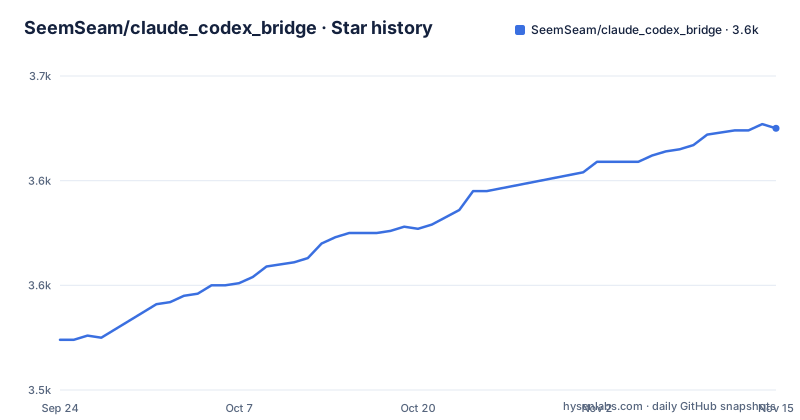
- SeemSeam/claude_codex_bridge3,625 ★ · +101
| Repository | 2026-09-24 | 2026-11-15 |
|---|---|---|
| SeemSeam/claude_codex_bridge | 3.5k | 3.6k |
101 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The release notes are in the readme, and they admit the failure modes
The most valuable thing in this repository is that its readme is also its changelog, and the entries describe what does not work.
The 8.7.0 entry introduces the human and agent queue modes and closes by calling it a first version for testing. It says the deadline clearing for two named providers uses a keyboard interrupt and that a simultaneous user action can still cause an interruption. And it says the final screen-check, paste and enter sequence is not atomic against typing at that exact instant.
That is a specific, technical admission of a race condition in the project's most important interaction. It is also, notably, not hidden behind a link.
The later entries keep going. 8.7.3 records that experimental native plugins for one provider remain disabled, and that the onboarding no longer recommends six preview roles while explicit updates for installed roles remain available. 8.7.1 records that after upgrading you must run a separate subcommand and reopen a pane, which is an admission that upgrades are not seamless. The Windows beta notes say the binaries are unsigned and that the updater is diagnostic-only for that tier.
Most projects put this material in a changelog nobody reads. Putting it in the readme, above the install instructions, is the right call and it is the reason this article leads with it rather than with the feature list.
A draft you are typing gets cleared after 180 seconds
There is a timer in the human and agent queue mode, and when it expires it destroys what you were typing.
The behaviour is stated as a five-step sequence. If your input box is empty, the next queued message is delivered. If it is not empty, the system waits up to 180 seconds, and clearing or submitting your draft releases the message once the agent is idle. If the box is still not empty after 180 seconds, the draft is cleared once, the box is confirmed empty, and only then is the message delivered. The text adds two things in bold: continuing to type does not reset the timer, and this mode does not preserve a draft indefinitely.
There is also a guard. If the input is in a busy, modal or unrecognised state, the system keeps waiting without clearing or sending, and closing the modal lets checks resume.
So the destructive path only fires on a recognised input surface, which is a sensible restriction. But the effect on a normal user is still this: start typing a reply, get distracted for three minutes, come back to an empty box and an agent's message already delivered.
The stated purpose is avoiding the interruption that comes from a result landing in the middle of your sentence, and avoiding accidentally submitting your half-written text as part of an agent's message. Both are real problems. The chosen fix trades them for a timeout that discards work, and it is at least documented precisely enough that you can decide whether three minutes is the right number for how you work.
The npm package excludes Windows, ships no source, and adds four commands
Read the package manifest as a distribution contract rather than as metadata, because three of its fields change what happens on your machine.
First, the platform list restricts installation to Linux and macOS, on two processor architectures, with Node 18 or newer required. npm will refuse to install this on Windows. Yet the readme carries a native Windows beta section. Those are not in conflict, because the Windows path is a separate artefact installed by its own script, but it does mean the two supported-looking paths are actually two different products.
Second, the published file list contains four command launchers, two install-time scripts, the readme and its translations, the licence, and a version file. There is no source code in the tarball at all. The repository is a Python project with a Rust component, and neither reaches npm. What you install from npm is a launcher that then obtains the payload, which is why the readme can say that the self-updater prints the equivalent npm command and declines to modify the vendored payload in place on an npm-managed install.
The two documented install paths are these:
npm install -g @seemseam/ccb@latestand, for a GitHub release-package or source install, the transactional updater:
ccb updateThird, the manifest maps four commands, not one. Installing globally puts the main command plus three others on your path, for sending a request to another agent, for starting something new, and for transferring context. That is worth knowing before you run a global install, since a name as short as the first one may collide with something else.
Two more fields are unremarkable but complete the picture. Access is declared public, and there is a dry-run check script for the package contents.
AGPL-3.0-only in the manifest, empty in the repository metadata
There is a licence inconsistency here, and the specific form of the identifier matters.
The recorded licence for the repository is empty rather than a named licence. The package manifest declares a single specific licence, and it is the strong copyleft variant with the no-fallback modifier: AGPL-3.0-only.
Those differ in a way that is not cosmetic. AGPL extends copyleft obligations to network use, so the obligations reach beyond distribution of the code to offering the software as a service. The `-only` form means there is no alternative licence grant offered alongside it, which is the stricter and more deliberate way to write it.
A licence file is present at the top level of the repository, alongside the manifest and the readme, so the text is shipped.
This article will not tell you which of these governs, and it will not interpret what the obligations mean for a particular deployment. What it will say is that an empty recorded field and a specific strong-copyleft identifier in the manifest are not the same statement, and that for a tool whose whole purpose is to sit between you and hosted model providers, which one you are operating under is a question worth resolving with the project rather than assuming.
The identifier being written precisely, with the modifier attached, suggests it was chosen rather than defaulted.
Python, Rust and JavaScript in one repository
The repository's recorded primary language is Python, and its top-level listing contains a directory named for Rust, a package manifest for npm, and a Python entry script.
So there are three languages doing three different jobs. The application logic is Python, since that is what the language detection settles on and what the entry script at the top level would be. The npm package is a thin JavaScript layer whose only job is to install and launch the payload. And there is a Rust component with its own directory.
The readme does not say what the Rust part is for, and the directory name gives no clue. Given that the project describes itself as lightweight and that the terminal integration is its core, a native component for something performance-sensitive is a reasonable guess, but it is a guess and the repository does not settle it.
The rest of the top level is unusually broad for a single tool, and it explains the scale of what this project actually is. Alongside the language directories there is a mobile directory, matching the mobile app the navigation advertises. There is a directory for model context protocol integration, and a separate one whose name suggests skills are inherited rather than duplicated. There are platform directories, a deploy directory, a tools directory, a dev tools directory, a scripts directory, and two separate test locations.
So this is not a small wrapper. It is a workspace application with a mobile client, a daemon, an extension mechanism and three language layers, which reframes how much the short feature list is actually promising you.
Two provider classes with deliberately different surfaces
The project draws a distinction between kinds of agent that most wrappers blur, and the sentence drawing it is unusually pointed.
Interactive command line agents are described as full native terminals, with visible layout control and direct takeover. Service-backed providers instead keep an explicit managed host and log surface, and the readme adds that the project does not pretend that surface is their request protocol.
That last clause is the interesting one. It is an explicit refusal to emulate a terminal protocol for a hosted service in order to make it look interchangeable with a local one. That choice costs convenience, because you cannot treat every provider identically, and it buys honesty about what you are actually talking to.
The collaboration model on top of that is described as stable inter-agent communication for graphs of a specific shape: one agent feeding another, several feeding one, and one feeding several. So the topology is part of the design rather than something the queue happens to support.
Concurrency is then defined precisely. Requests and returned results share a single chronological first-in-first-out queue per target agent. Each message waits for the target to finish the previous one, including the previous one's result. A later reply cannot interrupt an earlier reply's processing turn. Different agents can still work in parallel.
So parallelism is across agents and strict serialisation is within one. That is a coherent model, and stating that a later reply cannot cut in front of an earlier one is the kind of detail that saves debugging time.
A mobile controller with voice control and remote terminal access
One of the five reasons the readme gives for the project is a mobile remote controller, described as cross-provider voice control, file transfer, and remote terminal access.
All three of those are worth pausing on separately, because together they describe a phone driving terminal sessions on a machine where coding agents hold credentials and repository write access.
Remote terminal access is the headline. It means the terminal panes this tool manages are reachable from another device, and since the whole premise is that those panes are running agents with your permissions, the phone is a second front end onto the same authority.
File transfer moves data between the two machines, which is the feature people usually want and also the one with the sharpest edges if it runs in both directions without thought.
Voice control is the least expected of the three, and it sits oddly beside a project whose recent work has been about input guards and atomic input sequences. A voice interface is the hardest possible input surface to protect, since there is no draft buffer in the usual sense.
The readme's own recommendation is worth noting against all this: test the queue modes with the providers it has actually verified, in managed terminal panes, and do not assume the input protection applies to providers not yet covered.
That advice generalises. If you are enabling the mobile controller, the provider you test with is the provider you should trust.
Ten readmes ship in the tarball, and four planning documents sit at the root
A few repository details round out the picture, and they say something about how this project is run.
The readme exists in ten languages. English is the current one, and there are Chinese, Japanese, French, German, Arabic, Spanish, Portuguese, Korean and Russian versions in a directory beside it. The published file list includes every one of them, so all ten readmes travel in the npm tarball while no source code does. For a tool with this much install-specific detail, that is a defensible allocation of package weight, and it is also an unusual ratio.
At the top level there are two changelogs, one for the current line and one retained from the 4.0 era. There is an optimisation plan document and a separate plan notes document, plus a directory of further plans and an archive directory. So four planning or historical artefacts sit in the repository root alongside the readme.
None of that is wrong, and for a project shipping pre-1.0-style patch numbers with documented upgrade steps, keeping the old changelog is sensible. But it is a sign of a repository where the process is as much of the artefact as the code.
One more detail is worth a mention because it is genuinely odd. There is a configuration file at the top level named for a different AI coding tool. Whatever it configures, it means this repository ships settings for a competing assistant, which is either a leftover or a deliberate interoperability gesture. The readme does not say which.
Taken together with the daemon that keeps project state alive when you close the interface, the picture is of a tool with real operational weight: a background process, an upgrade cycle that requires a restart while idle, and a mobile client.
Editorial conclusion
This suits someone already running two or more CLI coding agents who wants them in visible panes they can take over, and the honesty in the release notes is a genuine reason to trust the rest of it. Five things to establish first. Which providers you actually need, because input protection is documented as tested for a named subset and explicitly not assumed for the rest. Whether the draft-clearing behaviour is acceptable in your workflow, since typing and stepping away for three minutes costs you the draft by design. How you installed it, because an npm install is a launcher and its updater deliberately declines to self-modify, while a release-package or source install is where the transactional updater applies. Whether you are on a supported platform, since npm refuses Windows and the Windows path is a separate unsigned beta with a heavy dependency list. And which licence governs, because the manifest and the repository metadata disagree.
Frequently asked questions
Can Codex and Claude talk to each other?
That is what the project is for. Requests and returned results share one chronological first-in-first-out queue per target agent, where a request is sent with one command and a result comes back with another. Each message waits for the target to finish the previous one including its result, a later reply cannot interrupt an earlier reply's processing turn, and different agents can still work in parallel. The readme names supported collaboration graphs including one agent feeding another, several feeding one, and one feeding several.
Why use Codex instead of Claude?
This repository does not rank providers. It names a long list of command line agents it coordinates, recommends testing its queue modes with two of them plus one other, and records in its 8.7.3 notes that it made composer detection model-independent so behaviour no longer varies by model name. Input protection is described as verified for a named subset, with other providers to follow and their existing delivery behaviour unchanged.
Does CCB work on Windows?
Not through npm. The package restricts installation to Linux and macOS on x64 and arm64 and requires Node 18 or newer, so npm will refuse on Windows. Windows support is a separate native x64 beta distributed as a GitHub release archive with a checksum sidecar to verify, installed with a PowerShell script. It requires Python 3.10 or newer, WezTerm, Git Bash and a named helper at 0.8.0 or newer, and its binaries are unsigned.
What does ccb update do on an npm install?
On an npm-managed install it prints the equivalent npm command and does not modify the vendored payload in place. For a GitHub release-package or source install it acts as the transactional updater. It also checks installed provider command line tools and offers supported updates once, with flags for report-only checking, non-interactive update, or skipping. An install-time script runs automatically when the package is installed.
What commands does installing CCB put on my PATH?
Four. The package maps the main command plus three more, for sending a request to another agent, for starting something new, and for transferring context. The published tarball contains those four launchers, two install-time scripts, all ten translated readmes, the licence and a version file. No source code is included, which is why an npm install is a launcher rather than the program itself.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/seemseam-claude-codex-bridge)Star history chart for your README
[](https://hysenlabs.com/projects/seemseam-claude-codex-bridge)Was this useful?