PakePlus-Android: Packaging a Web Page Into an App Through Your Own GitHub Token
Turn any webpage/HTML/Vue/React and so on into a desktop or mobile app under 5MB, easily and in just a few minutes. https://ppofficial.netlify.app
At a glance
- What is it?
- PakePlus-Android is the Android side of the PakePlus project, which wraps a webpage or a compiled Vue or React build into an app by running builds in your GitHub account. This piece covers the token model, the Mac signing workaround, the Tauri version split and what the repository itself contains.
- Who is it for?
- PakePlus-Android suits people who want to wrap a site or a static build into a client without installing a toolchain, and who accept handing a GitHub token to a desktop app. It is a poor fit if you need a verified size or speed figure, a signed Mac build with no manual step, or a repository with a long release history, since the only tagged release is v0.0.1.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 59 days ago.
- What is it written in?
- Mainly Lua, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 14, 2026, and from our analysis. They are not legal advice.
Star history
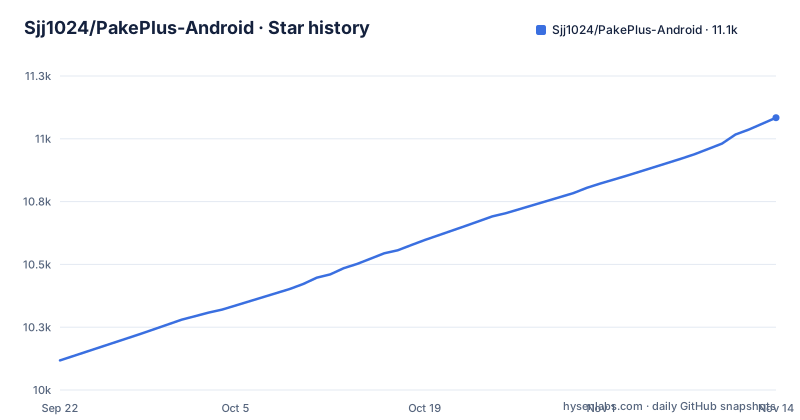
- Sjj1024/PakePlus-Android11,084 ★ · +966
| Repository | 2026-09-22 | 2026-11-14 |
|---|---|---|
| Sjj1024/PakePlus-Android | 10.1k | 11.1k |
966 Stars in the last 53 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The build runs in your GitHub account, so a token is the real install step
PakePlus does not compile anything on your machine. The README says you need no complex local dependencies, only a GitHub Token, and that packaging happens through GitHub Actions in the cloud. You download the app from the release page or open the web version, configure the token, create a project and set its options. Then you preview the app in a new window and press the publish button, and finally download the result from the release page.
The token is the part to think about. The README states that it is stored only locally and that your project stays in your own Git repo. The consequence of that design is that every build consumes your Actions runs and writes into your repositories. If the token is lost or the account is limited, packaging stops, because there is no local build path to fall back on. The web version works too, but the README recommends the client for stronger functionality.
The token permission lists differ between the beta and the classic version
Two permission sets are given, depending on which version of PakePlus you use. For the beta version the token needs: All repositories access to fork an original template repository, Actions to manage GitHub actions, Administration to fork and manage files in the repository, Contents to add, delete, modify and find repository contents, and Issues to submit issues to PakePlus.
For the classic version the list is shorter. It asks for repo, to fork and manage template code, and workflow, to compile and release your software. A classic repo scope is broad on its face, and the beta list includes Administration and write access to repository contents. Whichever you pick, you are giving a desktop app the ability to modify repositories. A sensible habit is to create a token for a dedicated account or a repository you can afford to lose, and to match the permission set to the version of the client you actually installed.
Mac builds need the quarantine attribute removed by hand
On macOS the app can be reported as damaged on first launch. The FAQ explains why: the application would need an official signature, which costs 99 dollars per year, so users are told to bypass it manually. After clicking cancel, run this for PakePlus itself and reopen the app:
sudo xattr -r -d com.apple.quarantine /Applications/PakePlus.appThe same warning appears for apps you package, and the same fix applies with your own app name in place of the placeholder:
sudo xattr -r -d com.apple.quarantine /Applications/YourAppName.appThe practical consequence is that anything you ship to Mac users from this pipeline asks them to run a sudo command in a terminal. That is acceptable for an internal tool you hand to colleagues, and a real obstacle for a public download.
Builds from before 2025 sit on Tauri v1, later ones on Tauri v2
The FAQ carries a version warning. If you hit problems, download the latest version, because versions developed before 2025 were based on Tauri v1.0, and in 2025 the project moved to Tauri v2.0. The desktop side is described as built on Tauri, while Android and iOS apps are described as using native frameworks and being smaller and faster than Tauri2.
For a reader this means two different histories behind one name. An old installer found on a mirror is not the same engine as a current one, and an issue reported against one may not apply to the other. The release list for this repository shows a single entry, named PakePlus v0.0.1 and dated 2026-05-07, so the repository itself gives you no series of tags to compare. Use the release page of the main PakePlus project for the client, as the README directs, and treat this Android repository as one piece of that pipeline.
This repository is a Gradle project plus a small Node worker
The top level of the repository holds app/, packages/, scripts/, docs/, build.gradle.kts, settings.gradle.kts, gradle.properties, gradlew and gradlew.bat, alongside package.json and pnpm-lock.yaml. So there is an Android Gradle build with a Node script layer beside it. The package is named pakeplus-android at version 1.0.0 with the description Pake Plus Android.
Its scripts are two. The first, pp:worker, runs node ./scripts/ppworker.cjs. The second, restore, runs git restore . and so resets the working tree. Runtime dependencies are commander, fs-extra and sharp. Note the licensing detail: the LICENSE file and the GitHub metadata say MIT, while package.json says ISC. GitHub also reports the primary language as Lua, which does not match the Gradle layout, so do not rely on that label to judge what the code does.
The size and speed figures are the project's own claims
The README makes several numeric statements. It says an app is under 5MB, that it is approximately 20 times smaller than Electron and 10 times faster, and that conversion takes 9 minutes. The repository description says a few minutes instead. These are the project's marketing statements, and nothing in the repository data backs them with a measurement or a method.
So treat them as claims. If app size matters to you, build your own app and look at the produced file. The same applies to the statement that the native Android and iOS path is smaller and faster than Tauri2: it is a comparison made by the README, not something you can confirm from the repository contents. If a decision depends on those numbers, measure with your own page before committing to the tool.
Script injection and static packaging define what you can wrap
Two inputs are supported. You can point at a website, or you can drop in a compiled dist folder or an index.html from a Vue or React project and have it become a client app. Custom JavaScript injection lets you write your own JS to run inside the page, and a debug mode helps during preview or release.
The listed use cases include turning a site into a client, packaging a front end you do not want to host on a server, restricting an internal platform to a dedicated client and hiding ads with injected JavaScript. What a wrapper like this does not change is the site itself. Hiding a web address only hides it from casual sharing, and restricting access to a dedicated client is only as strong as the server-side checks behind it. The wrapped page still loads from wherever it is hosted unless you packaged static files.
Editorial conclusion
PakePlus-Android suits people who want to wrap a site or a static build into a client without installing a toolchain, and who accept handing a GitHub token to a desktop app. It is a poor fit if you need a verified size or speed figure, a signed Mac build with no manual step, or a repository with a long release history, since the only tagged release is v0.0.1. Before using it, decide whether the beta or classic token permissions are acceptable for the account you will use, and check which Tauri generation your build comes from.
Frequently asked questions
What is PakePlus-Android?
PakePlus-Android is the Android part of PakePlus, which turns a webpage or a Vue or React build into a desktop or mobile app. Packaging runs through GitHub Actions using your own GitHub token.
Does PakePlus-Android need local build tools?
The README says there is no need to install complex dependencies locally and that all you need is a GitHub Token. Builds run in GitHub Actions in your own repository.
Why does a PakePlus app show an App is damaged warning on Mac?
The app lacks an official Apple signature, which costs 99 dollars per year. The FAQ tells users to run sudo xattr -r -d com.apple.quarantine on the installed .app and reopen it.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/sjj1024-pakeplus-android)Star history chart for your README
[](https://hysenlabs.com/projects/sjj1024-pakeplus-android)Was this useful?