Stoplight Elements' newest published version is from February 2021
Build beautiful, interactive API Docs with embeddable React or Web Components, powered by OpenAPI and Markdown.
At a glance
- What is it?
- A set of Apache-licensed React and Web Component pieces for rendering OpenAPI descriptions as documentation, with three OpenAPI versions supported and examples for three frameworks. The repository has been committed to as recently as September 2026 while the newest tag on the package registry is five and a half years old, and the toolchain that builds it is a 2020 linter sitting beside 2026 CSS tools.
- Who is it for?
- Use this if you want API documentation rendered in your own site without a hosted platform, because that is the whole value and the component boundary is clean. Three things to check before you adopt it.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 3 days ago.
- What is it written in?
- Mainly TypeScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 21, 2026, and from our analysis. They are not legal advice.
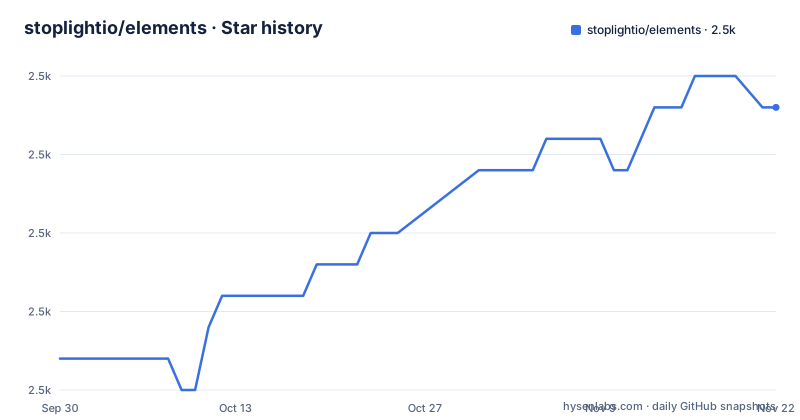
Star history
- stoplightio/elements2,474 ★ · +8
| Repository | 2026-09-30 | 2026-11-21 |
|---|---|---|
| stoplightio/elements | 2.5k | 2.5k |
8 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The newest published version is five and a half years old
The release list is short and stops in 2021: v6.1.10 dated 2021-02-09, preceded by v5.2.7 in November 2020 and v5.2.6 in September 2020. The repository's last push is dated 2026-09-30. So the tree has moved a long way past the newest tag, and anyone installing from the package registry gets code from 2021 rather than the code in the repository. That gap matters more here than it would for an application, because this is a component library: a consumer's bundle is built from the registry version, and a bug fixed on the default branch fixes nothing for them until a release is cut. The page does not draw attention to the gap, and there is no notice that the published version is behind. The demo links point at a subdomain rather than the vendor's own marketing domain, so a reader evaluating whether the project is current has to compare two dates rather than one.
A 2020 linter sits beside 2026 CSS tooling
Read the root manifest's development dependencies in order and it looks like a project that updates some things and not others. The linter is on major version 7, released in 2020. The code formatter is on major version 2. The unit test runner is on major version 26, also 2020, and the end-to-end runner is on major version 13, several years newer. The TypeScript ESLint plugins are on major version 4 while the CSS stack is current: a postcss at 8.5 and a CSS loader at 6.7, with a minifier at 5.0. The monorepo tool is lerna 7. None of that is wrong, and mixing generations is normal in a long-lived repository where the JavaScript toolchain moves faster than anyone wants to migrate. But it tells you something specific about the risk profile: a lint or test failure after an upgrade is more likely to be an ecosystem incompatibility than a logic bug, and the two runners make that diagnosis slower than it needs to be.
Two test runners and a version gap inside one dependency list
The repository configures both a unit runner and a browser runner: a jest config and a setup test file at the root, a Cypress config and a Cypress directory, plus environment packages for the DOM and a reporter that emits JUnit XML. That is not unusual for a component library with a visual surface, and having both means fast unit tests plus a few end-to-end checks. The awkward part is inside the dependency list itself. The unit runner is on major version 26 while its JUnit reporter is on major version 12, which is a gap of fourteen majors between a reporter and the runner it reports for. The browser runner is on major version 13 while the testing library integration for that same runner is on major version 10. Neither pairing is necessarily broken, and both may be deliberate, but a reader trying to work out which runner a given test belongs to has to infer it from the file layout rather than read it, and a future upgrade of either tool will land on whoever happens to touch it.
The lockfile is refreshed by a scheduled script in the repository
One filename at the root is worth more than a paragraph of documentation: a shell script whose name says it maintains the lockfile weekly. That is an unusual practice, and a sensible one for a repository with dozens of development dependencies on a floating version policy. Most of the manifest entries carry a caret rather than an exact pin, so the lockfile is the only thing standing between two installs, and a weekly job implies the project accepts that the lockfile will otherwise rot between releases. The same root holds a script for pointing the demo at a locally built copy of the components, which is the other half of working on a library like this: you need a way to see your change without publishing it. There is also a deploy configuration file for one hosting provider and a Storybook directory, so the components have a visual development environment as well as the demo applications.
Installation analytics are on by default and every consumer must opt out
This is the part of the page a reader should not skip, because it affects everyone who installs the package rather than only the maintainers. The components use a third-party analytics service to collect anonymized installation analytics, and the page says these only run during installation. Two opt-outs are given: a settings block in the consumer's own manifest that switches the collection off, and an environment variable set at install time. Both are per-consumer actions, which means the default for every new project that installs this package is to send an installation ping unless someone remembers to stop it. The page does give the opt-out instructions plainly and links to the documentation of what is sent, which is more than most packages do. The asymmetry to hold in mind is that the maintainers get the data by default and each adopter has to spend a decision to remove themselves from it.
The code samples and the request sampler are other people's packages
The thanks section names exactly two upstream projects, and they are load-bearing. One is the library that turns an operation into code samples in several languages, credited to a different API tooling vendor. The other is the request sampler, credited to yet another vendor whose own documentation product competes in the same space. So two of the most visible features, the automatic code samples and the try-it console, are maintained by companies with their own priorities. That is normal in this ecosystem and usually a sign of good manners rather than a problem, but it does mean an Elements upgrade does not necessarily upgrade the sampler. It also means the acknowledged dependencies in this repository are a subset of the real ones: everything those two packages pull in arrives transitively, and none of it is visible in the acknowledgements.
The roadmap is a completed checklist next to a suggestion form
The roadmap section is nine items long and every box is ticked. The API console, described as the try-it feature, is done. Automatic code samples are done, automatic examples are done, React and Web Component support are done. OpenAPI support is ticked three times, once each for version 3.1, 3.0 and 2.0. Callbacks, webhooks and multiple APIs under the dev portal name are all done as well. Then the section ends by pointing at an external roadmap site to submit ideas for new functionality. So the in-repo list has been finished for some time and has simply not been retired, while the actual suggestion channel is somewhere else. The OpenAPI version support is the substantive line in that list: a documentation renderer that still handles version 2.0 five years after 3.1 landed is carrying a compatibility burden for a great many existing descriptions.
Three example locations, and the quickstart loads from a CDN
The examples live in more than one place, and each is meant for a different integration. There is a demo application with its own manifest, its own transpiler config, its own environment file and its own bundler config. There is an examples folder holding three projects: one built with a React application generator, one Angular application using the Web Component distribution, and a single HTML page that loads the Web Component build through a global script tag. Then there are the snippets in the page itself, and the React one is a single install command plus a component with a description URL:
npm install @stoplight/elementsThe Web Component snippet is truncated partway through an attribute, so it is a shape rather than something to paste. That snippet also reveals the zero-build path: the script and the stylesheet both come from a public content delivery network, so the smallest possible integration has no build step but does have a runtime dependency on somebody else's CDN and a pinned version you have to choose.
Editorial conclusion
Use this if you want API documentation rendered in your own site without a hosted platform, because that is the whole value and the component boundary is clean. Three things to check before you adopt it. First, which version you actually get: the newest published tag is from 2021 while the repository has five and a half years of commits behind it, so an install from the registry is not the code in the tree, and you should read the two changelogs separately. Second, what the install tells someone else: anonymized installation analytics run by default in every consumer's project unless each one opts out, and opting out is a per-project configuration change that has to be made deliberately. Third, what you inherit: the code samples come from one vendor's package and the request sampler from another's, so two of the visible features are somebody else's maintenance burden.
Frequently asked questions
What is Stoplight Elements?
It is an Apache-2.0 licensed set of user interface components for rendering API documentation from OpenAPI descriptions and Markdown, published under the scope of one npm package. It is available both as React components and as Web Components, and the page describes two layouts: a three-column arrangement and a stacked one intended for integrating into a content management system that brings its own navigation.
How do I install Stoplight Elements?
For React, one install command for the scoped package followed by importing a component and giving it the URL of an API description. For plain HTML, load the Web Component script and stylesheet from a content delivery network and add an elements-api element carrying the description URL and a router setting. The examples in the page render the GitHub REST API description.
Which OpenAPI versions does Stoplight Elements support?
Versions 3.1, 3.0 and 2.0, each with its own ticked entry on the in-repository roadmap. That version 2.0 is still listed is the notable part, since it means the renderer carries a compatibility path for descriptions written years before the current specification.
Does installing Stoplight Elements send analytics?
Yes, by default in the consuming project. The page says anonymized installation analytics run only during installation, and gives two opt-outs: a scarf settings block set to false in the consumer's manifest, or an environment variable set to false for the install command. Neither is on by default, so every adopting project has to make the decision itself.
What is the latest version of Stoplight Elements?
The newest published release is v6.1.10, dated 2021-02-09, after v5.2.7 in November 2020 and v5.2.6 in September 2020. The repository's last commit is dated 2026-09-30, so an install from the package registry gives you the 2021 code rather than the current tree.
Can I run the Stoplight Elements examples locally?
Yes. The page gives four steps: clone the repository, open the examples folder and pick one, run the package manager to install, then run the start script. The three examples are a React application generator project, an Angular application using the Web Component build, and a single HTML page that loads the Web Component through a global script tag, which the page says you can open directly with no install step.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/stoplightio-elements)Star history chart for your README
[](https://hysenlabs.com/projects/stoplightio-elements)Was this useful?