Two configuration tiers, a C++ toolchain for arm64, and release tags that are all nightlies
AIOStreams consolidates multiple Stremio addons and debrid/usenet services - including its own suite of built-in addons and a native Usenet streaming engine - into a single, highly customisable super-addon.
At a glance
- What is it?
- AIOStreams is a self-hosted Stremio super-addon that merges configured addons and debrid or usenet services into one filtered list, with its own web app on the same instance; the parts that decide whether an install works are the split between bootstrap variables and database settings, and a Docker build that compiles native addons because one of them has no arm64 prebuild.
- Who is it for?
- AIOStreams fits a Stremio user who wants one configuration surface instead of six addon settings pages, and who is prepared to hold a debrid subscription if any of the built-in addons search torrents. Four things to check before you trust an instance.
- Can I use it commercially?
- Yes, with strict conditions. AGPL-3.0 is a network copyleft licence: if people use a modified version over a network, for example as a hosted service, you must offer them its source code under the same licence.
- Is it still maintained?
- Yes. The repository last received commits 1 day ago.
- What is it written in?
- Mainly TypeScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
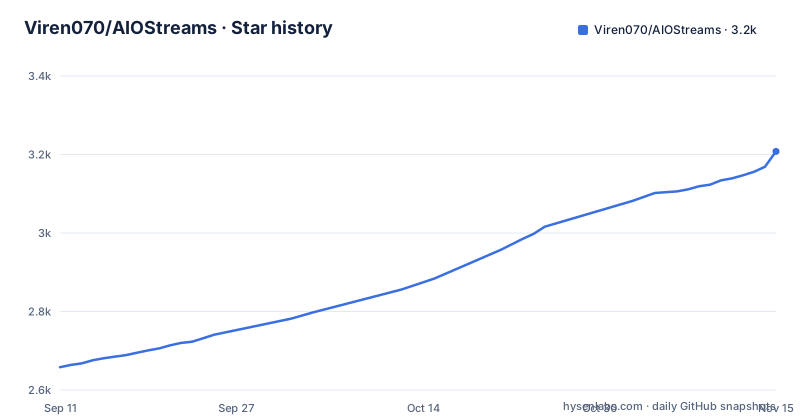
- Viren070/AIOStreams3,208 ★ · +550
| Repository | 2026-09-11 | 2026-11-15 |
|---|---|---|
| Viren070/AIOStreams | 2.7k | 3.2k |
550 Stars in the last 65 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Bootstrap variables lock the dashboard fields they duplicate
The sample environment file states the configuration model before it lists a single variable, and it is two tiers rather than one.
The first tier is bootstrap: variables read from the environment only, before the database is available, covering the things needed to start the process, which the file names as server, database, encryption, operator auth and logging. Those must be set in the file and cannot be changed from the dashboard. The second tier is runtime: branding, presets, built-ins, proxy, caching, rate limits, limits and metadata, all stored in the database and edited on the Settings page where they can be changed live and validated.
The catch is in the overlap. Every runtime setting also has a matching environment variable, and setting one there locks the value, which turns the field read-only in the interface. The file says to do that only if an immutable, env-pinned value is what you want. The first section is marked ESSENTIAL (REQUIRED) and begins with the base URL of the addon, including protocol, hostname and port if not behind a reverse proxy, used for installation URLs, self-scraping detection and genre links. An upgrade note points at a migrations page for version 2.30.
The compose file is four settings, one data directory and no version
Everything needed to run an instance from the repository side is ten lines:
services:
  aiostreams:
    image: ghcr.io/viren070/aiostreams:latest
    container_name: aiostreams
    restart: unless-stopped
    ports:
      - 3000:3000
    env_file:
      - .env
    volumes:
      - ./data:/app/data
Two of those lines decide your experience. The image reference is the floating latest tag, so the build that starts after a new publish is not the build that was running before, and nothing in the file pins a digest or a tag. The env_file has no fallback, so a missing .env stops the stack before the process ever reads a variable.
Port 3000 is the only published port, and the data directory is the only volume, which is where the database and configuration the app writes at runtime end up. Restart unless-stopped means the container comes back after a reboot but not after docker compose down. Nothing here mentions a reverse proxy, although the base URL variable asks for a port when the service is not behind one.
Three recent releases are nightlies from one evening, and package.json says 2.35.9
The three most recent releases are 2026.10.03.1821-nightly, 2026.10.03.1753-nightly and 2026.10.03.1641-nightly, published within about two hours of each other on 2026-10-03. The naming is a date, a time and the word nightly.
Inside the repository a second scheme runs. package.json carries version 2.35.9, the release script is commit-and-tag-version, and CHANGELOG.md sits at the root. Alongside those, release-please-config.json and .release-please-manifest.json are both present, which is a third mechanism sitting in the tree alongside the first two.
So the version a user sees in a release feed, the version in the manifest and the tag commit-and-tag-version writes are three different strings for the same tree, and the default branch is main. For anyone pinning an instance, that is the practical hazard: the compose file points at latest, the feed is full of nightlies, and the only semver visible in the repository is a static field in a JSON file.
The last push to main is dated 2026-10-02, one day before those nightlies, so the branch and the release cadence are close together here.
The build chain names six packages in order, dev starts four
The workspace is packages/*, and the build is a chain of six filtered commands in a fixed order:
"build": "pnpm -F crypto run build && pnpm -F core run build && pnpm -F server run build && pnpm -F frontend run build && pnpm -F jellyfin-web run build && pnpm -F seanime-extensions run build",Order is not decorative here: crypto is built before core, core before server, and the user facing pieces come last.
The development script covers four of the six:
"dev": "pnpm -F core -F server -F frontend -F jellyfin-web --parallel dev",So crypto and seanime-extensions are built for production but not started in development, which is a reasonable split for a compiled crypto package and a less obvious one for a media player extension. Two other details: the production start runs node with --max-semi-space-size=8, a heap tuning flag that only matters for a long-running server, and the development start goes through cross-env to set NODE_ENV before tsx watch takes packages/server/src/server.ts. Documentation has its own build and dev scripts pointing at a docs package that is not in the six.
arm64 builds compile yencode because it ships no prebuild for it
The image starts from a pinned Node release and enables pnpm through corepack:
FROM node:24.18.1-slim AS base

ENV PNPM_HOME="/pnpm"
ENV PATH="$PNPM_HOME:$PATH"
RUN corepack enable
The builder stage then installs a compiler toolchain, and the Dockerfile explains why in the comment above it. Native addons that lack prebuilt binaries on the platform have to be compiled with node-gyp, and yencode, used by the native usenet engine, has no linux/arm64 prebuild. That needs Python and a C and C++ toolchain, so python3, make and g++ are installed.
The comment also explains the shape of the final image: those tools live only in the builder and runtime stages, and the distroless image copies the already-compiled .node binaries so it stays clean. In practice that means an arm64 host does the compiling, a build of several minutes rather than a layer download, and a runtime image with no shell package manager in it. Anyone cross-building for a Raspberry Pi or an arm64 server should expect that step to be the slow one.
The Dockerfile copies package-lock.json while the repo installs with pnpm
One instruction in the Dockerfile is out of date with the rest of the repository. The comment above the copy step reads Copy the relevant package.json and package-lock.json files, and the instruction is a glob:
COPY package*.json ./
COPY packages/server/package*.json ./packages/server/
COPY packages/core/package*.json ./packages/core/
The install two steps later is pnpm install --frozen-lockfile, and the lockfile in the tree is pnpm-lock.yaml next to pnpm-workspace.yaml. There is no package-lock.json, so the glob matches the manifests only. The per-package copies exist so the dependency layer can be cached without copying sources, which is the right reason to have them.
The next line is more interesting:
COPY patches ./patchesA patches directory next to a frozen lockfile means some dependencies are patched at install time rather than pinned to a published version, so the exact dependency tree cannot be reconstructed from the registry alone. Anyone auditing what runs inside the container has to read those patches too, and nothing in the visible documentation calls them out.
The app plays links only, so P2P torrents are out of scope
The same instance that serves the addon also serves a web app, and the constraint that shapes it is stated early: it plays streams with a link, such as debrid and Usenet ones, so P2P torrents are not supported. That single sentence explains the whole player design.
Nothing extra has to be self-hosted and there is no Jellyfin to install, because the app runs on the AIOStreams instance itself. Public instances have it on except ElfHosted's, and ElfHosted's private instances have it off until the owner turns it on. On a television, the same configuration presents as a Jellyfin-compatible server, so Swiftfin, Findroid, Infuse, Kodi and Android TV apps can sign in, with a Quick Connect code for the TV case.
The desktop app is marked alpha and covers Windows, macOS and Linux, with an mpv based player for MKV, HEVC, AV1 and styled subtitles, surround output with Dolby and DTS passthrough, your own mpv.conf, input.conf, scripts and shaders, and media keys plus Discord presence. It updates itself on Windows and macOS, with an optional nightly channel, and ships as a Flatpak on Linux. The download link points at a release tag named desktop rather than at the latest release.
Debrid keys are pushed into every compatible addon automatically
The marketplace holds more than eighty community addons, and the credential model is the part worth reading. Debrid API keys are applied automatically to compatible addons, so they are configured once and work everywhere, and any Stremio addon can be added by URL on top of the built-in ones. Manifests are generated dynamically, so addon updates arrive without reconfiguring.
The built-in suite is separate in one specific way: those addons are hosted alongside AIOStreams itself and available exclusively to your instance, configured like any other marketplace entry. The table names Stremio GDrive for streaming from your own Drive, TorBox Search for TorBox's index with more options than the official addon, Knaben as a proxy search across several torrent sites, Zilean against a DMM hashlist instance, AnimeTosho as a mirror of anime releases, and Torrent Galaxy. All of them support anime and Kitsu and MAL catalogs.
The note under that table is the constraint: built-in addons that search for torrents require a debrid service. Usenet results take other routes, through the built-in usenet engine, external tools such as NzbDAV or AltMount, Stremio itself, or TorBox on the Pro plan. Household profiles add a second security surface, since each profile can carry an optional PIN while the main profile sees everyone's history and what each person is playing right now.
Editorial conclusion
AIOStreams fits a Stremio user who wants one configuration surface instead of six addon settings pages, and who is prepared to hold a debrid subscription if any of the built-in addons search torrents. Four things to check before you trust an instance. The three most recent releases are all nightlies published on the same evening, while package.json still carries the semver 2.35.9, so the tag you install is not the version field you read. The compose file uses the floating latest tag, which means a restart can pick up a different build. Bootstrap variables in .env cannot be changed from the dashboard, and setting a runtime setting through the environment makes its field read-only in the UI. And the app only plays streams that have a link, so P2P torrents are out of scope by design, with usenet handled by the built-in engine or by NzbDAV, AltMount, Stremio itself or TorBox on the Pro plan.
Frequently asked questions
How do I access the AIOStreams configuration page?
Runtime settings are edited on the dashboard Settings page, where they are stored in the database and can be changed live and validated, and the addon marketplace is browsed from the configuration page as well. Bootstrap variables are different: they are read from the environment before the database exists and cannot be changed from the dashboard, and setting a runtime setting through its environment variable makes its field read-only in the interface.
Can you use aiostreams without debrid?
For usenet, yes: those results can be streamed by the built-in usenet engine, by external tools such as NzbDAV or AltMount, natively by Stremio itself, or through TorBox on the Pro plan. For torrents, no: built-in addons that search for torrents require a debrid service, and debrid API keys are applied automatically to compatible addons in the marketplace.
What does AIOStreams do with my debrid API keys?
The marketplace applies your debrid keys automatically to compatible addons, so credentials are configured once and work everywhere. Any Stremio addon can be added by URL alongside the built-in suite, and addon manifests are generated dynamically so updates arrive without reconfiguring.
Why does the AIOStreams Docker build need a C++ toolchain?
Native addons without prebuilt binaries for the platform have to be compiled with node-gyp, and yencode, used by the native usenet engine, has no linux/arm64 prebuild. The builder stage therefore installs python3, make and g++, while the final distroless image copies the already-compiled .node binaries and keeps the toolchain out.
Which AIOStreams settings can be changed after it is running?
Branding, presets, built-ins, proxy, caching, rate limits, limits and metadata are runtime settings held in the database and edited on the Settings page. Server, database, encryption, operator auth and logging are bootstrap variables in the environment, read before the database is available, and they cannot be changed from the dashboard.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/viren070-aiostreams)Star history chart for your README
[](https://hysenlabs.com/projects/viren070-aiostreams)Was this useful?