void-packages cannot build as root, and one of its four chroot methods destroys the host
The Void source packages collection
At a glance
- What is it?
- The Void Linux source package collection drives everything through xbps-src, which needs a chroot utility and bind mounts rather than root. Two of its four chroot methods want different kernel namespace options, restricted packages need a line appended to a configuration file, and the licence file is named COPYING while the metadata field is empty.
- Who is it for?
- void-packages is the place to look if you package for Void or want to understand how a source-built XBPS distribution is put together, since the README documents the build driver, the bootstrap strategy and the isolation requirements in unusual detail. Two things to check before you run anything on a machine you care about.
- Can I use it commercially?
- Check first. The repository uses a licence we do not classify automatically, so read its LICENSE file before any commercial use.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly Shell, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
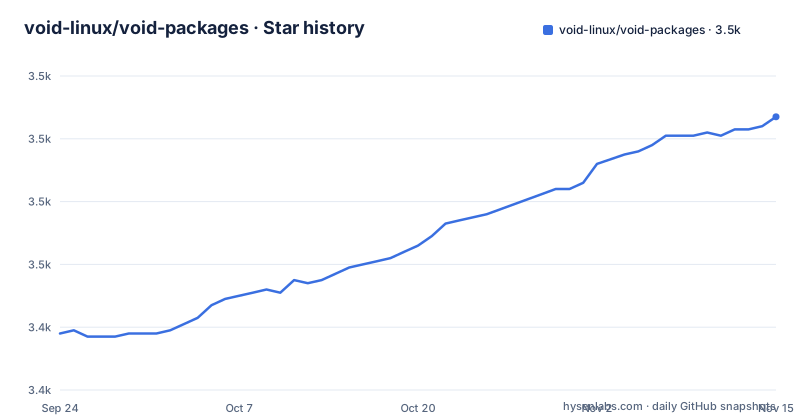
- void-linux/void-packages3,507 ★ · +69
| Repository | 2026-09-24 | 2026-11-15 |
|---|---|---|
| void-linux/void-packages | 3.4k | 3.5k |
69 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
Building as root is refused outright
One line in the requirements section changes everything else: xbps-src does not allow building as root anymore, and the instruction is to use one of the chroot methods instead. The reason is structural rather than stylistic. xbps-src needs a utility to chroot and needs to bind mount existing directories into a masterdir, which it uses as its main chroot directory, and several utilities can do that job. The entry point is two commands:
$ git clone https://github.com/void-linux/void-packages.git
$ cd void-packages
from which a single package is built by naming the pkg target and the package, and ./xbps-src -h lists everything available. The baseline requirements are GNU bash, xbps at version 0.56 or newer, git unless configured otherwise through etc/defaults.conf, ordinary POSIX utilities, and curl, which is required by the update-check target. Bootstrapping from source adds flock from util-linux, bsdtar or GNU tar in that order of preference, install from GNU coreutils, and objcopy, objdump and strip from binutils.
Four chroot methods, and one eats the host
The chroot methods section lists four options and is unusually blunt about the last one. xbps-uunshare is the default and uses user namespaces. xbps-uchroot uses namespaces and must be setgid. bwrap is bubblewrap, described as a sandboxing tool for unprivileged users that works through user namespaces or setuid. And ethereal is described in five words that say everything: it destroys the host system it runs on, and is only useful for one-shot containers, meaning Docker used with CI. So three of the four are isolation mechanisms you can point a normal build at, and one is a deliberate escape hatch for throwaway environments. The README also notes that the flag for selecting a method overrides configuration files entirely.
The two namespace methods want different kernel options
Read the two lists side by side and the difference decides which method works on your kernel. The default xbps-uunshare needs CONFIG_NAMESPACES, CONFIG_IPC_NS, CONFIG_UTS_NS and CONFIG_USER_NS. xbps-uchroot needs CONFIG_NAMESPACES, CONFIG_IPC_NS, CONFIG_PID_NS and CONFIG_UTS_NS, so it wants the PID namespace and does not list the user namespace. A kernel with one of each, which is unusual, satisfies only one method. If the default is missing an option the failure is specific: xbps-src fails with EINVAL, invalid argument. The uchroot path has its own failure mode, an error reading ERROR clone with Operation not permitted, and the documented causes are membership of the right group and the wrong owner, group or permissions on the executable.
uchroot needs a setgid binary and a group membership
Setting up the second method means changing the file and the account. The executable has to be owned by root and a chosen group, given mode 4750, and the user has to be added to that group with usermod. Three commands are given as an indented block. Then a line is appended to etc/conf to select it. The documentation also tells you not to do any of that by hand on Void itself, because your user should already be a member of the xbuilder group, which is the distribution's build group. The setgid requirement is the point of the method: it is how an unprivileged build gets the privileges it needs inside the chroot without being root on the host.
Restricted packages need one line appended to a config file
Some packages are marked restricted and are held back until you opt in. The quick start gives the exact mechanism: append XBPS_ALLOW_RESTRICTED=yes to etc/conf, using a shell append rather than an edit, which means the setting accumulates with anything else already in that file. Once a package is built it lands in hostdir/binpkgs or a subdirectory of it, and the README names hostdir/binpkgs/nonfree as the example for nonfree output. Installation takes a repository argument, or you can use the xi utility from the xtools package, which works out the repository from the current working directory. The whole build invocation is the pkg target with a package name.
Source bootstrap is called unreproducible and time consuming
The bootstrap section draws a clear line between two ways to get a build container. binary-bootstrap is the recommended one: it installs pre-existing binary packages from remote xbps repositories or from your own local repository, and it runs automatically the first time you build a package if no masterdir exists for the host architecture. The bootstrap command builds everything from scratch instead, and the documentation says it is usually not recommended, because those packages are built with your host toolchain and are neither fully featured nor reproducible, since the host system may influence the build. It is offered as a stage zero for bootstrapping new systems, and the text walks through three stages of rebuilding to reach the state binary-bootstrap would have given you directly.
Configuration falls back to three per-user files
Settings live in etc/defaults.conf, which holds everything that can be overridden, and the override file is etc/conf. If etc/conf does not exist, xbps-src tries three locations in order: the file named by XDG_CONFIG_HOME, then the default XDG path under the home directory, then a dotfile in the home directory. So there are four places a setting can come from, and the precedence is defaults, then the repository's own file, then the user's files, with the environment variable taking priority among the user paths. The configuration section in the visible document stops there, and everything after it, covering the directory hierarchy, build options, signing, mirrors, cross compilation and the musl and 32-bit builds, is one click away rather than reproduced here.
The licence file is COPYING and the metadata field is empty
The repository's licence metadata field carries no value, and the root contains a file named COPYING rather than one named LICENSE, so the terms have to be read from that file rather than inferred from the repository listing. The project itself is a packaging collection rather than a library: the root holds the xbps-src driver as an executable script, a srcpkgs directory for the packages, a common directory for shared shell code, and etc for the configuration defaults and templates, plus the documentation files for contributing and for the manual. What the README is, in nineteen table-of-contents entries, is the operating manual for that driver, and the packaging itself is only mentioned through the directory names.
Editorial conclusion
void-packages is the place to look if you package for Void or want to understand how a source-built XBPS distribution is put together, since the README documents the build driver, the bootstrap strategy and the isolation requirements in unusual detail. Two things to check before you run anything on a machine you care about. The build is no longer permitted to run as root, so it needs a chroot method, and one of the four documented methods is described as destroying the host system it runs on. And the licence situation needs reading before redistribution: the metadata field carries no value and the root file is named COPYING, so check that file rather than assuming a licence from the repository listing. For anything beyond packaging, this is the wrong repository, since it contains no packages that install without building them first.
Frequently asked questions
What does the void-packages repository contain?
The XBPS source packages collection used to build binary packages for the Void Linux distribution. It includes the xbps-src script, which fetches and compiles sources and installs the files into a fake destdir to produce XBPS packages that the xbps-install and xbps-query utilities can install and query.
How do I build a single package from void-packages?
Clone the repository, then run the pkg target with the package name, for example ./xbps-src pkg followed by the name. The first build bootstraps from binary packages automatically when no masterdir exists for the host architecture, or you can run ./xbps-src binary-bootstrap yourself, and the built package lands in hostdir/binpkgs.
Why does xbps-src fail with EINVAL or Operation not permitted?
It needs a chroot utility and bind mounts, and it cannot run as root. The default method xbps-uunshare needs the kernel options CONFIG_NAMESPACES, CONFIG_IPC_NS, CONFIG_UTS_NS and CONFIG_USER_NS and fails with EINVAL when one is missing, while xbps-uchroot needs CONFIG_PID_NS in place of the user namespace and requires the executable to be setgid with your user in the right group, which on Void means the xbuilder group.
What is the ethereal chroot method in void-packages?
It is one of four supported chroot methods, and the documentation describes it as destroying the host system it runs on, so it is only useful for one-shot containers such as Docker in CI. The other three are xbps-uunshare as the default, xbps-uchroot, and bwrap from bubblewrap.
How do I enable restricted packages in void-packages?
By appending XBPS_ALLOW_RESTRICTED=yes to the etc/conf file, which is done with a shell append rather than an edit. Output for nonfree packages is placed in a subdirectory such as hostdir/binpkgs/nonfree, and installation takes the repository explicitly or uses the xi utility from the xtools package.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/void-linux-void-packages)Star history chart for your README
[](https://hysenlabs.com/projects/void-linux-void-packages)Was this useful?