Win11Debloat's quick method executes whatever debloat.raphi.re returns, while the ZIP release leaves you a file to inspect
Win11Debloat is a lightweight PowerShell script that removes pre-installed apps, disables telemetry, and declutters Windows 10 and 11 without installation.
At a glance
- What is it?
- A read of Raphire/Win11Debloat: what the one line PowerShell method actually runs, why administrator rights are required and the readme's own warning is the only safeguard, which two security features sit in the same list as ad removal, and why the export and import feature turns one machine's choices into a fleet's choices.
- Who is it for?
- Use the ZIP from the latest release rather than the one line command if you want to see what you are about to run with administrator rights, and read the wiki's reverting page before applying anything on a machine whose BitLocker or Find My Device state matters.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 2 days ago.
- What is it written in?
- Mainly PowerShell, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 13, 2026, and from our analysis. They are not legal advice.
Star history
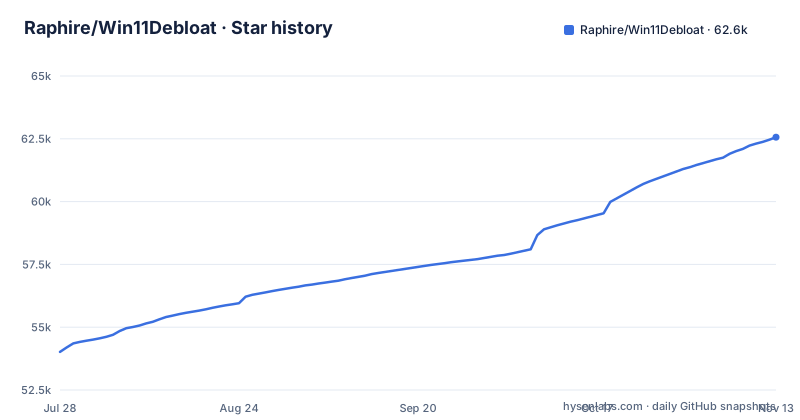
- Raphire/Win11Debloat62,565 ★ · +8,547
| Repository | 2026-07-28 | 2026-11-13 |
|---|---|---|
| Raphire/Win11Debloat | 54k | 62.6k |
8,547 Stars in the last 108 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The quick method fetches a script block and executes it in place
The recommended one line method is a single PowerShell expression, and every part of it matters.
& ([scriptblock]::Create((irm "https://debloat.raphi.re/")))`irm` retrieves whatever that address currently returns, `[scriptblock]::Create` compiles the response as PowerShell code, and `&` runs it. There is no file written to disk first, no version number in the command, and nothing to hash, archive, or read before it executes with the rights you granted it. The code your machine runs is whatever the endpoint serves at the moment you paste the line, which is the honest answer to the question people ask most about this project, whether it is safe to use. The readme's own answer is a warning box rather than a mechanism: great care went into making sure the script does not unintentionally break OS functionality, but use it at your own risk, with an issue tracker linked for problems.
The two manual methods avoid that property. Both download the latest ZIP from the releases page, extract it, and run a file you can open in an editor before executing. That is the difference worth insisting on: the same script, obtained in a form that can be reviewed and kept, or obtained as live text from a short URL.
The .bat launcher closes silently when it fails, and the workaround is a different method
The traditional route is a double click. Download the ZIP, extract it, open the Win11Debloat folder, and run `Run.bat`, then accept the Windows UAC prompt, which the readme states is required for the script to function. What that route does not tell you is how to tell a working run from a failed one, and the readme answers that in the next line: if the console window immediately closes and nothing happens, use the advanced method instead.
The advanced method is the same download with a PowerShell session you control. It requires opening the terminal as an administrator, temporarily relaxing script execution for that session only, changing into the extracted directory, and launching the script by path.
Set-ExecutionPolicy Bypass -Scope Process -Force.\Win11Debloat.ps1The scope is what makes this acceptable: `-Scope Process` applies to the current session and evaporates when the window closes, so nothing permanent changes about the machine's execution policy. Both the quick and the advanced methods document command line parameters for non-interactive use, and both send you to the wiki's command line interface page for them, which is where a scripted deployment should start rather than the on screen prompts.
Administrator rights are a requirement, not a recommendation
The traditional method ends at a UAC prompt, and the readme attaches a condition to it: accept the prompt to run as administrator, this is required for the script to function. That single sentence explains most of the design. The changes in the feature list are registry edits, service start type changes, and app removals, none of which a standard user session can perform, so the tool has no reduced privilege mode. The usage sections do not mention a dry run flag.
The feature inventory shows what that elevation is spent on. Copilot, Windows Recall and Click to Do are disabled and removed, and a named service, WSAIFabricSvc, is prevented from starting automatically. The Drag Tray for sharing and moving files is disabled, the old Windows 10 style context menu is restored, and Storage Sense, fast start-up and the Sticky Keys shortcut are turned off. Update behaviour changes too: updates are held back rather than applied as soon as they arrive, automatic restarts while signed in are prevented, Delivery Optimization sharing with other PCs is disabled, and device companion apps such as the LG Monitor App and Alienware Command Center are blocked from installing themselves.
Run as administrator on a personal machine, that list is a preference sheet. Run it as administrator on a managed machine, the same list collides with policy.
Reverting is claimed for the settings and hedged for the apps
The reversion story is stated in one sentence and the hedge sits in the wrong place for comfort. All of the changes made by Win11Debloat can easily be reverted, and almost all of the apps can be reinstalled through the Microsoft Store. The first clause is a claim about settings and registry state, which is plausible given the shape of the tool. The second is about the removals, and the word doing the work is almost.
So the failure mode is specific. An app removed by the app removal option that is not distributed through the Microsoft Store cannot be reinstalled that way, and the readme's own wording admits the gap without enumerating which apps fall outside it. The wiki page on reverting changes is named as the place to find out more, and that page, not the readme, is the document to consult before running the script on a machine whose installed software you care about.
The same sentence covers the appearance, taskbar, start menu and File Explorer groups, where the changes are the least dangerous and the most annoying to live with if you change your mind. Desktop spotlight, the learn about this picture shortcut, transparent effects, widgets on the taskbar and lock screen, and the file extension display setting are all one checkbox each in a list of dozens, which is the strongest argument for reading the feature list line by line before answering the prompts.
BitLocker auto-encryption and Find My Device sit in the same list as ad removal
The privacy group is where a reader should slow down, because the switches are not all about advertising. Alongside disabling telemetry, diagnostic data, activity history, app launch tracking and targeted ads, and hiding tips, tricks and suggestions across Windows, the lock screen and Edge, the same group disables Windows location services, app location access, and Find My Device location tracking. The system group disables BitLocker automatic device encryption.
Those are two different kinds of change and the readme groups them together. Turning off ad suggestions costs a little attention. Turning off automatic device encryption means a drive added to that machine later is not encrypted by default, and turning off Find My Device means a lost machine cannot be located through it. Neither is a bug, and a person who wants both off has every reason to want them off, but they are security mechanisms rather than noise, and a script that presents them in a list of conveniences does not distinguish them.
This is where the export and import feature stops being a convenience. Settings can be exported and imported to apply the same configuration across systems quickly, so a choice made on one machine, including the security ones, becomes the default for every machine that imports it. On an image used to build laptops, that means the BitLocker and location defaults are decided once, by whoever exported the preset, and the people receiving the machines inherit them.
Export, import and command line parameters turn a dialog into a fleet operation
The administrative features named near the top of the readme are the ones that scale: a command line interface, support for Windows Audit mode, and the ability to make changes to other Windows users. The readme only names these capabilities and sends you to the wiki for details.
Every method ends with carefully reading and following the on screen instructions, so the default experience is a human answering prompts, and the parameters that remove the prompts live in the wiki rather than in the readme. A fleet operator has to go read that page, because the readme links the parameter list there.
The script also targets both operating systems. The description says Win11Debloat works for both Windows 10 and Windows 11, and the feature list includes restoring the old Windows 10 style context menu, which is a change that only means anything on 11. The readme says the script works for both Windows 10 and Windows 11.
The tree has registry files, config schemas and a tests directory with no documented runner
The repository is small and its layout explains the mechanism. The entry point is `Win11Debloat.ps1` at the top level, and `Run.bat` is the launcher for the double click route. `Scripts/`, `Regfiles/`, `Config/`, `Schemas/` and `Assets/` sit alongside it. `Tests/` is there as well, which is unusual for a single script utility and says something about how the author treats changes.
The visible part of the readme does not explain how to run them. The project is MIT licensed and the last push landed on 2026-10-30, with releases named by date rather than version, 2026.10.30, then 2026.08.24, then 2026.07.11, so a follow-up to a specific release means a specific ZIP rather than a tag range.
For a user, the practical advice is to keep a copy of the preset you export or import, since the readme points to the wiki for reverting changes.
Editorial conclusion
Use the ZIP from the latest release rather than the one line command if you want to see what you are about to run with administrator rights, and read the wiki's reverting page before applying anything on a machine whose BitLocker or Find My Device state matters. Do not run it on a fleet through the interactive prompts, because the settings it removes include automatic device encryption and location tracking, and the export and import feature will carry that choice to every machine you apply it to.
Frequently asked questions
Is it safe to use Win11Debloat?
The readme carries a warning that the script should be used at your own risk, and the quick method executes whatever the debloat.raphi.re endpoint returns as a script block, with no file to inspect first. The manual route downloads a ZIP from the releases page instead, which gives you a versioned file to read before running it as administrator.
What does Win11Debloat do?
It is a PowerShell script that removes preinstalled apps, disables telemetry, diagnostic data, activity history, app launch tracking and targeted ads, removes intrusive interface elements, and adjusts system, update, appearance, taskbar and File Explorer behaviour, all without an installation step.
How do I install Win11Debloat?
Nothing is installed. The quick method pastes a single PowerShell line that downloads and runs the script, while the manual methods download the latest ZIP from the releases page, extract it, and either double click Run.bat or run Win11Debloat.ps1 from an administrator PowerShell session after a process scoped execution policy bypass.
What does Win11Debloat remove?
A wide variety of preinstalled apps, plus Microsoft Copilot, Windows Recall and Click to Do, and it prevents the AI service WSAIFabricSvc from starting automatically. The readme says almost all removed apps can be reinstalled through the Microsoft Store, so the store is the recovery path for removals.
How do I use Win11Debloat on other Windows user accounts?
The readme names Windows Audit mode support and the ability to make changes to other Windows users among the features aimed at administrators and power users, and it points to the wiki for the details. Both the quick and the advanced run methods also support command line parameters for customising the behaviour of the script.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/raphire-win11debloat)Star history chart for your README
[](https://hysenlabs.com/projects/raphire-win11debloat)Was this useful?