XPipe: a connection hub that borrows the command-line tools already on your servers
Access your entire server infrastructure from your local desktop
At a glance
- What is it?
- XPipe is a Java desktop application that fronts SSH, Docker, Kubernetes, Proxmox and RDP from a local workstation, installing nothing on the remote side and storing its state in a local vault. The interesting design decisions are all in what it refuses to do remotely: no agent, no server, no stored secrets.
- Who is it for?
- XPipe fits administrators who already have working SSH and container tooling on their machines and want one catalog across many hosts, because it inherits the behaviour of those tools instead of replacing them. It does not fit anyone who wants a server-side component to install once, a hosted control plane, or a single place where remote credentials are stored, since the remote side stays untouched and secrets are delegated to a password manager.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 2 days ago.
- What is it written in?
- Mainly Java, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 12, 2026, and from our analysis. They are not legal advice.
Star history
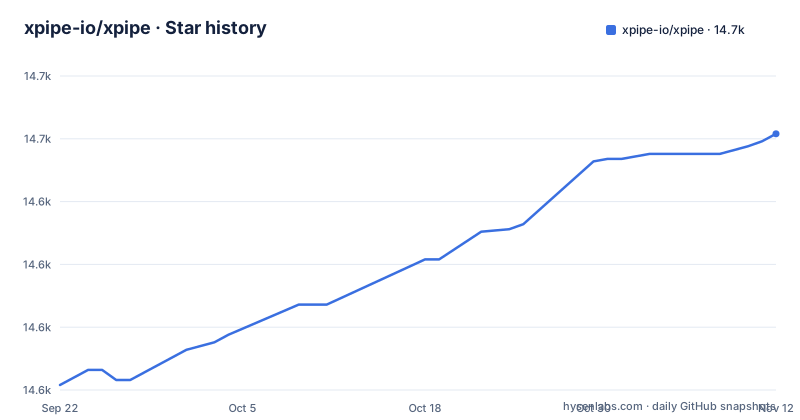
- xpipe-io/xpipe14,652 ★ · +100
| Repository | 2026-09-22 | 2026-11-12 |
|---|---|---|
| xpipe-io/xpipe | 14.6k | 14.7k |
100 Stars in the last 51 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
No agent goes on the remote side, so the remote stays exactly as it was
The architectural bet is stated in a single sentence: XPipe works on top of your installed command-line programs like SSH or docker, and does not require any setup on your remote systems. That means there is no daemon to deploy, no binary to keep in sync with the desktop app, and no upgrade conversation with whoever owns the host. The same principle shows up again in the scripting system, which makes scripts available in the PATH on any remote system without any setup. The tradeoff is that XPipe's capabilities are bounded by whatever those installed programs can do and how consistently they behave across distributions and versions. A host with an old client, a renamed binary, or a wrapper that prompts differently will not become a problem XPipe can fix from the desktop, because the abstraction layer is the tool you already had.
The vault keeps state on your machine and delegates secrets to your password manager
XPipe describes its storage model in unusually direct terms. All data is stored on your systems in a cryptographically secure vault, there are no servers involved, and the application does not send personal or sensitive information to outside services. For authentication, it retrieves secrets automatically from your installed password manager and does not store secrets itself. That is a real architectural decision rather than a feature bullet: the vault is the index of your infrastructure, and the credential that unlocks a host stays in the tool you already trust with credentials. A custom master passphrase can be set for further encryption, which layers a second secret on top of the vault rather than replacing the password manager. What follows from that split is that the password manager becomes a hard dependency for the connections that rely on it. Lose access to it and XPipe still has the connection definitions, but not the means to authenticate to them.
Vault synchronization is a git repository you host and administer yourself
Sharing a vault across machines is done by synchronizing it through your own self-hosted git repository, and the same mechanism is how you share it with other team members. This is consistent with the rest of the design, which avoids hosted components, but it transfers responsibility rather than removing it. The availability of your connection catalog now depends on a git server you run, and the access control on who can read that catalog is whatever your server enforces. There is no sharing service in the middle to audit, and there is also nothing between you and the consequences of a misconfigured repository or a laptop that has been offline for a week. For a team this is a reasonable trade, because the group that wants shared connection definitions is the same group that already runs its own infrastructure. For a single user it is one more self-hosted thing to remember.
The terminal connection is opened before the terminal window exists
The terminal launcher is built around shaving latency off the moment you click a connection. It launches you into a shell in your favourite terminal with one click and fills password prompts automatically. It connects to a system while the terminal is still starting up, which is the detail that separates this from a launcher that spawns a window and then runs ssh inside it. Coverage is broad by design: support for commonly used terminal emulators across all operating systems, a custom command-line spec so you can register an emulator the project has never heard of, shells including bash, zsh, fish, cmd and PowerShell both locally and remotely, multiplexers like tmux and zellij, prompt frameworks like starship and oh-my-zsh, and split pane views for multiple sessions at once. The trade is coupling to your local terminal setup, which has to be installed and configured before the launcher can be pointed at it.
Macros and desktop shortcuts are the path that never opens the GUI
One capability is described as producing desktop shortcuts and macros that automatically open remote connections in your terminal without having to open any GUI. Read literally, that means the application is not a prerequisite for using it day to day. A shortcut can launch a terminal and land you in a configured remote shell, and the shell login environments created in the connection hub can be reused across that path, so the same working setup applies whether you arrived through the window or through a keypress. For anyone who considers the desktop app the weak part of an otherwise terminal-based workflow, this is the feature that answers the objection. The cost is that these entry points have to be configured once in the hub before they are worth anything.
Scripts are injected into the remote PATH and reused inside the file browser
The scripting system covers reusable shell scripts, templates and groups that run on connected remote systems, plus shell init environments for customizing a connection's working state per purpose. Two design points matter. Scripts are made available in the PATH on any remote system without any setup, which is what lets the same helper work across a mixed estate instead of per host. And custom scripts are usable from the file browser, so the same definition that runs on the command line is also the one attached to file operations there. The same reasoning explains the session elevation feature: sessions are dynamically elevated with sudo when required without having to restart the session, so a mid task privilege change does not cost you the work already in flight.
The extension model is a directory in the tree, and the extension points are unnamed
The project invites others to add support for more tools or implement custom functionality through a modular extension system, and the repository layout supports that story: an ext/ directory sits alongside app/, dist/, lang/ and img/, with get-xpipe.sh and get-xpipe.ps1 at the root for fetching the application and a plain version file. The integration surface that the README enumerates is about protocols rather than about programmability: SSH connections, config files and tunnels, Docker with compose, Podman, LXD and incus, Proxmox PVE, Hyper-V, KVM, VMware Player/Workstation/Fusion, Tailscale, Netbird, Teleport, AWS and Hetzner Cloud servers, RDP with gateways and VNC, Windows Subsystem for Linux, Cygwin and MSYS2 environments, Kubernetes clusters, pods and containers, and Powershell Remote Sessions. Most have a docs page under docs.xpipe.io.
Three releases in six days, a commit from the day before, and no central service to fall back on
Activity is current: the repository is not archived, its last push is dated 2026-11-01, and the recent tags are 24.8 on 2026-10-24, 24.9 on 2026-10-25 and 24.10 on 2026-10-29. Three releases inside six days says the project ships on its own cadence rather than on a schedule you can plan around. The build is Gradle based, with build.gradle, settings.gradle, the gradlew wrappers and lombok.config, which marks the codebase as Java rather than as a shell or Electron wrapper around something else. On the trust side the repository carries LICENSE.md with Apache-2.0, plus SECURITY.md, CONTRIBUTING.md and CODE_OF_CONDUCT.md, and per protocol documentation lives at docs.xpipe.io with separate installation and managed installation pages. The desktop installers are described as the easiest entry point on Windows and carry an optional automatic update. The project states plainly that this is a desktop application for a local workstation and not something to run on a server or in a container.
Editorial conclusion
XPipe fits administrators who already have working SSH and container tooling on their machines and want one catalog across many hosts, because it inherits the behaviour of those tools instead of replacing them. It does not fit anyone who wants a server-side component to install once, a hosted control plane, or a single place where remote credentials are stored, since the remote side stays untouched and secrets are delegated to a password manager. Before adopting it, confirm that the CLI programs it drives exist with matching behaviour on every host you plan to add, and decide what you are willing to operate yourself: a self-hosted git repository for vault sync, an opt-in MCP server that exposes the hub to an agent, and sudo elevation granted in place to a live session.
Frequently asked questions
what is xpipe software
XPipe is a connection hub for accessing server infrastructure from a local desktop. It is a Java desktop application that works on top of installed command-line programs such as SSH and docker, adds no setup on remote systems, and is documented at docs.xpipe.io.
is xpipe safe
The project states that all data is stored on your systems in a cryptographically secure vault, that no servers are involved, and that it does not send personal or sensitive information to outside services. Secrets are retrieved from your installed password manager rather than stored by XPipe, and a custom master passphrase can add further encryption. The repository also carries a SECURITY.md file.
what does x pipe do
As software, XPipe lets you establish and manage connections to remote systems from one hub, organize them in hierarchical categories, launch terminals that fill password prompts for you, browse and transfer remote files with locally installed programs, and tunnel or start services. Remote desktop applications run over RDP, VNC and X11 forwards.
how to install x pipe
For XPipe the project points at the installation docs at docs.xpipe.io/guide/installation and separate managed installation docs. Installers are described as the easiest route on Windows and come with optional automatic update. It is a desktop application meant for a local workstation, not for a server or container.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/xpipe-io-xpipe)Star history chart for your README
[](https://hysenlabs.com/projects/xpipe-io-xpipe)Was this useful?