nodejs/Release: the schedule that decides when your Node.js version stops getting fixes
Node.js Release Working Group
At a glance
- What is it?
- This repository holds no Node.js code. It holds the release schedule, the phase rules and the working group structure that decide how long a version keeps receiving patches, and it is the file to read before you pin a runtime.
- Who is it for?
- Adopt this repository as the source of truth for upgrade planning if you run production services on a Node.js release line. Skip it if you only need an interpreter, since it carries no package, no binary and no install command, and a version manager or an official container tag is the better tool.
- Can I use it commercially?
- Not without permission. GitHub finds no licence file in the repository, and without a licence all rights are reserved by default: you may read the code but not reuse it. Check the README, or ask the authors, before using it.
- Is it still maintained?
- Yes. The repository last received commits 13 days ago.
- What is it written in?
- Mainly JavaScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 14, 2026, and from our analysis. They are not legal advice.
Star history
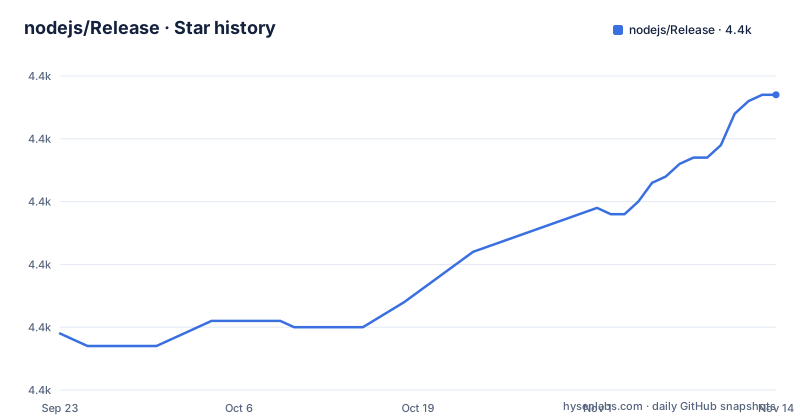
- nodejs/Release4,397 ★ · +38
| Repository | 2026-09-23 | 2026-11-14 |
|---|---|---|
| nodejs/Release | 4.4k | 4.4k |
38 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
A governance repository that ships no code
Cloning nodejs/Release gets you documents, not a package. The top level is .editorconfig, CODENAMES.md, CODE_OF_CONDUCT.md, CONTRIBUTING.md, GOVERNANCE.md, README.md, a doc/ directory, one script, and two schedule artifacts: schedule.json and schedule.svg. There is no package.json, no build step and no install command anywhere in the repository, so there is nothing to add to your dependencies. The working group itself is described as the Node.js Release Working Group, and its stated purpose is management and execution of the release and support process for all releases.
That makes the repository a control document. When a platform team asks whether an upgrade window is safe, the answer is a row in a table plus a phase definition. When a vendor asks for support on an old runtime, the same table gives the end-of-life date that ends the conversation. The repository was last pushed on 2026-11-02 and is not archived, so the schedule is still being touched, but the git history tells you when, not whether a date moved.
Three phases and the odd-numbered trap
The README lists four phases: Alpha, Current, Active Long Term Support, and Maintenance; Alpha applies from Node.js 27 onward, and Maintenance only to release lines up to Node.js 26. Current is where most non-breaking changes landing on the nodejs/node main branch get incorporated. Active LTS is where the Release team has audited new features and bug fixes and judged them stable for that line. Maintenance is narrower: critical bug fixes and security updates, with new features only at the Release team's discretion and typically only where the feature supports migration to a later line.
The trap is the version parity rule for release lines up to and including Node.js 26: odd-numbered lines were not promoted to LTS. Starting with Node.js 27, every release line is promoted to LTS. Their dates look abrupt in the end-of-life table: 23.x shipped on 2024-10-15, entered maintenance on 2025-04-01 and went end-of-life on 2025-06-01. 25.x shipped 2025-10-15, entered maintenance 2026-04-01 and ended 2026-06-01. Six months of security fixes, no migration runway. Odd numbers are the release line to watch if you deploy without a defined upgrade date.
Reading the table instead of installing anything
There is no install step here, and the repository does not point to a package registry for one. What you take away is a read, not a dependency. Start with schedule.json, which the README names as the machine-readable form of the release schedule, then check schedule.svg if you want the same information as an image. GOVERNANCE.md holds the process the TSC follows to approve additions to the releasers team, the team entrusted with the secrets and CI access needed to build and sign releases.
For an on-call decision, the four columns that matter are Initial Release, Active LTS Start, Maintenance Start and End-of-life. Read them in that order for your own line. If your version is before Active LTS Start, it is Current and you are inside the window where new features still land. If it sits between Active LTS Start and Maintenance Start, you are on the audited line. Past Maintenance Start, only security and critical fixes arrive.
The twelve-month claim the dates do not quite match
For lines up to Node.js 26 the table shows roughly a year in Active LTS before Maintenance; starting with Node.js 27, release lines stay in Active LTS for the whole 30 months of Long Term Support. The table does not hit 12 months exactly. 22.x entered Active LTS on 2024-10-29 and moved to Maintenance on 2025-10-21, which is 11 months and 22 days, not 12. 24.x entered Active LTS on 2025-10-28 and entered Maintenance on 2026-10-20, again a few days short of a full year.
The discrepancy is small. A date you plan a migration around is therefore a target, not a contract. The table itself says dates are subject to change, and 16.x shows the exception in practice, moving to end-of-life on 2023-09-11 rather than the April 30 date that the 14.x and 18.x rows use.
semver-major changes that arrive inside a patch stream
A release schedule that promises only minor changes has to have an exception, and this one names it. Changes required for critical security and bug fixes may lead to semver-major changes landing within a release stream. The README is careful about the shape of that exception: such situations will be rare, and they will land as semver-minor. A breaking change that ships under a minor bump is a hazard for tooling that pins a minor version and assumes forward compatibility inside a line.
The mitigation the README specifies is procedural rather than technical. Those changes should have a revert option included. So the failure mode is not hidden, but detection is manual: the schedule artifact carries dates rather than changelogs. Teams that auto-upgrade inside a maintenance line are the ones exposed.
Backports are a policy decision, not a merge queue
The working group lists managing the Alpha, Current and LTS branches, including backporting changes to those branches, and defining the policy for what gets backported, as two separate responsibilities. That split is the interesting part. Merging a fix into main is straightforward; deciding that the fix belongs on older release lines is the Release team's judgment, and the repository is where that policy is recorded rather than where it is applied.
Work is split across three teams: Releasers, Backporters, and CITGM, the Canary in the Gold Mine team. Membership in the working group does not put you on a team, and only the Releasers team holds the secrets and CI access required to build and sign. Additions to the releasers team must be approved by the TSC following the process outlined in GOVERNANCE.md.
Where nvm, Docker tags and the JSON file differ
For an individual machine, nvm or a version manager resolves versions from the published release list, which is convenient and gives you no policy. Container images tagged node:22 or node:22-alpine give you a moving target inside a line, so the tag alone will not tell you whether a security fix has landed. This repository gives the opposite: the policy with no mechanism. It will not install anything, hold an artifact, or tell you which patch level fixed a CVE.
The real difference in approach is between a resolvable version list and a governance record. A version manager answers which builds exist. nodejs/Release answers which line deserves your maintenance attention and when it will stop receiving security updates, and it names who signs, who backports and who tests. Teams that need both use schedule.json for the upgrade calendar and a version manager for the actual interpreter.
Editorial conclusion
Adopt this repository as the source of truth for upgrade planning if you run production services on a Node.js release line. Skip it if you only need an interpreter, since it carries no package, no binary and no install command, and a version manager or an official container tag is the better tool. Do not skip it if you deploy odd-numbered lines, because 25.x went end-of-life on 2026-06-01 though starting with Node.js 27 every release line is promoted to LTS. Verify first that schedule.json still matches the line you run: the table marks its dates as subject to change, and 22.x moved from Active LTS on 2024-10-29 to Maintenance on 2025-10-21, slightly under a year.
Frequently asked questions
How do I check whether my Node.js version is still supported?
Compare the major version you run against the release table in this repository. A line is supported while it is not End-of-Life; the 22.x row lists 2027-04-30 as its end-of-life date and 24.x lists 2028-04-30.
Why does an odd Node.js version like 25.x never become LTS?
Up to and including Node.js 26, odd-numbered release lines were not promoted to LTS and did not go through the Active LTS or Maintenance phases; starting with Node.js 27, every release line is promoted to LTS. 25.x shipped on 2025-10-15 and reached end-of-life on 2026-06-01.
What is the difference between Current, Active LTS and Maintenance in Node.js?
Current incorporates most non-major changes from the nodejs/node main branch. Active LTS covers changes the Release team has audited as appropriate and stable, while Maintenance is limited to critical bug fixes and security updates.
How long does an even Node.js release stay in Active LTS?
For lines up to Node.js 26 the table shows slightly under a year in Active LTS, for example 22.x from 2024-10-29 to 2025-10-21. Starting with Node.js 27, release lines stay in Active LTS for the whole 30 months of Long Term Support. The table notes that dates are subject to change.
Does nodejs/Release contain Node.js source code or a package to install?
It contains documents and schedule artifacts, including schedule.json and schedule.svg, plus GOVERNANCE.md and a release plan generator. There is no install command, so nothing is added to your dependencies.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/nodejs-release)Star history chart for your README
[](https://hysenlabs.com/projects/nodejs-release)Was this useful?