pgAdmin's Makefile reads the version by grepping Python source, and its dependencies branch on Python 3.9
pgAdmin is the most popular and feature rich Open Source administration and development platform for PostgreSQL, the most advanced Open Source database in the world.
At a glance
- What is it?
- pgAdmin 4 is a Flask and React administration tool for PostgreSQL that can run on a web server or standalone through an Electron runtime. Its build files are the interesting part: the Makefile extracts the version from two Python files, the requirements file carries two dependency sets because one interpreter version is still supported, and several pins exist for reasons written in comments.
- Who is it for?
- pgAdmin 4 is the right tool if you administer PostgreSQL and want a browser interface with a desktop option, and the code is candid in the places where it matters. Three things to know before you build or package it.
- Can I use it commercially?
- Check first. The repository uses a licence we do not classify automatically, so read its LICENSE file before any commercial use.
- Is it still maintained?
- Yes. The repository last received commits 2 days ago.
- What is it written in?
- Mainly Python, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
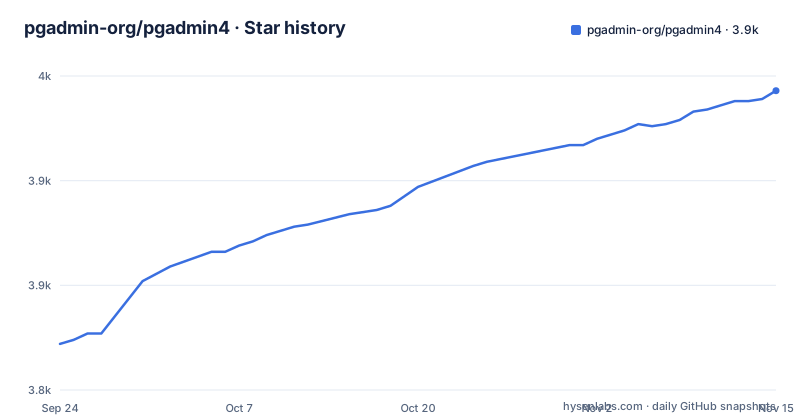
- pgadmin-org/pgadmin43,943 ★ · +121
| Repository | 2026-09-24 | 2026-11-15 |
|---|---|---|
| pgadmin-org/pgadmin4 | 3.8k | 3.9k |
121 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The Makefile reads the version by grepping Python source
Three variables at the top of the build file are computed by shelling out and parsing text:
APP_NAME := $(shell grep ^APP_NAME web/branding.py | awk -F"=" '{print $$NF}' | tr -d '[:space:]' | tr -d "'" | awk '{print tolower($$0)}')
APP_RELEASE := $(shell grep ^APP_RELEASE web/version.py | awk -F"=" '{print $$NF}' | tr -d '[:space:]')
APP_REVISION := $(shell grep ^APP_REVISION web/version.py | awk -F"=" '{print $$NF}' | tr -d '[:space:]')
The application name is read out of a branding file by grepping for a line, splitting on the equals sign, stripping whitespace and single quotes with a stream editor, then lowercasing the result. The release and revision numbers come from a version file the same way, without the lowercasing. So the build's idea of what version it is depends on a specific formatting convention in the Python sources, and a stray space or a changed quoting style would silently produce a different package name. It is an old technique and it works, but it is the kind of coupling that a manifest would have made impossible. The rest of the file is more conventional: a default target that builds the platform independent outputs, and a set of targets that all change into the web directory and run the JavaScript toolchain.
Two dependency sets, because one Python version is still supported
The requirements file declares that Python 3.9 and later are supported, and several libraries are pinned twice with an environment marker on each line. One authentication library is on one series for 3.9 and a later series for everything above it. The AWS library is pinned to two different minor series the same way, as are the form library, the OAuth helper and the login framework. The pattern is consistent and deliberate, and it has a cost: a packaging change now has to be reasoned about twice, and a security patch that lands in the newer series has to be checked against the older one before it can be called fixed. The file's own header explains the housekeeping rule that goes with it: packages are sorted alphabetically, exceptions are allowed to preserve dependency order with a comment, and any change to runtime or build dependencies obliges the committer to tell the distribution package maintainers.
One pin exists because an earlier version refused all logins
Three comments in the requirements file explain pins that would otherwise look arbitrary, and the most valuable one documents a bug. The login framework is held at a fixed series for newer interpreters because a specific release in that series corrected an inverted lock-status check, and the model code follows the corrected semantics, so anything earlier in the same series would refuse all logins. That is a security-adjacent library being pinned to a version because the earlier one had the sign the wrong way round, and the comment names the file that depends on it. Another comment explains a floor and a ceiling on an Azure management package, kept deliberately narrow because a command line tool commonly present on Linux distributions pins a lower version, with a reference to the issue where the conflict was tracked. A third explains the alphabetical rule with its exception.
The desktop runtime forks a Python server and cannot run setup for you
The application has two shapes. In server mode it is a web application on a web server, reached through a browser. In desktop mode it is a workstation application built on an embedded runtime that forks a Python server process and displays the interface, so the same server code serves both. That shared process has a consequence for installation, and the README states it: the initial setup of the configuration database is interactive in server mode and non-interactive in desktop mode. You can run the setup script by hand, or let it happen when you start the application. Running the runtime will do it for you automatically in desktop mode, but that will not work in server mode, because the runtime does not allow command line interaction with the setup program. In other words, the path of least resistance breaks on exactly the deployment where the interactive step is required.
The documented development config ships credentials
The configuration walkthrough tells you to copy the sample configuration into a local override file, and the sample is a working one. It points the data directory at a user path, pins the server to the loopback address and a non-default port, and sets a mode switch that toggles between the two shapes above. It also contains a database connection string with a username and a password inline and a port that does not match the default, and a mail block with a real mail provider's host, a port configured for implicit encryption, a username placeholder and a password placeholder. Nothing here leaks a secret, since every value is a placeholder or a well-known local default, and the port and address are the two that would need attention if the example were copied to a server. The example is the most likely file in a contributor's first commit to end up in a public deployment.
The JavaScript audit is narrowed, and the reason is in a comment
The build file has two audit targets for the JavaScript side, and one of them is a shortened version of the other. The comment above explains why: auditing everything pulled in a vulnerability from a package used only to decompress archives, so the original command is commented out and replaced with one that audits only the dependencies group, with a link to the advisory and a note that a fix was sent to the upstream project as a pull request. So the project's dependency scanning is scoped to what ships, not to what it builds with, and the reason is recorded rather than quietly resolved. There is a matching audit target for the Python side, and a check target that installs the node packages, bundles, runs the linter, checks style, runs the JavaScript tests once and then runs the regression suite.
The container build deletes its own lock file and disables an optimisation
The image's first stage builds the front end and then tidies up after itself. It installs the build toolchain, copies the web sources in, and runs the bundle step inside a command that mounts the git directory read-only, mounts the dependency directory as an in-memory filesystem, and mounts the generated asset cache the same way. Before building it sets a compile flag that disables an ARM instruction set optimisation for image handling, which is a workaround rather than an optimisation. After bundling it deletes the lock file, the package manifest, every dotfile, and the bundler, babel and test configuration. Inside a throwaway stage that is fine, and the stage does then start again from a pinned Python base image. The first stage is built from a moving Alpine tag, though, while the second pins its Python version, which is an asymmetry in a file that otherwise tries hard to be reproducible.
A database driver is compiled, so PostgreSQL's binaries must be on the path
The Python setup instructions have one step that is easy to skip and hard to debug. Before installing the requirements, the PostgreSQL installation's binary directory has to be on the path, because the build looks for a configuration program from that installation in order to compile a database driver. If it is missing, the failure appears during a compile step with a message about a header or a library rather than about a path, which is a bad way to learn that the problem is your path. Two other steps in the same section are equally practical: a recent installer for the package tool is required, because some of the components ask for a very recent version, and running the regression suite needs a second requirements file from a subdirectory. The Windows path is delegated to a separate document, with the README calling it more complicated. One more piece of the setup is worth knowing before you start: the database migration workflow runs through the same application entry point, with the entry file named in an environment variable so the command line tool picks up the right application, and it is run from the web directory. So a contributor changing the bundled SQLite schema adds a migration file with a command rather than by hand, and the same command is what a release has to remember.
Editorial conclusion
pgAdmin 4 is the right tool if you administer PostgreSQL and want a browser interface with a desktop option, and the code is candid in the places where it matters. Three things to know before you build or package it. The build expects the PostgreSQL installation's binaries on your path, because a driver is compiled rather than installed as a wheel. One dependency pin exists because an earlier release refused every login, which tells you how carefully those comments are maintained. And the JavaScript audit is deliberately narrowed to production dependencies, with the reason and an unmerged upstream fix recorded in the build file.
Frequently asked questions
What is PGAdmin4?
A rewrite of the earlier pgAdmin3 management tool for PostgreSQL: a Flask web application with a React client. It can be deployed on a web server and reached through a browser, or run standalone on a workstation through an embedded runtime that forks a Python server process.
how to install pgadmin4
From source, with Node.js 20 or newer, yarn, Python 3.9 or newer and a PostgreSQL server as prerequisites. The README then covers enabling corepack, building the asset bundle, creating a virtual environment with a recent pip, writing a local config file, and running either the setup script or the application itself.
how to access pgadmin4 in browser
Start it from the command line in either server or desktop mode. The README says the URL is shown in the terminal once the application has started up.
Is pgAdmin the same as PostgreSQL?
No. The README describes pgAdmin 4 as a rewrite of the earlier pgAdmin3 tool, built with Python on the server and a React client on the front, and PostgreSQL is the database it administers.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/pgadmin-org-pgadmin4)Star history chart for your README
[](https://hysenlabs.com/projects/pgadmin-org-pgadmin4)Was this useful?