Rancher: a management plane you bootstrap with --privileged, and a pinned Kubernetes
Complete container management platform. Rancher makes it easy to run Kubernetes everywhere, meet IT requirements, and empower DevOps teams.
At a glance
- What is it?
- Rancher is a container management platform for organisations running Kubernetes in production. Its module file is more revealing than its README: every Kubernetes library is pinned to exactly one version, and four upstream projects are consumed as Rancher forks, which tells you both how tightly the release is coupled and where security updates will have to be forward-ported by hand.
- Who is it for?
- Rancher suits an organisation already running Kubernetes in production across several clusters that needs one place to see and manage them, and that can accept a component that requests root and full container privileges to bootstrap itself. It is a poor fit as a desktop Docker replacement, which is a separate product, and a poor fit if you cannot take on the release coupling that comes with every Kubernetes library pinned to one version.
- Can I use it commercially?
- Yes. Apache-2.0 is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository received new commits within the last day.
- What is it written in?
- Mainly Go, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
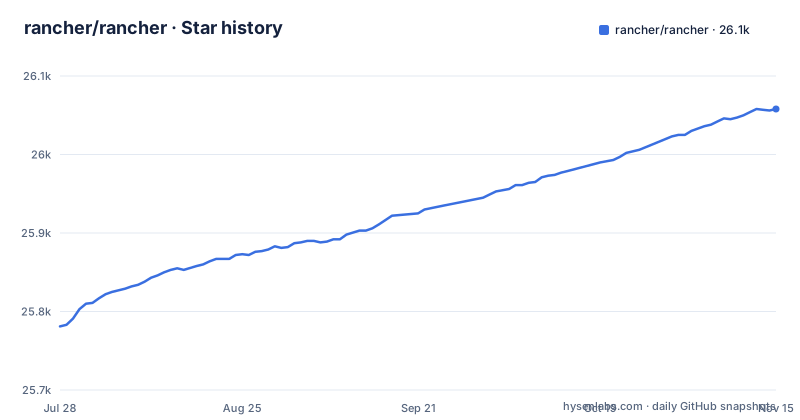
- rancher/rancher26,058 ★ · +277
| Repository | 2026-07-28 | 2026-11-15 |
|---|---|---|
| rancher/rancher | 25.8k | 26.1k |
277 Stars in the last 110 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The quick start asks for root and full container privileges
The entire bootstrap is one command, and it is worth reading carefully before running it on a machine that matters:
sudo docker run -d --restart=unless-stopped -p 80:80 -p 443:443 --privileged rancher/rancherThen you open a browser to `https://localhost`.
Two flags in that line deserve attention. It runs under `sudo`, so the container is not confined to your user. And it passes `--privileged`, which grants the container far more capability than a normal container gets, including access to host devices.
For a component whose job is to manage other clusters, some level of host access is inherent to the design, so this is not surprising in isolation. But it does mean the documented first step is a privileged process, and it is the step an operator tends to run early, on whatever machine is to hand, before reading further.
Two other details are practical rather than alarming. The container restarts unless stopped, so it survives a reboot, and both port 80 and 443 are published, which is why the browser URL is HTTPS rather than HTTP.
The README itself does not discuss the privilege requirement. If that is a concern, the installation documentation linked from the same page covers the other options, including the Helm chart directory in this repository.
Every Kubernetes library is pinned to exactly one version
The module file contains a large block of replace directives, and almost all of them point Kubernetes libraries at the same version. The API types, apimachinery, apiserver, client library, cloud provider, cluster bootstrap and component-base packages, among others, are each forced to `v0.37.1`.
That is a deliberate coupling. Kubernetes client libraries drift out of step with each other easily, and a management platform that talks to many of them at once will produce subtle behaviour differences if they are allowed to float independently. Pinning everything to one version removes that class of problem.
The cost is on the other side. Because the whole set is pinned together, moving to a new Kubernetes version is a single coordinated change rather than something you can adopt incrementally, and the pin lives in the source rather than in a configuration file you can adjust per deployment. A fork or a downstream build that needs a different Kubernetes version is editing this file.
There are also local replaces for three of the project's own subpackages, the API types, the generated client and the plan types, each pointed at a directory in the repository. So a piece of the tree is consumed as a module without being published first, which is the normal arrangement for a monorepo but does mean a partial checkout will not build.
Five upstream projects are consumed as Rancher forks
The same replace block is where the maintenance burden becomes visible. Four dependencies are not used as published; they point at Rancher's own forks.
The SAML library is one, replaced with a Rancher build. The Docker distribution library is also replaced, but to upstream docker/distribution v2.8.2, with a comment explaining that rancher-machine requires a replace to be set. Knative's shared package is forked too. A mocking library and a test-management client are also pointed at Rancher copies.
Every one of these is an upstream project that will eventually publish a release. Because a replace directive wins over the published version, Rancher is not picking those up automatically, and neither is anyone who builds this. Security fixes in the SAML library or in the Knative helpers have to be noticed and forward-ported by hand.
That is the ordinary cost of forking, and it is a normal thing for a vendor to do. What makes it worth noting is that it is visible in one file rather than hidden, so you can enumerate exactly which upstream projects you are now tracking. If any of those four matters to your security posture, you now have a line item for it.
The module also requires a recent Go toolchain, declared as 1.27.3, so building from source has its own floor.
Every make target, including the default one, runs inside a container
The Makefile is small and unusual. Its list of targets is not written out; it is generated by listing a directory and filtering one entry out. Anything in the scripts directory becomes a make target, minus the container-run script itself, and each target runs that script with the target name as its argument. A second list does the same over a development scripts directory, but runs each script directly rather than through the container-run script.
The default goal is the continuous integration target. So running make with no arguments, which is what most people do first, goes straight into a container.
There are convenience targets that delegate to a shared quick target with a different value: one for the agent component, one for the server, one for a binary server build, and one for building the k3s images. Those are the components a developer works on day to day.
The consequence is that the build requires a working container runtime before anything else can happen, and that the set of available targets is defined by what files exist on disk rather than by anything readable in the Makefile. A contributor reading the file cannot enumerate what they can build, and a change that adds a script silently adds a target.
That is a reasonable trade for a project of this size, where the alternative is a very long Makefile, but it is worth knowing before you start.
Integration tests need a live server and run one at a time
There are two integration targets, and reading them tells you what the test suite actually requires.
The first, the setup target, builds a setup binary from a subdirectory by running its build script, then executes that binary with a test configuration file pointed at a path in the repository. The comment says it builds the integration setup without starting a container, and the configuration it generates is what the second target consumes.
The second target runs the tests against an already-running Rancher server. Its requirements are spelled out in a comment: the test configuration environment variable must point at a valid config file, or you run the setup target first to generate one. The command itself sets that variable, disables CGO, and runs the test suite verbosely with a flag to stop on the first failure, a 30 minute timeout, and a parallelism setting of one.
That last flag is the notable one. Parallelism of one means the tests run serially, which combined with a 30 minute ceiling describes a suite that is long by design rather than broken. It also means integration testing is not something you do casually on every save.
The practical requirement is the live server. These are not unit tests that spin up their own environment; something has to be running for them to talk to.
Part of the README is generated, and the stable tag moves under you
The stable release section contains an inline comment instructing that the line not be removed, which is the kind of thing you only see in a file partly written by a script. The release it names is v2.15.3, and it gives two image references for it: a fully qualified version tag and a moving stable tag.
That distinction matters. If you deploy the stable tag, you are not pinning anything, and a future pull will move you to a different version without any change on your side. If you deploy the versioned tag, you know exactly what you have and can plan the upgrade. For a management plane, the second is the defensible default.
Release channels are maintained in a file at the top of the repository rather than being implicit, which is a better arrangement than most projects manage, and there is a documentation directory covering how to customise building and packaging if you need to.
The support matrix is handled with a similar piece of care and a similar trap. The README points at a support matrix URL and warns that the link defaults to the matrix for the latest version of Rancher, and that you should use the left navigation to select a different version. So the page you land on describes the newest release, not the one you are running.
Recent releases include v2.15.3, v2.14.7 and v2.13.11, all on the same day in October 2026, and the last push to the main branch was on 2026-11-02.
This is a packaging meta-repo, and the rest of the code is elsewhere
The README describes this repository as a meta-repo used for packaging that contains the majority of the Rancher codebase, and directs you to the module file for the full list of other Rancher projects and modules. It repeats the point about the other open source libraries and projects the build includes, again pointing at the same file.
So the boundary is explicit. Some Rancher components live in their own repositories, and this one assembles the release. If you are looking for a specific subsystem and cannot find it here, the answer is probably that it has moved.
The top-level layout is consistent with a release engineering repository. There is a runtime Dockerfile separate from the build, a build configuration file, a Helm chart directory, a main entry point, a module file and a generator file, and separate directories for internal packages, public packages, commands, hack scripts and dev scripts. A cleanup directory suggests there is deliberate machinery for removing build artefacts.
Two files describe concerns outside the code itself. There is a keybase document and an RPM signing key file, which is what you would expect from a project that distributes signed RPM packages. And there is an update directory for update automation, alongside a linting configuration and a Go module file, which is the standard set of maintenance tooling.
Editorial conclusion
Rancher suits an organisation already running Kubernetes in production across several clusters that needs one place to see and manage them, and that can accept a component that requests root and full container privileges to bootstrap itself. It is a poor fit as a desktop Docker replacement, which is a separate product, and a poor fit if you cannot take on the release coupling that comes with every Kubernetes library pinned to one version. Before deploying, check three things: which version the moving stable tag currently points at and whether you should pin v2.15.3 instead, which of the four forked dependencies you are now responsible for tracking, and what your own support matrix looks like, since the project's defaults to the latest release.
Frequently asked questions
What is rancher vs Kubernetes?
Kubernetes is the container orchestrator; Rancher is a management layer on top of it. The README describes Rancher as an open source container management platform built for organizations that deploy containers in production, whose purpose is to make it easy to run Kubernetes everywhere, meet IT requirements and empower DevOps teams. You still run Kubernetes; Rancher sits above it so several clusters can be seen and managed from one place.
how to install rancher
The README's quick start is a single command: `sudo docker run -d --restart=unless-stopped -p 80:80 -p 443:443 --privileged rancher/rancher`, after which you open a browser to https://localhost. Note that it runs as root and passes the privileged flag. The README also points to an installation and upgrade guide for all other options, and the repository contains a Helm chart directory.
how to use rancher
The README does not document usage, it links to the Rancher documentation for that. What it does tell you about the running system is that after the quick start you open a browser to https://localhost, since ports 80 and 443 are published and the container is set to restart unless stopped. Operating system requirements are version-specific and are listed in a support matrix that defaults to the latest Rancher version rather than the one you are running.
how to use rancher kubernetes
The README frames Rancher as a way to run Kubernetes everywhere and to meet IT requirements and empower DevOps teams, so its Kubernetes relationship is the central one rather than a separate feature. The module file shows the coupling, with every Kubernetes library pinned by a replace directive to the same version, v0.37.1, so the client libraries cannot drift apart. Usage detail is in the linked documentation rather than the README.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/rancher-rancher)Star history chart for your README
[](https://hysenlabs.com/projects/rancher-rancher)Was this useful?