angular-realworld-example-app: the default e2e run skips every security test
Exemplary real world application built with Angular
At a glance
- What is it?
- An Angular implementation of the RealWorld spec, a social blogging application backed by a real API, used as a reference implementation. Two things in the package manifest are worth reading before anything else: the releases are named with incrementing build numbers rather than versions, and the default end to end command explicitly excludes every test tagged as a security test.
- Who is it for?
- This app suits someone evaluating Angular against a spec rather than a tutorial, because the routing, forms, state and API layers are all present and follow the published style guide. Two things to know first.
- Can I use it commercially?
- Check first. The repository uses a licence we do not classify automatically, so read its LICENSE file before any commercial use.
- Is it still maintained?
- Yes. The repository last received commits 13 days ago.
- What is it written in?
- Mainly TypeScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
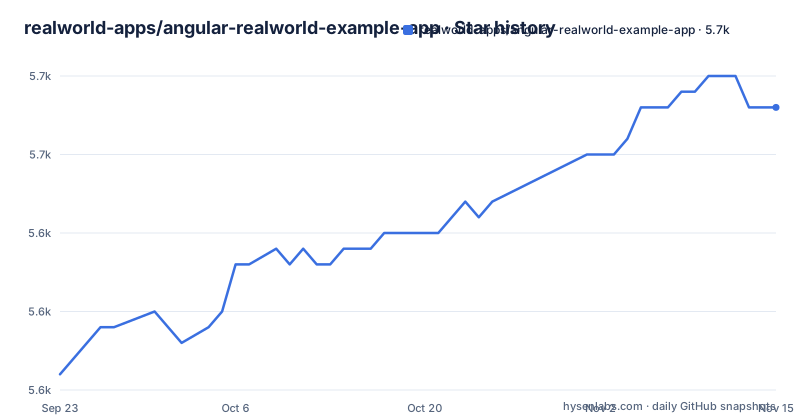
- realworld-apps/angular-realworld-example-app5,653 ★ · +17
| Repository | 2026-09-23 | 2026-11-15 |
|---|---|---|
| realworld-apps/angular-realworld-example-app | 5.6k | 5.7k |
17 Stars in the last 53 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The releases are build numbers, and the package version is zero
The release history does not contain version numbers. The three visible tags are build-52, build-53 and build-54, all dated 2026-11-02, which is the naming convention of an automated build rather than a release. Two builds minutes apart that morning and a third that evening is the shape of a continuous integration job that tags on success. Meanwhile the package manifest declares a version of 0.0.0 and marks the package private, so nothing here is published to a registry either. The last commit to the default branch, on 2026-11-02, landed seconds after build-53 was tagged, which is the ordinary consequence of that setup: there is a stream of deployable artefacts and no release train. For anyone trying to work out what a given commit corresponds to in terms of a shipped build, the answer is the tag that follows it, not a version number in the manifest.
Security tests exist and the default run inverts their tag
The test scripts are unusually explicit about one thing. The default end to end command passes a flag that inverts a tag filter for tests labelled as security tests, and there is a separate script that runs only those, plus variants for a user interface mode, a headed mode, a debug mode, and one that opens a stored report. There is also a script whose entire body is printing a file listing disabled tests, which means known failures are enumerated in a document rather than left as mysterious skips. So the suite is partitioned by intent, and a developer running the default command gets a green result that explicitly says nothing about the security partition. That is a reasonable design for keeping the main suite fast, and a trap for anyone reading a passing pipeline as evidence the application is free of injection or authentication problems.
The build calls the Angular CLI while a Vite plugin sits in dev dependencies
The start and build scripts are the standard command line invocations for the framework, serving and building through the CLI. But the dev dependencies include a Vite plugin built for Angular, and the repository root carries a vitest.config.ts next to angular.json. The manifest also lists two reactive libraries for Angular at matching versions. For a reference application, the build path matters more than usual, because it is the part most likely to be copied wholesale into another project.
Framework packages are pinned exactly, everything else is ranged
The dependency list has a visible seam. Every core framework package carries a fixed version with no range operator, and the compiler package matches, while the reactive libraries are also fixed. Everything that is not the framework uses a caret range instead, including the reactive library's own peers, the markdown renderer, the reactive streams library, the type definitions for the markdown renderer, and the test tooling. The practical effect is that installing the application resolves the framework to one known patch level and lets the rest float, which is a defensible split: framework minor releases carry migration risk, while a markdown renderer does not. One number in that list is worth a second look, though. The markdown renderer is on a version in the teens while the type definitions for it are on a major version in the single digits, so the types are not tracking the runtime and anything typechecked against them may be describing a much older surface.
The backend is a submodule, and the toolchain is Bun
Getting started is three commands and the first one has a requirement stated above it: Bun, with a link to its own installation documentation.
git clone https://github.com/realworld-apps/angular-realworld-example-app.git
cd angular-realworld-example-app
bun run setup  # Init submodules + install dependencies
bun run start
The setup script initialises the submodules and installs dependencies with the package manager of that runtime. The submodule is the realworld directory, and the README says the application uses a custom API for all requests. The readme then adds an instruction that catches people out: run the setup command again after any pull that updates the submodule. So there is a class of change that leaves you with stale backend code and no error, and the only signal is the reminder in the readme. The formatting script makes the same point in code, excluding the submodule directory from the set of files it rewrites, which is the same decision expressed as an exclusion pattern.
Tokens are stored where a script can read them, and the readme says so
The authentication section is short and honest about its own trade-off. Sign in and sign up use JSON web tokens, and the token is stored in local storage, with a note that authentication can be easily switched to session and cookie based. That is an unusually clear statement of the weakness, because storing a bearer token in local storage makes it readable by any script running on the page and it survives a tab close, which is precisely the case the application demonstrates when it renders markdown that came from the server on the client. Rendering that content on the client is the other decision that shape of the app implies, and for a reference implementation it is a feature rather than an oversight. The rest of the page breakdown follows the spec closely: an article page with a delete button visible only to the author, a comments section with the same rule, a profile page with two variants, and a settings page. Nothing here is unusual, which is the point of a reference implementation.
The readme opens with an empty heading and points elsewhere for real work
The first line of the readme is a markdown heading with nothing after it. Below that the description is the normal one for this family of applications, and the functionality overview is presented as a list of create, read, update and delete operations on users, articles and comments, with a note that deleting a user is not required by the spec, and the same kind of note attached to updating a comment. The last substantive section is the most useful paragraph in the file. It says the project may be too simple for getting a good understanding of the different ways an Angular project can be built, and points to a separate organisation focused on Angular development for a comprehensive understanding of how more complex projects are implemented, naming the person who manages it. The licensing section is split the same way, with project code under one licence and the framework logo called out as a trademark of the company that owns it.
Editorial conclusion
This app suits someone evaluating Angular against a spec rather than a tutorial, because the routing, forms, state and API layers are all present and follow the published style guide. Two things to know first. The default end to end command excludes every test tagged as a security test, so a green run does not mean those passed; they are a separate invocation. And the build commands are the Angular CLI while the dev dependencies include a Vite plugin for Angular. A team wanting a production application should treat this as a reference, since the readme itself says it is too simple and points elsewhere for serious work.
Frequently asked questions
What is the Angular RealWorld example app?
It is an exemplary application built with Angular that adheres to the RealWorld specification and API, demonstrating CRUD operations, authentication, routing and pagination against an actual backend server rather than a mock. The application itself is a social blogging site called Conduit, described as a Medium clone, and a live demo is available.
What do I need to run angular-realworld-example-app?
Bun is required. You clone the repository, change into the directory, run a setup script that initialises the submodules and installs dependencies, then run the start command. The realworld project is a git submodule, and the readme says to run the setup command again after any pull that updates that submodule. The declared Node engine requirement is 20.11.1 or newer.
How are tests run in angular-realworld-example-app?
Unit tests use vitest, with separate scripts for a user interface mode and coverage. End to end tests use Playwright, and the default script passes a flag that inverts a tag filter for tests labelled as security tests, so those are excluded from the default run and have their own script. There is also a script whose only action is printing a file that lists disabled tests.
How is authentication handled in the RealWorld Conduit app?
It uses JSON web tokens, with the token stored in local storage. The readme notes that authentication can be easily switched to session and cookie based.
Is angular-realworld-example-app meant for production use?
The readme says the project may be too simple for getting a good understanding of the different ways an Angular project can be built, and points to a separate Angular focused organisation for how more complex projects are implemented. The package is marked private with a version of 0.0.0, and the releases are named with build numbers rather than versions.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/realworld-apps-angular-realworld-example-app)Star history chart for your README
[](https://hysenlabs.com/projects/realworld-apps-angular-realworld-example-app)Was this useful?