Easy Watermark strips all EXIF, reserves its interface, and ships no crash reporter
Project brief: Securely, easily add a watermark to your sensitive photos. .
At a glance
- What is it?
- Easy Watermark is a Kotlin app for stamping photos you have to send, on Android, iOS and desktop. Its whole pitch is negative: no network, no analytics, no device identifiers, no crash reports, no tracking SDK. The price of that is a support channel that runs through an email address, and the licence covers the code while the interface design is explicitly reserved.
- Who is it for?
- Easy Watermark fits exactly the case it names, where an image has to travel somewhere it might be reused and where you would rather it carried no location data and no third-party SDK. Two things to weigh before installing.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 27 days ago.
- What is it written in?
- Mainly Kotlin, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 13, 2026, and from our analysis. They are not legal advice.
Star history
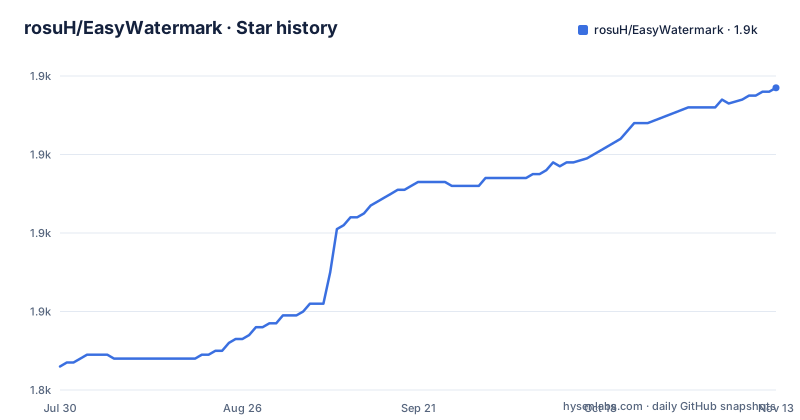
- rosuH/EasyWatermark1,917 ★ · +71
| Repository | 2026-07-30 | 2026-11-13 |
|---|---|---|
| rosuH/EasyWatermark | 1.8k | 1.9k |
71 Stars in the last 106 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The no-network claim has a support cost attached to it
The tagline is two words long and negative: no network, that is safer. The privacy section backs it up in specifics. The app collects no analytics, no device identifiers and no crash reports, and there is no third-party tracking SDK. The consequence is stated further down, in the open source section, and it is the part worth reading before you install. Because there is no crash reporter, bugs that cannot be reported in-app have to be mailed to an address at the author's domain. So the design choice is visible in two places at once: the user's privacy is protected by declining to collect the data that would make support easier, and the maintainer absorbs the difference. For an app whose stated use is identity documents and receipts, where a silent failure could mean a rejected upload, that trade is at least made deliberately and in public rather than hidden in a privacy policy.
Android 9 and below still needs storage access
The permission story splits by platform version, and the split is a consequence of the Android photo picker rather than of the app's design. On Android 10 and later, choosing a photo is the only permission the app needs, because the system picker hands over the single selected image without granting broad storage access. On Android 9 and below there is no such picker, so storage access is still required to read images and to save the watermarked result. That means the install experience differs by device age in a way the feature list does not hint at, and anyone writing a policy about which devices may run the app has to account for the older branch. The privacy policy itself is a document in the repository in two languages, English and Simplified Chinese, matching the two README files, so what is promised about data handling is readable without installing anything.
MIT covers the code, the interface stays with its designer
The open source section says the app is MIT licensed, and then the credit section immediately qualifies it. The interface was designed by someone else, credited by handle, and the page states that the user interface and related design assets remain his, asking that they not be reused without permission. That is a narrower grant than the licence line suggests, and it matters for anyone who reads MIT and assumes the whole repository is reusable. Third-party components are handled separately and correctly: Phosphor Icons glyphs are vendored as Compose vectors with the licence notice recorded in a separate third-party notices file, and three libraries are credited for what they do, an image loading library for the gallery and filmstrip thumbnails, Material Components for Android, and a colour picker view used for a custom colour dialog. So the repository has three licence layers rather than one, and only the first is MIT.
Four distribution channels and a package name worth checking
The download table is the part of the page that most deserves attention, because watermarking apps attract lookalike listings. Four channels are named and all four are described as developer-run: the App Store for iOS, Google Play as a paid edition that is the same code and supports ongoing development, GitHub Releases for the latest APK, and F-Droid for a free reproducible Android build. Then the warning: listings elsewhere are unofficial, and on Android you should check the package name, me.rosuh.easywatermark, before installing. Two of the four channels are paid or store gated, which is the honest way to fund a small privacy-first app, and the one channel that is both free and verifiable is the reproducible build, since that is the one where the binary can be checked against its own source. The store listing also carries a version history of its own, so a paid user and a F-Droid user can be on different builds at the same moment.
A test infrastructure far larger than the feature list
The repository root carries several test related modules that the feature list never mentions, and together they describe how seriously the visual side is taken. There is a base benchmarks module and a separate macrobenchmark module, so both micro and device level performance are measured. There are two screenshot comparison frameworks, one under a plain name and one suffixed for the target it serves, plus a parity shots module, which together suggest a habit of comparing rendered output rather than trusting it by eye. A colour module sits beside them, which is what a colour picker needs to be consistent across platforms. The multiplatform shape is visible too: separate application directories for Android, iOS and desktop over a shared module, a buildSrc directory, and a Gradle wrapper with both shell and batch launchers. Translations run through Weblate, and the language switch is a link at the top of the page rather than a setting buried in the app.
Three planning documents and two agent directories in the root
Several files in the root are working material rather than project infrastructure, and their presence tells you something about how the work is being done. There are three Markdown documents with working titles: a findings file, a progress file and a task plan. There is also a skills directory paired with a lock file, and two agent configuration directories alongside two agent instruction files at the root, one named for a specific tool. For a single developer app, that is a lot of scaffolding committed to version control, and it has a practical effect on anyone browsing the repository: the root is not a clean list of build files, and the documentation a newcomer reads first may be a progress note rather than a guide. None of it is harmful, and keeping plans in version control has real value for a solo maintainer, but it does mean the README is the only curated document in the top level.
Version 3.0.2 shipped three weeks before the last push
The recent releases are three in the first half of September 2026: 3.0.0 on 2026-09-04, 3.0.1 on 2026-09-12 and 3.0.2 on 2026-09-13. The default branch was then pushed to on 2026-10-03, which is roughly three weeks after the newest tag. So the current shape of the project is a 3.x line that shipped a major release and two patches inside ten days, followed by a quiet month of commits that have not been cut into a release. Anyone tracking this repository should treat 3.0.2 as the newest installable version and the branch as work in progress ahead of it. The version line also tells a small story about the project's shape: a third major version for an app whose feature list is six lines long suggests the changes were structural, most likely the move out of a single Android application into the shared multiplatform layout the root now shows.
Editorial conclusion
Easy Watermark fits exactly the case it names, where an image has to travel somewhere it might be reused and where you would rather it carried no location data and no third-party SDK. Two things to weigh before installing. The privacy design means there is no in-app crash reporting, so a fault on a platform version you need has to go through an email address, and that is a real cost when the app also ships a paid edition whose stated purpose is funding ongoing development. And the MIT licence covers the application code but not the interface design, which stays with its original author, so the licence is narrower than it first appears for anyone planning to reuse the app in a product of their own. If you want a build you can inspect and reproduce, the F-Droid channel is the one that offers both.
Frequently asked questions
What does Easy Watermark do with EXIF data in exported photos?
It strips all of it, including location. Export is JPEG or PNG, and the metadata removal happens at that point rather than at import.
Is Easy Watermark free to install?
It depends on the channel. The Google Play edition is paid and described as the same code supporting ongoing development, the F-Droid build is free and reproducible, and GitHub Releases carries the latest APK.
What permissions does Easy Watermark need on Android?
On Android 10 and later, choosing a photo through the system picker is the only permission required. Android 9 and below still need storage access in order to read images and save the result.
Can I reuse the Easy Watermark interface in my own project?
Not without asking. The app code is MIT licensed, but the interface design and related design assets remain with the designer who created them, and the page asks that they not be reused without permission.
Does Easy Watermark send anything to a server?
No. It collects no analytics, device identifiers or crash reports and has no third-party tracking SDK. One consequence is that bugs cannot be reported in-app, so they have to be mailed instead.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/rosuh-easywatermark)Star history chart for your README
[](https://hysenlabs.com/projects/rosuh-easywatermark)Was this useful?