Scrcpy GUI ships unsigned binaries and tells you to verify the checksum anyway
👻 A simple & beautiful GUI application for scrcpy.
At a glance
- What is it?
- SimonAKing/scrcpy-gui is an Electron desktop front end that discovers Android devices and launches the upstream scrcpy with a configured command line. The packaging is the interesting part: official scrcpy and adb are bundled and checksum-verified, the app itself is not signed, and the project tells you how to attest the download anyway.
- Who is it for?
- Scrcpy GUI suits a user who wants scrcpy's capabilities without memorising its flags, who wants several devices launched at once, and who would rather not configure a path to find the tools. It suits someone on macOS or Linux who would otherwise install a distribution package that lags behind, since the bundled runtime pins the version.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 4 days ago.
- What is it written in?
- Mainly TypeScript, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
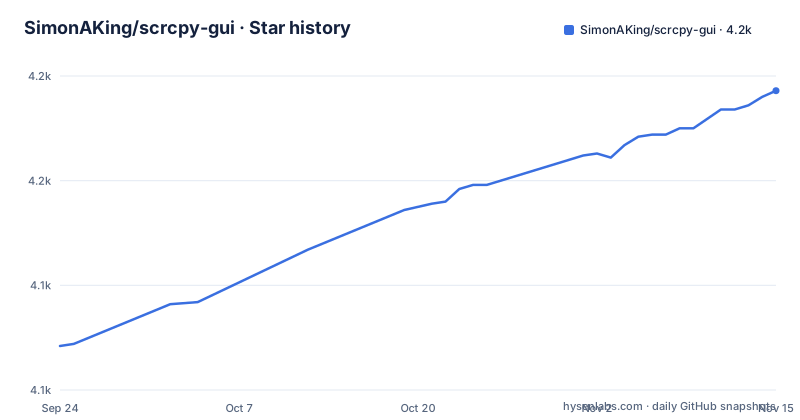
- SimonAKing/scrcpy-gui4,193 ★ · +122
| Repository | 2026-09-24 | 2026-11-15 |
|---|---|---|
| SimonAKing/scrcpy-gui | 4.1k | 4.2k |
122 Stars in the last 52 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The app is unsigned while the runtime inside it is checksum-verified
The security posture here is layered and slightly unusual, so it is worth separating the two things. The release packages include an unmodified, checksum-verified official scrcpy bundle, under scrcpy's own licence, and the documentation states that this exists to make installation easier. That is the part the project verifies. The application's own artifacts are a different story: the current stable ones are explicitly not code-signed or notarised, so the operating system may ask you to confirm that you trust the downloaded application. The project's answer is verification rather than signing. It asks you to check the download against the published checksum file before opening it, and from a recent release onwards also to run an attestation command against the workflow identity. In other words, trust in the container is delegated to a manifest and an attestation rather than to the operating system's signature check.
Bundled tools mean no path configuration, and a fallback search when you override
The requirements section is explicit about how tool discovery works, which is one of the nicer touches in a desktop wrapper. Release packages ship a verified scrcpy and the platform tools, and work without configuring a path at all. If you choose a different scrcpy executable instead, the application searches several places for the platform tools: the directory of the executable you selected, the path, common Homebrew locations, and the standard Android SDK locations. So the override is not all-or-nothing. The version floor matters as much as the search: version two and later requires scrcpy 4.x, and distribution packages may lag behind, which is the reason the bundled copy exists at all. On macOS the documented alternative is a two-package install that brings in both the tool and the platform tools:
brew install scrcpy android-platform-toolsOn Linux the guidance is to use a current package from the distribution or follow the upstream Linux documentation, and on Windows the documented override is to download an official archive, extract it, and select the executable from the settings screen.
Configuration from version one is deliberately not imported
The comparison section with the previous major version contains a decision that will annoy some people and is correct. Existing version one configuration is intentionally not imported, because several old options no longer have the same meaning in the current tool. That is the whole justification for a ground-up rewrite of the interface and the flags at once, and it is the first thing to check if you are upgrading from the older release. The rewrite itself replaced a stack from 2018 and moved from the older tool generation to the current one, and the change list is long: a new interface, current arguments, direct supervision of the launched process, wireless pairing on newer Android, multi-device reliability, diagnostics, security hardening, automated tests and cross-platform release automation. The first stable release of that work is version two point four, which is what the documentation asks you to name when reporting a regression.
Wireless pairing has two addresses, and people mix them up
The wireless instructions are six steps and the fourth and fifth are where it goes wrong. Pairing uses an address and a six-digit code shown on the device, and connecting uses a separate address from the same settings page, and the documentation says plainly that these two ports are usually different. The accepted forms are hostnames, IPv4, bracketed IPv6, and ports across the full range. Every address that connects successfully is remembered, so the second time you do not re-enter it. Two pieces of advice are attached to that memory: rename an entry for clarity rather than leaving it as a raw address, and only enable connecting at startup for addresses that are stable, since that option will retry the connection every time the application opens. Legacy wireless setups are documented separately, using a direct connection over the network rather than the pairing flow.
Device state is shown honestly, including unauthorized
Two features exist specifically to stop people guessing. The first is device state: unauthorized and offline are surfaced as distinct card states, and the wired-connection walkthrough explains that an unauthorized card means the phone is still waiting for you to accept the authorization prompt on the device. That is a real support question, and answering it in the interface removes a round trip. The second is launch status: the application reports real launch status and standard error output instead of claiming success before the launched tool is actually running. For a wrapper whose whole job is starting another program, that distinction is the difference between a useful error and a silent failure. The diagnostics are also part of the support contract, since the documentation asks for the log output, the operating system and the tool version in any regression report.
The renderer is sandboxed and process arguments are handled deliberately
The highlight list names a security posture in one line: a sandboxed renderer, context isolation, restricted inter-process communication, and argument-safe process launching. That last phrase is the one to notice. An application whose job is to assemble a command line and hand it to another program has an obvious injection surface: anything a user types into a settings field that ends up as a command argument. Building the launch as an argument array rather than a shell string removes that class of problem, which is exactly what the wording implies. Context isolation and a restricted communication channel are the other two halves, since an Electron application that reads device names and file paths has a lot to protect. The repository also carries a third-party notices file and a separate frequently asked questions document, both of which are the right place to look for what is bundled. The rest of the highlight list is capability rather than posture: several devices launched at once with duplicate-process protection, named profiles with per-device configuration and aliases, recorded replay of platform-tool actions, the three keyboard modes the upstream tool exposes with a configurable shortcut modifier, video controls for bitrate, size, frame rate, orientation, codec and cropping, and optional notification muting with minimise-to-tray. Four interface languages are shipped. None of that is exotic, and the combination is what makes the wrapper worth installing rather than the individual features.
Six scripts decide what ends up in each platform package
The build scripts are the clearest statement of what a release actually is. Each platform target runs a type check, builds the Electron bundle, then fetches the tool for that platform before invoking the packager, and the packager is told not to publish. The fetch step is the interesting one: it takes a platform name and pulls the matching runtime, which is how one repository produces a Windows package with the Windows tool, a macOS package with the Darwin tool and a Linux package with the Linux tool. The macOS target builds both processor architectures and the Windows target builds both of its architectures in one invocation. Alongside those are the checks: a smoke test for a packaged runtime, one for a prepared runtime, and one for hardware, plus an icon generation script with a check mode. The repository also holds two release smoke reports at two versions, one of which records an explicitly unverified hardware matrix.
Editorial conclusion
Scrcpy GUI suits a user who wants scrcpy's capabilities without memorising its flags, who wants several devices launched at once, and who would rather not configure a path to find the tools. It suits someone on macOS or Linux who would otherwise install a distribution package that lags behind, since the bundled runtime pins the version. It does not suit a Windows or macOS user whose organisation enforces signature checks, because the release artifacts are explicitly not signed or notarised and the system will ask you to confirm trust. It also does not suit someone carrying over configuration from the previous major version, because the project states that old options are intentionally not imported. Before downloading, verify the artifact against the published checksum file and, if you care about provenance, run the attestation command the documentation gives, then confirm your device meets the stated minimum Android version and has USB debugging enabled.
Frequently asked questions
How do I install Scrcpy GUI?
Download the package for your platform from the project's releases: an installer or portable archive on Windows, a disk image or archive on macOS, and an AppImage, Debian package, Arch package or portable archive on Linux. The package includes a verified official scrcpy and adb, so no path configuration is needed.
Is scrcpy GUI safe to install?
The release packages are not code-signed or notarised, so your operating system may ask you to confirm that you trust the application. The project asks you to verify the download against the published checksum file before opening it, and releases from a recent version also include a software bill of materials and build-provenance attestations you can verify from the command line.
Can I mirror my Android device screen to my PC using scrcpy?
Yes. Scrcpy mirrors and controls an Android device over USB or TCP/IP without root access and without leaving an application installed on the device. Scrcpy GUI is a separate front end that discovers devices and launches scrcpy with a configured command line, and the device needs Android 5.0 or later with USB debugging enabled.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/simonaking-scrcpy-gui)Star history chart for your README
[](https://hysenlabs.com/projects/simonaking-scrcpy-gui)Was this useful?