gemini-web2api serves on 0.0.0.0 with authentication off by default, and returns Flash when you ask for Pro
Convert Google Gemini web into OpenAI-compatible API. Zero auth, cross-platform, single file.
At a glance
- What is it?
- A single-file Python service that puts an OpenAI-compatible endpoint in front of the Gemini web interface, with no required dependencies and httpx needed only for streaming. The interesting parts are all in the configuration surface. `api_keys` empty means no authentication at all, `host` defaults to every interface, conversations persist to the account history by default, and the model you request is not always the model you get, because Pro routing silently falls back to Flash.
- Who is it for?
- Check the terms of the Gemini web service before anything else, because this project takes your account's access and spends it through an interface Google does not offer as an API, and the file you configure decides whether that access is anonymous or tied to your paid subscription. Then check four things.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 99 days ago.
- What is it written in?
- Mainly Python, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 21, 2026, and from our analysis. They are not legal advice.
Star history
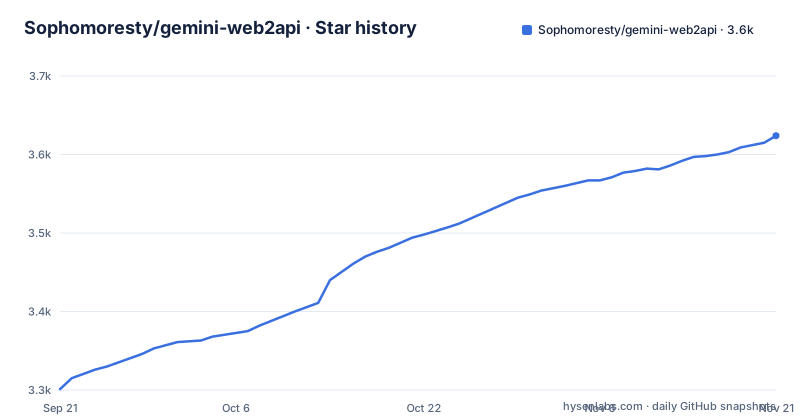
- Sophomoresty/gemini-web2api3,624 ★ · +323
| Repository | 2026-09-21 | 2026-11-21 |
|---|---|---|
| Sophomoresty/gemini-web2api | 3.3k | 3.6k |
323 Stars in the last 61 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The default configuration is an unauthenticated proxy on every interface
Two keys in the configuration decide who can reach the service, and both default to the open option.
`api_keys` is an array. The rule is stated exactly: when `api_keys` is `[]`, authentication is disabled, and when one or more keys are set, the `/v1/*` endpoints require an `Authorization: Bearer <key>` header or an `x-api-key` header. So the empty list is not a locked-down default, it is an explicitly unauthenticated one, and the client configuration table reinforces it by saying the API key can be anything if not configured.
`host` is `0.0.0.0` by default, which binds every interface rather than loopback. The quick start then says the server starts at `http://localhost:8081/v1`, which is the address you use, not the address it listens on.
Put together and the out-of-the-box state is a service with no credential check, bound to all interfaces, on port 8081. The Docker examples publish that port with `-p 8081:8081`, which does not change the binding question but does make it reachable from outside the host.
Two other defaults are worth knowing before you point a client at it. `log_requests` is `true`, so request logging is on from the start. And `temporary_chats` is `false`, which means conversations are persisted to the Gemini account history rather than run as temporary chats, so every call you make through this leaves a trace in that account.
Requesting Pro returns Flash without an error
The model table lists seven identifiers with approximate output lengths, and one of them has a precondition attached. `gemini-3.1-pro` is described as advanced math and code, and marked as needing a cookie, with roughly 12k characters of output. The thinking variant `gemini-3.5-flash-thinking` is the longest at around 20k characters, and `gemini-flash-lite` the shortest at around 10k.
The behaviour when you lack that cookie is the problem. Anonymous access works for all models, but `gemini-3.1-pro` routes to Flash without authentication. And a free Google account cookie will authenticate but silently fall back to Flash.
Two things are wrong with that from a caller's perspective. First, there is no error. A client requesting `gemini-3.1-pro` gets a successful completion, in the Flash shape, with nothing in the response indicating the substitution. Second, the two failure modes are indistinguishable from the outside: no cookie and a non-qualifying cookie both produce Flash, so there is no way to tell from the response whether credentials were checked at all.
For anything that compares models, or that selects Pro deliberately because of the math and code capability, that is a correctness problem rather than a quality one. Check the model actually served rather than trusting the name you sent.
The documentation is otherwise explicit that real Pro routing requires Gemini Advanced, described as a paid subscription, so the capability boundary is stated plainly even though the failure is quiet.
The authenticated path depends on live session credentials
Getting genuine Pro routing means the service acts with a signed-in Google session, and the configuration surface for that is three fields rather than one.
The first is a cookie file, passed with `--cookie-file`, holding six named Google session cookies. These are the credentials that matter here, and they are live account credentials rather than a key you can revoke from a dashboard: they authenticate as the browser session they came from, for as long as they remain valid.
The second is `auth_user`, an account index. It exists because a signed-in Gemini page URL can carry an index such as `/u/1/app/`, and authenticated requests need to select the matching account rather than the default one.
The third is `xsrf_token`. The file states that authenticated web requests may also require the page XSRF token, that in the rendered Gemini page source this token is exposed under a particular internal key, and that the server sends it as the `at` form field. The value shown in the configuration example is truncated. So this design depends on a value scraped out of a rendered page, not on anything Google documents as an API parameter.
There is a stated failure mode, which is helpful. If authenticated requests return HTTP 400 with an `xsrf` error, the instruction is to refresh the Gemini web page, update the token, and confirm `auth_user` matches the `/u/<index>/` part of the browser URL.
A directory named `gemini-cookie-sync-extension/` sits at the top level of the repository, which indicates the cookie is expected to go stale and to need refreshing.
gemini_bl is a Google build identifier with a date inside it
One configuration field is not a setting you choose. It is a build identifier from Google's own frontend, and the default value carries a date and a revision inside it: `boq_assistant-bard-web-server_20260716.08_p0`.
Read that as three parts. A service name identifying the web backend, a date of 20260716 with revision 08, and a shard suffix of p0. It is the kind of value Google's web client sends to its own backend, and this project reproduces it so its requests look like the real client's.
The fragility is structural rather than accidental. Nothing about that identifier is published as a stable interface, so when Google changes its frontend build the value goes stale and the failure mode is a server that still starts and still answers, with responses that are empty or refused. There is no compatibility range to fall back on and no second value to try.
The configuration example shows the same field at a different value from the one in the sample configuration block elsewhere in the file, which tells you it is meant to be edited rather than trusted. The date in the example is close to the last commit in the repository, so whoever maintains this is updating it by hand.
That is the single most important field to check first when responses start coming back empty.
A single file and a package directory share a name, and Docker ships only the directory
The description calls this a single file, and at the top level there is `gemini_web2api.py`. There is also a `gemini_web2api/` directory beside it, so both a module and a package of the same name sit in the same directory.
The two entry points differ, and the documentation uses both. The quick start runs the file directly, after installing httpx:
pip install httpx
python gemini_web2api.py
The packaging metadata takes the other route, declaring a console script named `gemini-web2api` whose target is `gemini_web2api.__main__:main`, which is inside the package directory.
The container picks the package route and ignores the file. The Dockerfile copies `requirements.txt`, installs it, copies only the `gemini_web2api/` directory into the image, copies `config.example.json` to `config.json`, exposes 8081, and starts `python -m gemini_web2api --config /app/config.json`.
So the single file that the description advertises is not in the image, and the image cannot reproduce the quick start. If the file is a thin launcher that delegates to the package, the two are equivalent; nothing in the file says so, and nothing states that the file is generated from the package.
Two more packaging details. `requires-python` is `>=3.8` while the image is `python:3.12-slim`, so the floor is a decade lower than what actually gets tested. And the version is `1.1.0` with no GitHub releases, so there is no tag to pin an install to.
httpx is optional in the package metadata and required in requirements.txt
The dependency story is small, which is the point of the design, and it is described inconsistently in three places.
The package metadata declares no required dependencies at all. `dependencies` is an empty list, and httpx appears only under optional dependencies as the `streaming` extra with a floor of `httpx>=0.25`. Streaming is therefore supposed to be a feature you opt into.
`requirements.txt` contains exactly one line, `httpx>=0.25`, with no comment marking it optional. Anything that installs from that file gets httpx.
The quick start tells you to install httpx before running anything, which makes it a hard prerequisite for the documented path regardless of whether you intend to stream.
So three files describe one dependency three different ways: required by the docs, optional in the metadata, unconditional in the requirements file. If you are packaging this or vendoring it, the metadata is the one to trust, and you can run without httpx if you never touch a streaming endpoint.
The rest of the metadata is conventional: setuptools 68 or newer as the build backend, MIT as `license = {text = "MIT"}`, and the readme pointing at the English file while a `README_CN.md` sits beside it for Chinese.
An @think suffix makes the model name something no OpenAI client will recognise
Thinking depth is controlled by appending a suffix to the model name, with `@think=N` where 0 is deepest and 4 is shallowest, and 0 as the default.
It is a usable convention and it is not compatible with the API being emulated. A model identifier such as `gemini-3.5-flash-thinking@think=2` is not a valid OpenAI model id, so any client that validates model names against what `/v1/models` returned will reject it, and any client that caches the model list will not show it.
The service does present three different surfaces, which widens the compatibility question. The OpenAI-compatible pair is `/v1/chat/completions` and `/v1/models`, described as a drop-in replacement. A Responses API at `/v1/responses` is there for OpenAI Codex integration. And a Google native set at `/v1beta/models`, `:generateContent` and `:streamGenerateContent` is there for Gemini CLI compatibility, configured by pointing `GOOGLE_GEMINI_BASE_URL` at the service and setting `GEMINI_API_KEY` to the literal string none.
Impersonating three client families at once is what makes the tool broadly usable, and it is also why the model naming has to bend. The `@think` suffix is the one place where it bends in a way a strict client will notice.
One naming detail in the table itself: `gemini-3.6-flash` is the latest all-around model and `gemini-3.5-flash` is an alias for it, yet the client configuration table recommends `gemini-3.5-flash-thinking`, so the documented starting point is behind the newest name.
Editorial conclusion
Check the terms of the Gemini web service before anything else, because this project takes your account's access and spends it through an interface Google does not offer as an API, and the file you configure decides whether that access is anonymous or tied to your paid subscription. Then check four things. Whether your listener is reachable, since `host` defaults to `0.0.0.0` and `api_keys` empty disables authentication outright, so the default configuration is an open proxy on every interface. Whether you are getting the model you asked for, since `gemini-3.1-pro` routes to Flash without a qualifying cookie and a free account cookie authenticates without error while still serving Flash. Whether your conversations persist, since `temporary_chats` defaults to false and writes into the account history. And whether `gemini_bl` still matches, because it is a Google frontend build identifier with a date baked into it. Pin a version, since there are no releases to pin to.
Frequently asked questions
What is gemini-web2api?
A Python service that turns the Gemini web interface into an OpenAI-compatible API. It is MIT licensed, version 1.1.0, requires Python 3.8 or newer, declares no required dependencies, and needs httpx only for streaming. It listens on port 8081 and presents three surfaces: `/v1/chat/completions` and `/v1/models`, a Responses API at `/v1/responses`, and the Google native `/v1beta/models` endpoints.
How do I authenticate to gemini-web2api?
Either way. When `api_keys` is an empty list, authentication is disabled and the `/v1/*` endpoints need no header, with the client table noting the API key can be anything if not configured. When one or more keys are set, the endpoints require `Authorization: Bearer <key>` or `x-api-key: <key>`. Separately, `host` defaults to `0.0.0.0`, so the default configuration listens on every interface.
Does gemini-web2api give me access to Gemini Pro?
Not by default. The model table marks `gemini-3.1-pro` as needing a cookie, and the file states that anonymously it routes to Flash, and that a free Google account cookie will authenticate but silently fall back to Flash. Real Pro routing requires a Gemini Advanced paid subscription cookie, so both the anonymous and the free-account cases return a successful Flash response instead.
How do I make authenticated requests work in gemini-web2api?
Three configuration fields are involved. A cookie file passed with `--cookie-file` holding six named Google session cookies, an `auth_user` index matching the `/u/<index>/` part of a signed-in Gemini URL, and an `xsrf_token` which the file says is exposed in the rendered page source under a particular internal key and is sent as the `at` form field. An HTTP 400 carrying an `xsrf` error means refresh the page and update the token.
Does gemini-web2api cost anything?
The project charges nothing and publishes no GitHub releases. Anonymous access works for all models, with listed output lengths from about 10k characters for `gemini-flash-lite` to about 20k for `gemini-3.5-flash-thinking`. The one paid requirement is on the Google side: real Pro routing requires a Gemini Advanced paid subscription, since a free account cookie falls back to Flash.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/sophomoresty-gemini-web2api)Star history chart for your README
[](https://hysenlabs.com/projects/sophomoresty-gemini-web2api)Was this useful?