redis_exporter has three scrape modes, and only one password covers them all
Prometheus Exporter for Valkey & Redis Metrics. Supports Valkey 9.x, 8.x, 7.x and various Redis versions
At a glance
- What is it?
- oliver006/redis_exporter is a Go Prometheus exporter for Valkey and Redis that serves one target on port 9121, switches to a multi-target mode through a /scrape endpoint, and adds cluster discovery behind a flag. Its test environment is a docker-compose file of a dozen servers, and its release images are static binaries running as an arbitrary non-root user.
- Who is it for?
- redis_exporter suits an operator with several Valkey or Redis instances to monitor, since the multi-target and cluster discovery modes exist precisely for that. It does not suit a fleet where every instance has a different password, because one exporter can hold only one --redis.password and the documented workaround is several exporters.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 4 days ago.
- What is it written in?
- Mainly Go, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 14, 2026, and from our analysis. They are not legal advice.
Star history
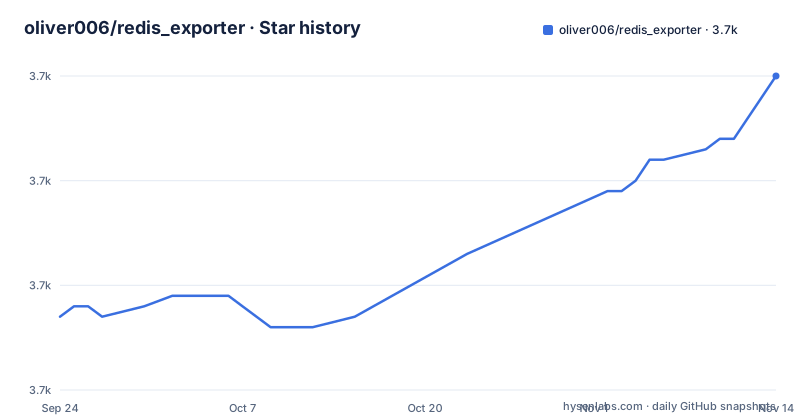
- oliver006/redis_exporter3,720 ★ · +23
| Repository | 2026-09-24 | 2026-11-14 |
|---|---|---|
| oliver006/redis_exporter | 3.7k | 3.7k |
23 Stars in the last 51 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The basic setup is a clone, a build and one scrape block
Building the exporter locally is four commands, and the last one is the version check:
git clone https://github.com/oliver006/redis_exporter.git
cd redis_exporter
go build .
./redis_exporter --version
Pre-built binaries are published on the releases page instead, which is the path most deployments take. Registering it with Prometheus is a single scrape block, and the port is fixed at 9121:
scrape_configs:
  - job_name: redis_exporter
    static_configs:
    - targets: ['<<REDIS-EXPORTER-HOSTNAME>>:9121']
The hostname placeholder is the only value that has to change. The job name is redis_exporter and no path is given, so Prometheus uses the default metrics endpoint. The project describes itself as a Prometheus exporter for Valkey metrics that is Redis compatible, supporting Valkey 7.x, 8.x and 9.x alongside Redis, and it is written in Go.
Multi-target mode replaces /metrics with /scrape and a target parameter
Scraping many instances changes the shape of the configuration, because one exporter process cannot answer for a list of servers on its own. Running it with the command line flag --redis.addr= stops it trying to reach the local instance every time the metrics endpoint is scraped, and the scrape path becomes /scrape, where the instance is a query parameter: http://exporterhost:9121/scrape?target=first-redis-host:6379. The relabel rules do the translation, moving __address__ into __param_target, copying __param_target back into instance, and replacing __address__ with the exporter's own address so Prometheus still talks to the right process. The password is a limitation here: --redis.password means one password across every instance scraped this way, and the project's answer is to run several exporters if that is a problem.
A JSON file of targets works because Prometheus watches the file
Hardcoding a target list in YAML is replaced by file_sd_configs pointing at a JSON file, and the mechanism is that Prometheus uses file watches, so every change to that file is applied immediately without a reload. The file holds a list of groups, each with a targets array of redis URLs and a labels object:
[
  {
    "targets": [ "redis://redis-host-01:6379", "redis://redis-host-02:6379"],
    "labels": { }
  }
]
The same three relabel rules apply, and the scrape job keeps the metrics_path at /scrape. A second job in the same configuration scrapes the exporter itself on port 9121, so the multi-target setup and the plain setup coexist in one file. For TLS targets whose certificate hostname does not match the address in the URL, the fix is to pass tls_server_name to the /scrape endpoint, for example through the Prometheus relabel target __param_tls_server_name.
Cluster discovery needs a flag, an endpoint and a ten minute refresh
Cluster support is opt-in. The exporter must be started with the --is-cluster flag, and only then does it expose a discovery endpoint at /discover-cluster-nodes, which Prometheus consumes through http_sd_configs with a refresh_interval of 10m, so the node list is re-read every ten minutes rather than per scrape. By default the endpoint returns IP addresses. If the cluster runs with --cluster-preferred-endpoint-type hostname and --cluster-announce-hostname set on each node, the exporter can be told to return hostnames instead, either with the --cluster-discover-hostnames flag or with the REDIS_EXPORTER_CLUSTER_DISCOVER_HOSTNAMES environment variable set to true. The documentation notes this matters in container environments, where the node IP is rarely the address you want to see. One extra option is recommended for clusters: -append-instance-role-label, which makes master and replica metrics separable by label.
Kubernetes targets need instance relabelling to be readable
When instances arrive as IPs from Kubernetes service discovery, the result is a list of indistinguishable numbers in the Prometheus user interface. The fix is instance relabelling, and the project points at the general Prometheus documentation for it before giving a concrete example. For metrics scraped through the pod role, the relabel config takes the pod name, replaces the instance label with it, and filters by a regular expression:
          - source_labels: [__meta_kubernetes_pod_name]
            action: replace
            target_label: instance
            regex: (.*redis.*)
The regular expression decides the scope: only pods whose name contains redis are relabelled that way, so the example does not rename every pod in the cluster. The same shape works for other role types, and which one applies depends on how the scrape targets are retrieved in the first place.
The test environment is a compose file full of near-identical servers
The compatibility claim is tested against a fleet rather than a single instance, and the fleet lives in docker-compose.yml. Several Valkey 9 services appear with different shapes: a plain server on 16382 and 6379, a replica that joins it on 16381, a TLS variant on 16386 that mounts certificates from contrib/tls and creates a user named exporter with a password, and a bundle image on 16389. Redis appears at several versions, including 8.6.3 on 16388 and 8.8 on 16488, a password protected instance using --requirepass on 16380, Redis 7.4 on 16385 and a TLS variant on 16387, all launched with protected mode off and debug commands enabled so the exporter can reach them. The Makefile wires these into a docker-all target that brings the environment up, runs the tests in a container and tears it down.
Test URIs encode which connection style is under test
The make test target is a list of environment variables, and the variable names are the test plan. Each server gets a TEST_ variable holding a URI, and the scheme changes with what is being exercised: plain redis:// for a default server, valkey:// for Valkey, rediss:// and valkeys:// for the TLS variants, and a unix socket path for connection tests. Password cases are encoded in the URI itself, one with a password only and one with a user and password, matching the TLS service that creates the exporter user. Cluster coverage has its own variables for a master, a slave and a password protected cluster, and the list also reaches a Tile38 instance. TLS material is not committed: the test-certs target runs contrib/tls/gen-test-certs.sh, which is what generates the certificates the compose file mounts.
The release image is a static binary running as uid 59000
The Dockerfile produces two images from one builder. The builder is golang 1.27 on Alpine 3.24, installs certificates and git, and compiles with CGO_ENABLED=0 for the target OS and architecture, stamping the version, commit SHA and build date into the binary with ldflags while stripping symbols and forcing static external linking. A sanity step then runs the binary with -version on amd64 and falls back to a directory listing elsewhere. The release stage is FROM scratch, which copies only the binary, the certificate bundle and nsswitch.conf, and the Alpine stage copies the binary and certificates. Both declare EXPOSE 9121, both set ENTRYPOINT to the binary, and both run as USER 59000:59000, a non-root user created so the image works in environments that refuse root processes.
Editorial conclusion
redis_exporter suits an operator with several Valkey or Redis instances to monitor, since the multi-target and cluster discovery modes exist precisely for that. It does not suit a fleet where every instance has a different password, because one exporter can hold only one --redis.password and the documented workaround is several exporters. Before wiring it up, decide whether you need the /scrape path or the discovery endpoint, generate TLS test certificates with the contrib script if you are trying the TLS targets, and remember the image runs as uid 59000 rather than root.
Frequently asked questions
What does a Prometheus exporter do?
It exposes metrics from a system in the format Prometheus scrapes. For redis_exporter that means the exporter serves a metrics endpoint on port 9121, and Prometheus is pointed at it with a scrape_configs block whose target is the exporter hostname and that port.
How do I install redis_exporter?
Either take a pre-built binary from the releases page, or build it with Go by cloning the repository, changing into the directory, running go build . and checking the result with ./redis_exporter --version. Then add a scrape_configs block pointing at <<REDIS-EXPORTER-HOSTNAME>>:9121.
What is redis_exporter used for when a server has a password?
The password is set with the --redis.password command line option, and that means one password across all instances scraped through a single exporter. The project states that several exporters should be used if that is a problem, while a JSON file of targets can supply many instances in the multi-target mode.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/oliver006-redis-exporter)Star history chart for your README
[](https://hysenlabs.com/projects/oliver006-redis-exporter)Was this useful?