PyChatGPT: a TLS client for a private API, with two unexplained dependencies
⚡️ Python client for the ChatGPT API with, conversation tracking, proxy support and more.
At a glance
- What is it?
- PyChatGPT talks to the ChatGPT service by reverse engineering it and mimicking a browser with a TLS client, logging in without one and grabbing an access token. Its manifest requires Python 3.9 while its badge advertises 3.8, colourama is declared twice, and it ships a vector and PDF library the feature list never explains.
- Who is it for?
- Use PyChatGPT if you want scripted access to the chat service itself rather than a hosted API, and you are comfortable with a library that follows internal endpoints which the vendor can change without notice. Its own changelog is the best warning: the endpoint action has already been switched once and had to be patched.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 119 days ago.
- What is it written in?
- Mainly Python, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 15, 2026, and from our analysis. They are not legal advice.
Star history
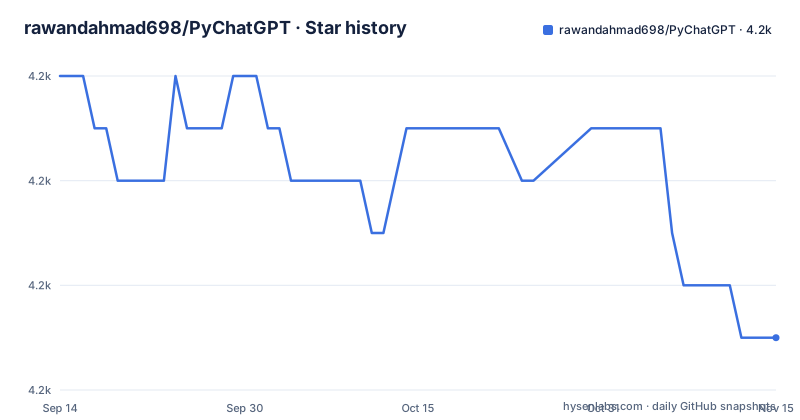
- rawandahmad698/PyChatGPT4,181 ★ · -5
| Repository | 2026-09-14 | 2026-11-15 |
|---|---|---|
| rawandahmad698/PyChatGPT | 4.2k | 4.2k |
-5 Stars in the last 62 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The badge says Python 3.8, the manifest says 3.9
Two version claims sit in the same project and they disagree.
pip install chatgptpy --upgradeThat is the install command, and the badge above it advertises support for Python 3.8. The build manifest requires 3.9 or newer.
The manifest is the one that matters, because it is what a package installer enforces and what the dependency resolution is tested against. The badge is a static image with a hardcoded version in its label, which means it only changes when somebody remembers to regenerate it.
The badges also point at the legacy package index host rather than the current one, in both the Python version badge and the two download counters. Links of that form still redirect, so the counters still work, but they are the kind of thing that stops working quietly one day.
None of this is dangerous. It is the ordinary drift of a small project where the metadata file is generated by a tool and the badges are copied by hand.
Colourama appears twice and two libraries are unexplained
The dependency list is short enough to read in full.
dependencies = [
  "tls-client",
  "requests",
  "colorama",
  "svglib",
  "bs4",
  "colorama",
  "reportlab"
]
Seven entries, six distinct packages, because the colour terminal library is listed twice. A resolver will install it once, so the effect is cosmetic, but it is a sign the list was assembled by appending rather than maintained as a set.
The two interesting entries are at the end. An HTML parser is expected, given the service returns markup. A vector graphics library and a PDF generation library are not, and the feature list never mentions vectors or documents. Whatever they are for, it is not documented in the place a reader would look.
The TLS client is the load-bearing dependency and it is the one the whole approach rests on, which the readme explains at length further down.
The client is coupled to endpoints that are not public
The changelog is where this project tells you how fragile it is.
One entry records that the service switched from one action parameter to another, frequently, and that the library now uses the newer one to fetch the next response. Another records that when the service is overloaded it returns a bad gateway error, and that error handling was added for a missing or corrupt authentication file. A third records that the library has to make a request to the moderation endpoint first, because otherwise the service returns what the author calls a crippled version of the response.
Read together, those three entries say the client is talking to internal endpoints whose names and order are not part of any published contract. The action name changed; the moderation call became a precondition for a usable answer; an overload returns a status code the client has to recognise.
None of that is criticism of the author, who documented each break rather than hiding it. It is a maintenance profile, and it should be weighed against the alternative of a published API with a version number. The library also lists better error handling as a planned item that is still unchecked, which is an honest signal about where the rough edges are.
Working around the login captcha is a listed feature
Two items in the feature list describe the authentication behaviour, and they are worth reading closely.
One is automatic login without involving a browser. The other is getting around the login captcha, with a parenthetical that says if you try to log in subsequently you will be prompted to solve a captcha.
So the library handles the first login and stops there. Any second login, on any account, on any machine, hits the challenge. That makes the behaviour stateful in a way the feature list does not spell out: a token is cached to a file, and the captcha appears when the cache is not there or has expired.
The notes at the end of the readme are the operational advice that follows from this. Use a proxy, and the author recommends doing so always. Do not log in too fast; wait at least ten minutes if you are being rate limited. If the token creation keeps failing, use a VPN, on which the script should work fine.
Three fallbacks, none of them about code, is what a rate-limited private endpoint looks like in practice.
Every call returns three values, and two of them are state
The conversation model is the part of the API a user actually touches.
from pychatgpt import Chat

# Create a Chat object
chat = Chat(email="email", password="password")
chat.cli_chat()
A one-shot question returns three items: the answer, a parent conversation identifier, and a conversation identifier.
Those identifiers are how a conversation survives the process. To resume one, both are passed back into the constructor, and they can also be overridden on any individual call, which lets you fork from an earlier point rather than continuing the current thread. Where you do not want them, the tuple can be unpacked with throwaway names.
Persistence is optional and configured through the options object. There is a switch to track conversations, and two optional file paths for the chat log and the identifier log, both created if missing. The feature list also claims conversations can be resumed after the program is closed, which follows from the identifiers being returned rather than hidden.
The identifier log is also load-bearing: one changelog entry is a fix for reading from it, so a corrupted file broke resumption.
The moderation bypass runs on its own thread and defaults off
One option deserves its own reading, and it is the newest feature in the changelog.
The newest version introduces a parameter on the options object that decides whether the moderation step is skipped. It defaults to false, proxy settings were added to it in the same release, and when it is enabled the function is invoked in another thread so it does not block the main thread.
So there are three separate defaults interacting. The option is off by default, which means the moderation request is made, which is also the call the changelog for the previous version says has to happen first to get an uncrippled response. Turning the option on skips a request the library says it needs.
The threading note is the interesting engineering detail. Whatever the bypass does, it can take long enough that running it inline would stall the interactive session, so it is pushed onto another thread. That is a reasonable design for a CLI where the user is waiting at a prompt.
It is also the feature with the least documentation, since the readme only mentions the option in a commented-out line and links to a discussion thread.
Nine functions and a state token stand between you and an access token
The last section of the readme explains the approach, and it is the clearest statement of what the library is.
The author set out to avoid the usual approaches, which require a Chromium instance running in the background or the developer web inspector to grab a token by hand. Instead the service was reverse engineered and a TLS client is used to mimic a real user, so the script can log in without triggering bot detection.
The reason plain requests are not enough is described next. The identity provider guards each login process with a state token, which is itself a JWT, used both to prevent cross-site request forgery and to prevent bots from logging in. So the client has to participate in that dance rather than just posting credentials.
The implementation is in one module, with over nine functions each responsible for a different task, all working together to produce a token. One detail is called out as having played a huge role: allowing redirects, which lets the login flow navigate as a browser would.
That is also the whole risk profile in one paragraph. The library is correct as long as the flow it mimics stays the same.
Editorial conclusion
Use PyChatGPT if you want scripted access to the chat service itself rather than a hosted API, and you are comfortable with a library that follows internal endpoints which the vendor can change without notice. Its own changelog is the best warning: the endpoint action has already been switched once and had to be patched. Check three things before you build on it. The real Python floor is 3.9, not the 3.8 the badge claims. Conversation handling returns a three-item tuple, so every call site unpacks identifiers you may or may not want to store. And token handling is deliberately aggressive, including an advertised ability to work around the login captcha, which is worth understanding rather than ignoring on any account you care about.
Frequently asked questions
Is there a ChatGPT library available for Python?
PyChatGPT is one, published on PyPI as chatgptpy. It is a client for the chat service itself rather than for a hosted API, logging in by mimicking a browser with a TLS client, and it installs with pip install chatgptpy.
What Python version does PyChatGPT need?
The build manifest requires Python 3.9 or newer, and it requires a recent package installer. The badge in the readme advertises Python 3.8, which the manifest does not match.
How does PyChatGPT log in without a browser?
It uses a TLS client to mimic a real user against the service's own login flow, which is guarded by a state token that is itself a JWT used to prevent cross-site request forgery and bot logins. The implementation lives in a module with over nine functions, and allowing redirects is described as essential to the flow.
How do I resume a conversation in PyChatGPT?
Both identifiers returned by ask are passed back in, either to the constructor or to an individual call, so a thread can be continued or forked. They can also be written to identifier and chat log files, which the library creates if they are missing.
What happens when PyChatGPT cannot get a token?
The readme advises using a proxy, which it recommends doing always, not logging in too fast and waiting at least ten minutes if you are being rate limited, and using a VPN if the problem persists. Token creation also fails on a captcha on any login after the first.
What does the pass_moderation option do in PyChatGPT?
It is the newest option, added in version 1.0.8, and it controls whether the moderation step is skipped. It defaults to false, it accepts proxy settings, and when enabled the function runs in another thread so it does not block the main thread.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/rawandahmad698-pychatgpt)Star history chart for your README
[](https://hysenlabs.com/projects/rawandahmad698-pychatgpt)Was this useful?