picoclaw claims under 10MB in the headline and 10 to 20MB in its own safety notice
Tiny, Fast, and Deployable anywhere, automate the mundane, unleash your creativity.
At a glance
- What is it?
- PicoClaw is a Go personal AI assistant from Sipeed, built to run as one static binary on cheap boards, with chat channels, model providers and the MCP SDK linked into the same process. It suits someone experimenting on a small single board computer, and the project itself says not to put it in production before version 1.0, which is the sentence to read first.
- Who is it for?
- Use it to try a personal assistant on hardware you already own, and read the safety notice as a requirement rather than a disclaimer, because the project states there may be unresolved security issues and asks you to stay off production until 1.0. Do not adopt it on the strength of the memory or boot numbers, since the README gives conflicting figures for both, and check which channels and providers you actually need before you rely on a binary that links all of them.
- Can I use it commercially?
- Yes. MIT is a permissive licence: you can use, modify and sell software built on it, as long as you keep its copyright and licence notices.
- Is it still maintained?
- Yes. The repository last received commits 8 days ago.
- What is it written in?
- Mainly Go, according to GitHub's language statistics.
Answers come from the project's GitHub data, last synced on November 12, 2026, and from our analysis. They are not legal advice.
Star history
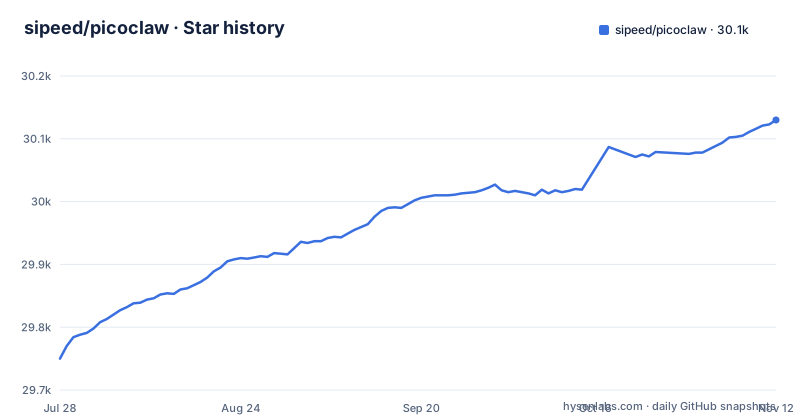
- sipeed/picoclaw30,130 ★ · +380
| Repository | 2026-07-28 | 2026-11-12 |
|---|---|---|
| sipeed/picoclaw | 29.8k | 30.1k |
380 Stars in the last 107 days, measured from the daily GitHub snapshot. Compare with other projects
Editorial analysis
The safety notice says do not deploy this before 1.0
The first thing the front page does after the introduction is warn you about itself, in a callout marked as a caution. It says the project is in early rapid development, that there may be unresolved security issues, and that you should not deploy it to production before version 1.0. The same callout carries a currency warning, stating that no official tokens or cryptocurrency have been issued and that claims about it on trading platforms are scams, and a domain warning, saying the only official site is the one named in the file and that many similar domains have been registered by third parties and should not be trusted. That is an unusual amount of self warning for a project front page, and it is the most useful paragraph in the file. A reader who is evaluating this for anything real has the answer before the feature list, and the impersonation warning is a concrete signal that the project has already been copied.
The memory figure is contradicted three times in the same file
The headline says ten megabytes of memory, the introduction says it runs on ten dollar hardware with under ten megabytes of memory and calls that ninety nine percent less than the other project it compares itself to, and the feature list repeats the figure with a footnote marker. Then the footnote says recent builds may use ten to twenty megabytes because of rapid merge activity, that resource optimisation is planned, and that the boot comparison is based on a specific processor speed. The safety notice repeats the higher figure as well. So the number in the headline is a target, and the file says so twice, in the note and in the warning. The consequence for a reader with a memory constrained board is that the figure to plan with is the higher one, and the difference between the two is roughly a factor of two on the project's own account rather than a rounding difference.
Boot speed is quoted as one multiple in prose and another in the table
The features section claims a boot that is four hundred times faster and under a second even on a slow single core processor. The footnote under the same list, and the comparison table below it, both use a different processor speed for the benchmark, and the table gives the other project as taking more than five hundred seconds against under a second here. Those two numbers imply a factor of more than five hundred, not the four hundred in the prose, and the hardware in the two claims is not the same. The table also compares three projects rather than two, naming the project this one was inspired by, and puts language, memory, boot time and cost in four rows. So the comparison is the most concrete part of the file and also the place where the arithmetic does not quite close.
One binary, and every channel and provider SDK linked into it
The module file is the honest answer to how a small assistant talks to everything. It requires a client library for each chat platform the project supports, including Telegram, Discord, Slack, IRC, WhatsApp, DingTalk, Feishu, Line and a teams notifier, plus MQTT and a WebRTC stack, and on the model side clients for Anthropic, OpenAI, AWS Bedrock and Azure. Alongside those sit a markdown renderer, a QR code renderer for the terminal, a terminal styling library, a pseudo terminal library, a search client, the Model Context Protocol SDK and a self update library. Cross compiling one static binary to four processor families is only possible when nothing needs the C toolchain, and the Makefile's `CGO_ENABLED?=0` default confirms that is the design, so the portability and the lightness are the same decision seen from two ends. The price is a binary carrying every channel whether or not you ever open one.
The build strips symbols and stamps the version into one package path
The build file is where the portability claim is enforced, and it is written for a machine with no network. The C toolchain is disabled by default, which is what makes a static binary possible, two build tags are applied by default, and the toolchain is pinned to the local installation rather than allowed to download a newer one, so your own Go has to satisfy the version the module file names. The build cache and module cache are redirected into a directory inside the project, which keeps a build from writing to shared caches on a small device. Version, commit, build time and the Go version are injected through linker flags into one specific configuration package, and the symbols are stripped; when the version command returns nothing, each of those values falls back to a placeholder.
The example environment file ships a Shanghai timezone and a reaction setting
The example environment file is commented out almost entirely, and that makes what is left unusually telling. There are seven provider variables, including an OAuth variable for a coding tool rather than an API key, then channel tokens for two platforms, then three variables for a third platform where one of them is not a credential at all but a setting for random reaction emoji with a default value of two emoji names. Below that is a search key, and then one line that is not commented out at all: a timezone set to Asia/Shanghai. So the single value a user gets by copying the file is a timezone of Asia/Shanghai; the Feishu reaction setting stays commented out like the rest. The timezone is one edit to change, and it is the kind of default that is easy to inherit without noticing.
The changelog stops two months before the last release
The news section and the release list do not line up. The newest entry in the news is a version from late May, describing a web interface for managing MCP servers, a configurable search backend and a batch of fixes across providers and channels. The newest tag in the release list is a version from the following month, and there is a nightly build dated the day before that. The last push to the main branch is later still, on 2026-10-30. So five months of development is in the repository and absent from the front page, and the tags are the only record of what changed in it. The nightly channel is worth a second look for the same reason: its artefact is older than the release artefact, so the nightly is not currently ahead of the release, which is the opposite of what the label suggests.
Ten translations live in the repository, and only one of them is authoritative
The header carries a language switcher with ten languages, and every one of them is a file inside this repository under the project documentation directory, with English marked as the current one. Keeping translations next to the source is the right call for a project that ships a binary people download. The rest of the documentation follows the same pattern, with a hardware compatibility guide that lists tested boards and invites a pull request for anything missing, a roadmap file, and a single example project. The README header also links a separate documentation site at docs.picoclaw.io and a DeepWiki page.
Editorial conclusion
Use it to try a personal assistant on hardware you already own, and read the safety notice as a requirement rather than a disclaimer, because the project states there may be unresolved security issues and asks you to stay off production until 1.0. Do not adopt it on the strength of the memory or boot numbers, since the README gives conflicting figures for both, and check which channels and providers you actually need before you rely on a binary that links all of them.
Frequently asked questions
What is PicoClaw?
It is a personal AI assistant written from scratch in Go by Sipeed, under the MIT licence, and the file states explicitly that it is not a fork of the other assistant projects it is compared with, though it was inspired by one of them. The design goal is a single static binary that runs on cheap hardware across RISC-V, ARM, MIPS and x86 processors, with the C toolchain disabled so that a single artefact covers all four.
what does picoclaw do
The listed capabilities are native support for the Model Context Protocol so any MCP server can be connected, a vision pipeline that sends images and files straight to the model with automatic base64 encoding, rule based model routing that sends simple queries to lighter models to cut API cost, and a system tray interface on Windows and Linux. Its module file also depends on a self update library.
is picoclaw open source
Yes. The repository is published under the MIT licence and the file describes the project as an independent open source effort initiated by Sipeed, written entirely in Go from scratch. It also warns that the project is in early rapid development, that there may be unresolved security issues, and that you should not deploy it to production before version 1.0.
is picoclaw better than openclaw
The file does not argue that way, but it does publish a comparison table covering language, memory, boot time on a shared processor speed, and cost across three projects including that one. It states separately that it is not a fork of it, and its own safety notice says current builds may use more memory than the headline figure while optimisation is pending.
picoclaw vs nanobot
The file says this project was inspired by that one and then rebuilt in Go rather than extending it. In the comparison table the inspired project is listed as Python, using more than 100 megabytes of memory, booting in more than 30 seconds, running on most Linux boards costing around 50 dollars, against Go, under 10 megabytes, under a second, and any Linux board from 10 dollars.
how to use pico claw
The README's opening sections point to a download page that offers an Android package, to a hardware compatibility guide listing tested boards, and to nine translated READMEs. For building from source, the build file defines build, install, test and integration test targets, and the example environment file is where the provider and channel keys go.
Official sources
Add this badge to your README
If you maintain this project, the badge below links readers to this analysis and shows its maintenance status from the daily GitHub snapshot. Paste the markdown into your README; add ?metric=license or ?metric=stars to the image URL for a different field.
[](https://hysenlabs.com/projects/sipeed-picoclaw)Star history chart for your README
[](https://hysenlabs.com/projects/sipeed-picoclaw)Was this useful?